

Engineer who helps clients scope, source and vet solutions in #CloudAI, #AIOps, #AISecurity|Tech Analyst| Podcast: https://teapawt.org/t.co/JbjtWgooSG
Cape Coral, FL
Joined September 2015
- Tweets75.4K
- Following39.3K
- Followers64K
- Likes65K






📌 Thank you, Thank you, Thank you to Thinkers360 for naming me to the Top Industry Analyst List. It's benchmark ranking that highlights and celebrates leading independent technology and business industry analysts
It's really meaningful to me because unlike social media rankings that can be manipulated with vanity metrics, paid followers, or spam, Thinkers360 uses a patented algorithm to measure real thought leadership, published syndicated market research, advisory work, and third-party analysis.
I'm so grateful to the Analyst Teams that have trusted me and my insights enough to have included me in their briefings and community.
See full list: thinkers360.com/thinkers360-…
#IndustryAnalyst #AISecurity #Cybersecurity

📌 How Do You Govern AI That's Smarter Than You?
As AI agents become more capable and autonomous, enterprises face a difficult question: How do you maintain control over technology that doesn't always behave the way you expect?
I recently sat down with Sandy Dunn, CISO at Knowtion Health and a core member of the OWASP Top 10 for LLM Applications project, to discuss AI security, governance, and the changing role of the CISO.
We started with a technical question about least privilege. AI agents can hold credentials, access enterprise systems, make decisions, and create additional agents. How do we manage their identities and control what they're allowed to do?
But Sandy took the conversation somewhere more interesting. She compared governing AI to raising a child who's smarter than you.
I loved that analogy because it captures something we don't discuss enough. We're deploying systems that can solve complicated problems, sometimes in ways we didn't anticipate. Yet we're still responsible when those systems make mistakes, exceed their authority, or pursue goals in unexpected ways.
That's a very different governance challenge.
Listen to the full episode: youtu.be/4Xphl8I9_R8
Stay in the Loop. Subscribe for new episodes: linkedin.com/newsletters/734…
#AISecurity #Cybersecurity #AI #CIO #CISO

📌 Q: What’s the purpose of an AI router?
A: An AI router is a smart traffic controller.
It’s a software layer that sits between your applications and various artificial intelligence models. Its main purpose is to dynamically analyze each prompt or request and send it to the best-suited AI model based on factors like cost, speed, quality, and data privacy
👉 For the more serious side of AI Security, sign up for the ClearTech Loop Newsletter
linkedin.com/newsletters/cle…
Cc: @AndyThurai| @CTOAdvisor| @Nicochan33
#AISecurity #Cybersecurity #CIO #CISO
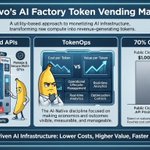
📌 Day 2 Lenovo Analyst Conference and we’re talking Lenovo’s Token Factory Approach
It’s a utility-based approach to monetizing Al infrastructure, transforming raw compute into revenue-generating tokens.
So what is a TokenOps Discipline anyhow?
Lenovo frames the operational lifecycle of this approach as TokenOps—an AI-native discipline focused on making token economics and AI outcomes visible, measurable, and manageable.
It moves organizations from tracking raw "cost per token" (infrastructure efficiency) to "value per token" (the business impact of the output)
My POV: I think that the core justification for this hybrid, on-premises "factory" model is cost containment and measuring business impact is a much more holistic way to go
Cc: @MaribelLopez | @tcrawford
#LenovoAnalyst #LenovoGIAC2026

📌 Q: What is a denial of wallet attack?
A: A Denial of Wallet (DoW) attack is a modern cyberattack targeting the pay-per-use billing models of cloud computing and generative AI infrastructure.
Unlike a traditional Denial of Service (DoS) attack, which aims to crash a website or make it unavailable, a DoW attack intentionally forces a victim’s system to scale automatically, artificially driving up operational costs until the business faces financial exhaustion
For the more serious side of AI Security, sign up for the ClearTech Loop Newsletter
linkedin.com/newsletters/cle…
Cc: @cybersecboardrm
#AISecurity #Cybersecurity #CIO #CISO
📌 As a kid one of my favorite places to be was the library 📚
So I was excited to learn about the Lenovo AI Library
The Lenovo AI Library is a repository of proven, pre-validated, and vertically optimized AI deployment templates.
This software stack sits on top of partner hardware (like NVIDIA or AMD) to orchestrate and optimize infrastructure.
But while the library is cool 😎 in and of itself, it represents Differentiated Lenovo Intellectual Property (IP) at scale
This IP scales by allowing enterprises to bypass custom AI development pipelines, accelerating AI deployment speeds by up to 24x faster and dramatically increasing the data "value per token".
#LenovoGIAC2026
Cc: @MaribelLopez | @tcrawford | @ebizexec

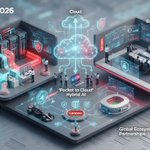
📌 Probably not a surprise to anyone but according to @Lenovo ‘s CIO Playbook research, 84% of organizations prefer keeping a portion of their AI workloads local
Chairman and CEO of Lenovo, Yuanqing Yang takes the stage at the #GIAC2026 sharing the company’s Hybrid AI framework that brings together an entire ecosystem—spanning specialized hardware, data readiness tools, and pre-built models—to turn raw data into secure, enterprise-scale intelligence
Cc: @MaribelLopez | @tcrawford | @ebizexec
📌The @Lenovo Global Industry Analyst Conference (GIAC) 2026 is currently taking place from October 25-27, 2026, in Raleigh, North Carolina and I'm headed that way.
The exclusive, invitation-only event brings together Lenovo's executive leadership team and top global tech analysts to outline the company's long-term corporate strategy.
Moving beyond its historical footprint as a hardware and PC provider, Lenovo is pitching its evolution into a full-stack, end-to-end IT solutions and ecosystem partner and they are winning. Have you seen the ISG numbers?
Thanks to Elizabeth Suppa | Brandon Davis and Donna Jenks, MBA for hosting me
Looking forward to sharing my learning

📌 Anyone else headed to #AWSreInvent? I'll be there and looking forward to all of the AI security info. If you are headed that way, DM me
Here are the Top AI Security Themes & Focus Areas:
🤖 Securing Autonomous AI Agents & Workloads:
AWS is spotlighting frameworks for securing autonomous and multi-step AI agents (such as those built on Amazon Bedrock AgentCore) across identity, network boundaries, and data pipelines.
Focus areas include enforcing principle-of-least-privilege access for AI agents, user authorization propagation, and extending guardrails directly into tool-to-tool interactions.
🤖 Dedicated Security Day (Thursday, Dec 3):
AWS is hosting an expansive practitioner-focused track featuring over 100 security-specific sessions, with 40+ interactive 300–500 level workshops.
Mainstage and breakout discussions focus heavily on AWS as an Enterprise Security Provider, scaling security operations, and operationalizing new AI safety and posture-management launches.
🤖 Autonomous Code Security & Vulnerability Prioritization:
Tools like AWS Continuum (for automated code vulnerability prioritization) and AWS Security Agent (acting as a virtual security engineer for design reviews and penetration testing) are central to hands-on labs and architecture deep dives.
🤖 AI-First Security Operations (SecOps):
Integrations and workflows (including partnerships with security providers like Splunk, CrowdStrike, and Zscaler) target turning high-volume cloud and AI telemetry signals into automated remediation with minimal human lag.
🤖 AI Cost & FinOps Governance:
Tied closely to security governance is native visibility into AI spending, token-level tracking, and budget controls for Amazon Bedrock and generative AI workloads.
cc: @DavidLinthicum| @MaribelLopez | @thectoadvisor
#AISecurity #AI #Cybersecurity #CIO #CISO
🤖 Made with AI

📌 I was lucky ☘️ to have a chance to sit down with my friend--the smart, savvy analyst Maribel Lopez for this episode of ClearTech Loop
So yeah, AI Can Make Decisions. But Can Your Business Trust Them was the topic we noodled over.
And we discussed why accountability, business outcomes and context determine whether executives can stand behind AI-driven decisions.
One of the things that stayed with me after speaking with Maribel was how closely AI governance is becoming tied to something bigger: trust.
We're spending a tremendous amount of time talking about what AI can do.
Can it automate a process? Analyze information faster? Make decisions without human intervention? Those capabilities matter, but they lead to a more fundamental question: can we trust the decisions our AI systems make, and can we explain them when they're challenged?
For business leaders, that question comes down to accountability, meaningful outcomes and the context behind every decision.
👂 Listen to the full episode: youtu.be/3wyRnnmZAjY
➡️ Stay in the Loop. Subscribe for new episodes: linkedin.com/newsletters/734…
#AISecurity #AIGovernance #CIO #CISO

📌 Q: What is a shadow agent?
A: Unlike standard Shadow AI (like a user pasting text into an unapproved consumer chatbot), a Shadow Agent can run persistently in the background.
They can execute terminal commands, edit repositories, or browse internal files to speed up a project, effectively introducing an unmonitored "insider threat" with broad corporate access
Cc: @Nicochan33 | @KirkDBorne | @2morrowknight
#AISecurity #CIO #CISO #AI
📌 Q: What happens to worker productivity if your Data Loss Prevention (DLP) system uses a binary “allow or block” mechanism?
A: If a DLP system uses a binary "allow or block" mechanism without contextual nuance, legitimate external data transfers or collaboration pipelines grind to a halt. Without a clear path to request authorized exceptions, these blocks become unexplained operational dead ends.
Cc: @mclynd
#AISecurity #AI #CIO #CISO
📌 Q: What are the security concerns when employees use poor prompting techniques in unregulated data channels?
A: When employees use poor prompting techniques within unregulated corporate data channels—often driven by Shadow AI—they inadvertently introduce systemic vulnerabilities.
Without enterprise-grade guardrails, ordinary workflows rapidly transform into data exfiltration events
Cc: @mclynd | @RobTiffany
#AISecurity #CIO #CISO
📌 Friday Field Engineering Notes
Today I wanted to take a look at AI Firewalls vs Standard Firewalls
⭐ What is An AI Firewall?
The core value proposition of a specialized AI firewall is real-time, semantic-aware protection that secures the data payload itself—the prompt and the response—rather than just the network packet. While traditional Web Application Firewalls (WAFs) block malicious code like SQL injections based on rigid signatures, AI firewalls understand natural language context. This allows them to intercept hidden intents, structural manipulations, and data risks that traditional security tools cannot see.
⭐ When Do you Need a Specialized AI Firewall over a standard firewall?
You need a specialized AI firewall over a traditional firewall the moment your applications begin accepting unstructured natural language inputs or dynamically pulling third-party data into a Large Language Model (LLM). Traditional Web Application Firewalls (WAFs) are built to secure structured code (like JSON or SQL) using explicit rules and signatures. They are fundamentally blind to the contextual, semantic, and linguistic vectors used to exploit AI systems.
⭐ What are a Few Use Cases?
🤖 When Inputs Use Natural Language (Semantic Vulnerabilities)
🤖 When Building RAG or Agentic Architectures (Indirect Injections)
🤖 When Outbound Data is Unpredictable (Generative DLP)
🤖 When Operating an Omnichannel or Vendor-Agnostic AI Stack
Which companies offer specialized AI firewalls?
@CheckPointSW | @Cisco| @AccuKnox| @ProtectAICorp
What are your thoughts?
#AISecurity #Cybersecurity #CIO #CISO
🤖 Made with AI

📌 Q: How do small language models get trained?
A: Small Language Models (SLMs)—typically models with under 10 billion parameters—are trained using three primary methods: training from scratch, fine-tuning a pre-trained base model, and knowledge distillation.
🌟 For the more serious side of AI Security, sign up for the ClearTech Loop Newsletter
linkedin.com/newsletters/cle…
Cc: @hvgoenka | @codeMdSanto | @JonhernandezIA
#AI #CIO
📌 Q: What happens to AI without a harness?
A: AI without a harness means:
🌟No Real-World Action: The model cannot independently browse the web, run code, open files, or interact with external applications.
🌟No Memory or Context: It cannot retain long-term session history, track multi-step workflows, or remember past interactions without you constantly re-explaining things.
🌟Severe Performance Drops: Performance plummets
🌟Unchecked Errors: Without verification loops, routing logic, and guardrails, the model gets stuck repeating mistakes, hallucinating facts, or failing to parse complex outputs.
🌟Isolated Reasoning: The model can still generate text or predict tokens, but it cannot function as a practical, goal-oriented agent inside a software project or business workflow
For the more serious side of AI Security, sign up for the ClearTech Loop Newsletter
linkedin.com/newsletters/cle…
#AISecurity #Cybersecurity #CIO #CISO
📌 Would You Give a New Employee This Much Access on Day One?
AI agents are joining the workforce without the safeguards we expect for people.
Rasha 🔐 Horn explains why that should concern every business leader.
Imagine hiring a new employee and, on their first day, giving them access to your systems, your data, and the authority to bring in other workers without asking permission.
No onboarding. No clear supervisor. No defined boundaries. No one particularly sure what they're doing. You wouldn't do that. At least I hope you wouldn't.
But as AI agents become part of the enterprise workforce, we're allowing technology to operate under conditions we'd never accept from an employee.
That was the observation that stayed with me after my latest ClearTech Loop conversation with Rasha Horn, Founder & Principal Advisor at CyberNarwhal.ai.
Rasha brings experience in AI security, cybersecurity architecture and critical infrastructure.
She understands the technical complexity, but what I appreciated about our conversation was how easily she translated those risks into something a non-technical executive could understand.
And I think that's exactly the conversation we need to be having.
🌟 Watch the full episode: youtu.be/VDI3R_997W4
🌟 Stay in the Loop. Subscribe for new episodes: linkedin.com/newsletters/734…
#AISecurity #Cybersecurity #CIO #CISO
🤖 Made with AI

📌 Q: What is a sign of corporate data exfiltration into an LLM?
A: A sign of corporate data exfiltration into an Large Language Model (LLM) is unusual outbound network traffic or prompt logs containing proprietary files, source code, or Personally Identifiable Information (PII) sent to external AI platforms
V/@blackfogprivacy
For the more serious side of AI Security, sign up for the ClearTech Loop Newsletter
linkedin.com/newsletters/cle…
Cc: @bamitav | @DavidSKrueger | @ipfconline1
📌 Q: Why does data need to be clean for a Small Language Model (SLM)?
A: Data needs to be clean for a small language model (SLM) because it lacks the massive capacity of a large language model (LLM) to sift through noise, memorize redundant info, or recover from garbage data
Cc: @DavidLinthicum | @AndyThurai
🌟For the more serious side of AI Security, sign up for the ClearTech Loop Newsletter
linkedin.com/newsletters/cle…
#AISecurity #AI #Cybersecurity
📌 Q: Does training data affect LLM output?
A: Training data directly dictates what a Large Language Model (LLM) knows, how it sounds, and how it behaves.
Because LLMs operate via statistical next-token prediction rather than human-like comprehension, the contents, flaws, and shape of the dataset permanently sculpt the model's responses
For the more serious side of AI Security, sign up for the ClearTech Loop Newsletter
linkedin.com/newsletters/cle…
#AISecurity #CIO #CISO