

Official account of MalwareMustDie, NPO & public account @unixfreaxjp Info: https://teapawt.org/t.co/131r5UW4bF Blog: https://teapawt.org/t.co/lUnpKnXOqV
Joined September 2018
- Tweets735
- Following147
- Followers6K
- Likes333




Pinned Tweet
I made online presentation about #ARTEX Signature Detection & its #Playbook, to make it clearer explanation about how we can deal with this type of #AI/#LLM #cyberthreat in the future too. #malwaremustdie
Video: youtube.com/watch?v=hrcIvTZg…
Ref, blog: blog.malwaremustdie.org/2026… & github: github.com/unixfreaxjp/malwa…
☩MalwareMustDie retweeted
My keypoints for all friends followers on #artex sig v1.1.5 update:
1/ People keep asking if #AI/#LLM attackers break behavior detection. They don’t. The agent still has to touch the system to do anything, it just moves faster, so the primitives we already detect still fire. Speed trades stealth for noise.
2/ The loud example is #Kubernetes. Barracuda’s 44-hour intrusion pulled creds straight from K8s, harvested node secrets, swept secrets across namespaces. It's ordinary behavior. The only question was whether anyone had Kubernetes audit on at all or..whether anyone was even watching that layer at all?
3/ So, the gap is "coverage", not "technique". Watch your clusters. #MalwareMustDie!
#Artex #signature detection pack v1.1.5 is out! 6th updates, did it after day work. #BehaviorFirst, #TLP:CLEAR, confirmed+tested. Added:
- #Barracuda’s 44h machine-speed cloud intrusion: CI/CD build steps that encode secrets to slip past job-log masking (B7) &
- A read-only #Kubernetes hostPath container harvesting node creds (B8) plus the widened intentID & wallet hunt
- Deferred: artex.lol re-tier, 0.0.0.0:8788 self-audit, D1 UA/TLS hunt, non-Barracuda chronology rows
Ref: blog.malwaremustdie.org/2026…
Github: github.com/unixfreaxjp/malwa…
Regards! @unixfreaxjp


#Artex #signature detection pack v1.1.4 is out.
Added: #BehaviorFirst: foothold-gated #WinRM/#PsExec lateral-movement correlation from the #ExtraHop thx ScopeWeaver lab, plus two fork user-agents, and now tracking the new Ayven fork (thx!).
Confirmed/append-only/tested/is on #malwaremustdie's GitHub. PS: Detect the behavior, not the name. Rgds/@unixfreaxjp
Notes: blog.malwaremustdie.org/2026…
Github: github.com/unixfreaxjp/malwa…
My keypoints for all friends followers on #artex sig v1.1.5 update:
1/ People keep asking if #AI/#LLM attackers break behavior detection. They don’t. The agent still has to touch the system to do anything, it just moves faster, so the primitives we already detect still fire. Speed trades stealth for noise.
2/ The loud example is #Kubernetes. Barracuda’s 44-hour intrusion pulled creds straight from K8s, harvested node secrets, swept secrets across namespaces. It's ordinary behavior. The only question was whether anyone had Kubernetes audit on at all or..whether anyone was even watching that layer at all?
3/ So, the gap is "coverage", not "technique". Watch your clusters. #MalwareMustDie!
Thank you to #infosec & #journalism communities for recognizing our work!
海外と日本国内のジャーナリズム皆さま、いつも有難う! ai-industry.jp, @BleepinComputer @securityaffairs
ai-industry.jp/trends/fbi-fl…
bleepingcomputer.com/news/se…
securityaffairs.com/203230/h… #malwaremustdie

#SecurityAffairs has published a nice summary of our #artex sigpack work here: securityaffairs.com/203230/h… written by a respected #infosec senior Mr. Pierluigi Paganini @securityaffairs , thank you, sir!
20 new attack nodes within 2hours.. dangerously impressive.. #artex (+artex-like nodes).
src: #shodan. Advise: Start dork shodan/censys & build #blacklist folks, eliminate ip you really don't need to communicate with, #pewpew is on.

#Artex #signature detection pack v1.1.4 is out.
Added: #BehaviorFirst: foothold-gated #WinRM/#PsExec lateral-movement correlation from the #ExtraHop thx ScopeWeaver lab, plus two fork user-agents, and now tracking the new Ayven fork (thx!).
Confirmed/append-only/tested/is on #malwaremustdie's GitHub. PS: Detect the behavior, not the name. Rgds/@unixfreaxjp
Notes: blog.malwaremustdie.org/2026…
Github: github.com/unixfreaxjp/malwa…
4th ruleset update of #Artex signatures pack v1.1.3 (minor) is out. #Playbook for dev works well (no update/v0.4). Added Sophos' X-Ops "HOLD" indicators (finally confirmed), & added Testing.md a #howto test /tools script.
Read: 1)#blog addendum: blog.malwaremustdie.org/2026… and 2)#malwaremustdie github: github.com/unixfreaxjp/malwa… - best regards - @unixfreaxjp
Friends, going forward, how would you like me to handle updates to #Artex detection signature set? (fyi, I have other sec weekdays day job also)
32%Event-based: Immediately
50%On a regular basis/weel
9%No need,we'll do the rest
9%Collaborative,give a hand
22 votes • 2 days ☩MalwareMustDie retweeted
4th ruleset update of #Artex signatures pack v1.1.3 (minor) is out. #Playbook for dev works well (no update/v0.4). Added Sophos' X-Ops "HOLD" indicators (finally confirmed), & added Testing.md a #howto test /tools script.
Read: 1)#blog addendum: blog.malwaremustdie.org/2026… and 2)#malwaremustdie github: github.com/unixfreaxjp/malwa… - best regards - @unixfreaxjp
4th ruleset update of #Artex signatures pack v1.1.3 (minor) is out. #Playbook for dev works well (no update/v0.4). Added Sophos' X-Ops "HOLD" indicators (finally confirmed), & added Testing.md a #howto test /tools script.
Read: 1)#blog addendum: blog.malwaremustdie.org/2026… and 2)#malwaremustdie github: github.com/unixfreaxjp/malwa… - best regards - @unixfreaxjp
Just to put things right:
1/ Many read my #ARTEX signature release as "an IOC list". It isn't. The #IOCs expire within a year by design. The real release is the workflow: how to turn the next ARTEX-style attack into detections as fast as the attacker moves.
2/ ARTEX is an #LLM harness. Swap the model, prompts or infra and every IOC changes. What changes much less is how an agent behaves: machine-speed recon chains, ~1/s #PasswordSprays with rotating UAs, self-correcting API retries, systematic record enumeration.
3/ So the pack is behavior-first. Those patterns live in Sigma correlations, Sentinel KQL and Zeek SumStats on the upper network layers, not in packet filters. IPs are clearly labelled T3/T4 context for retro-hunting what already happened.
4/ The #playbook is the core: verify the source, classify how specific an indicator really is, assign a tier, route it to the right format, expire it. We applied it to four campaigns with an LLM assisting and humans gating every verification step. Next trail, same loop.
5/ That's the big picture: attackers use LLMs to compress weeks into hours. Defenders can use LLMs to compress "new report → tested detection" into hours too, as long as humans keep the verification gates. We must defend atacker's powered LLM/#AI with AI.
6/ The Zeek section shows how to carry the same behavioral logic into network sensors you already run. Playbook, rules and tests: [link]. Break them, send FP/TP reports. That's how this grows.
#BLOG: #MMD-072-2026 - #ARTEX detection signature pack - from #IOC w/#playbook : blog.malwaremustdie.org/2026…
Artex detection signature pack's repo: github.com/unixfreaxjp/malwa…
Read the playbook carefully, asses & test before apply, you can use my python scripts in /tools dir and see /tests result in github repo beforehand. Posted to inspire #block-ing this threat for defenders in FIRST(dot)oeg or xCERTs and xSIRTs. Hope helps. - @unixfreaxjp Nov,2026


#BLOG: #MMD-072-2026 - #ARTEX detection signature pack - from #IOC w/#playbook : blog.malwaremustdie.org/2026…
Artex detection signature pack's repo: github.com/unixfreaxjp/malwa…
Read the playbook carefully, asses & test before apply, you can use my python scripts in /tools dir and see /tests result in github repo beforehand. Posted to inspire #block-ing this threat for defenders in FIRST(dot)oeg or xCERTs and xSIRTs. Hope helps. - @unixfreaxjp Nov,2026
#Blog: #MMD-071-2026 #KinsingBot a "bad-bad"-designed Linux botnet a while ago.. until recent.
blog.malwaremustdie.org/2026…
(I posted this to answer requests on new analysis #education materials. I rendered by chapters accordingly. Thanks for sticking with #malwaremustdie! Enjoy! - @unixfreaxjp, Nov 2026)


BLOG: MMD-0070-2026 - Once upon a time, Linux/Hajime hexstring-pushed a tiny ARM ELF fileless downloader: blog.malwaremustdie.org/2026…
#malwaremustdie (#research & #education purpose)
For followers & IR folks. Updated fakedns python tool with bugfix (for py 2.7) and upgraded to v2 for py 3.11+ compatibilities. Please use it with tests beforehand.
This updates inspired by code originally made by Francisco Santos & I still use it for +/- 20years (since Sat, 15 Apr 2006/thanks) - @unixfreaxjp
PS: feel free to improve.
py 3.11+:github.com/unixfreaxjp/malwa…
py 2.7:github.com/unixfreaxjp/malwa…
#malwaremustdie friends

A lot of improvements in Iaito (radare2)
Now it is as sharp as my katana irl :)
Thank you @radareorg @trufae <3
#MalwareMustDie!

Okay, listen up. THIS (see prev thread) #malware campaign is on-going, even now. Adversaries are in control of these .INFO domains:
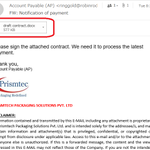
crystalogletree[.]info, coraliereinger[.]info and kevinsaad[.]info, Which they are spreading infection campaign relayed from various IP MTA located in this subnet 160[.]250.128.0/23 at AS150895/EZ TECHNOLOGY CO LTD, I attached. email they used for the infection.
Chains infection:
docx -> rtf -> xml obj #cve-2017-118822 load shellcode to decrypt & load another shellcode to execute malicious script in rtf (there are license.vbs/.js/Client.vbs) that downloads python312x86()zip contains evil Protected(py) to be persistence installed & executed, or execute a DLL binary of "license(.)ini" to be injected to into process.
That evil python is lastly served at sendspace(.)com/pro/dl/5qcr3i
So all of scripts used & binary will be heavily obfuscated. They tried hard to evade all checks and aiming unpatched #EQEDIT on older #msoffice app.
The above #IOC and #CTI info should be their #TTP so use information above to #block ur network in anyway you can.
Just saying, in a glimpse, it seems like adaptation of previously known as #hancitor docx campaign added w/ AI steroid. No, this isn't emotet, and no this is not Heodo/Geodo but could be the copycat.
#MalwareMustDie!!


Well, the adventure continues.. w/same bad-actors (pivoted attackers spambot: 160[.]250.128.165/VN) who's very eager to do more #malware CTF with me.
But.. the endgame is now different...an AI generated hash-obfuscated DLL loader..
See the pics of details & links (it has my hint to crack the hash), below is chain of infections:
docx: virustotal.com/gui/file/467f…
rtf: virustotal.com/gui/file/4289…
DLL loader: virustotal.com/gui/file/1a11…
#MalwareMustDie!


Okay.. this #malware actor's efforts continues. New #email malvertisement w/domain robinrodriguez[.]info via spambot at 161[.]248.238.122 at same AS150895/EZ TECHNOLOGY in #Vietnam, w/same payload "Protected .py" saved in #sendspace camouflaged in a zipped python windows pkg. The evil docx is now using new obfusctated JS loader to exec encoded powershell downloader, triggered by same cve #EQUEDIT exploit. It aims signature evasion, with same infection #backdoor motivation.
See attached pictures for better understanding. Block that sendspace url & final #stager hashes.
docx: virustotal.com/gui/file/fc04…
js: virustotal.com/gui/file/4062…
#MalwareMustDie!


Okay, listen up. THIS (see prev thread) #malware campaign is on-going, even now. Adversaries are in control of these .INFO domains:
crystalogletree[.]info, coraliereinger[.]info and kevinsaad[.]info, Which they are spreading infection campaign relayed from various IP MTA located in this subnet 160[.]250.128.0/23 at AS150895/EZ TECHNOLOGY CO LTD, I attached. email they used for the infection.
Chains infection:
docx -> rtf -> xml obj #cve-2017-118822 load shellcode to decrypt & load another shellcode to execute malicious script in rtf (there are license.vbs/.js/Client.vbs) that downloads python312x86()zip contains evil Protected(py) to be persistence installed & executed, or execute a DLL binary of "license(.)ini" to be injected to into process.
That evil python is lastly served at sendspace(.)com/pro/dl/5qcr3i
So all of scripts used & binary will be heavily obfuscated. They tried hard to evade all checks and aiming unpatched #EQEDIT on older #msoffice app.
The above #IOC and #CTI info should be their #TTP so use information above to #block ur network in anyway you can.
Just saying, in a glimpse, it seems like adaptation of previously known as #hancitor docx campaign added w/ AI steroid. No, this isn't emotet, and no this is not Heodo/Geodo but could be the copycat.
#MalwareMustDie!!