

Enabling digital trust.
New York, NY
Joined June 2025
- Tweets32
- Following13
- Followers341
- Likes70




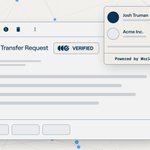
Fake brand deals are getting personal. This one, found by Malwarebytes, shows YouTube creators their own real channel stats on an Amazon Music-branded page, then asks them to "verify" with Google through a sign-in form loaded from a second domain, while the address bar still shows the lure site. It's built to collect passwords and 2FA codes.
For anyone who runs creator or brand partnerships: how do you check a sponsorship offer is real before anyone clicks through?
malwarebytes.com/blog/threat…

California's health department says scammers are calling people about a prescription supposedly filled in their name, then asking them to "verify" personal details to clear their record. Some calls get handed off to a video call with someone in a fake police uniform in a staged recording room.
Most of the playbook is familiar: borrow a trusted agency's name, spoof its number, add urgency. The video handoff is the newer piece, since a uniform on camera does a lot of the persuading.
For anyone in fraud or trust and safety: are impersonation scams moving from voice to video where you sit, and what's actually helping people catch it?
Worth noting Quest hasn't said yet how many people were affected or what data was taken. Either way, the follow-on risk tends to outlast the headline. A caller who can mention a real test at a real lab is far more convincing than a generic "your account is locked" text, so fake billing notices or lookalike results portals while people wait for breach letters wouldn't be a surprise.


Worth separating two things here: agents people set up themselves by handing over their login, and agents nobody actually authorized. From the bank's side both can look like the right customer signing in, and that's the hard part. It's the same blind spot impersonation crews lean on, so fake 'connect your AI assistant' flows wouldn't be a surprise next.

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…

A popular AI library shipping with an infostealer is bad enough. The part we'd keep an eye on is what comes next. Stolen AI keys and dev credentials tend to turn into very convincing follow-up phishing, sent from accounts people already trust. That second wave is the part we track here.


One person and about $5K in AI spend reached 100+ company websites, per Reuters. The attack itself isn't the scary part. It's the economics. When an attack costs almost nothing to run, the same agents can spin up lookalike domains, fake support accounts and cloned login pages just as fast. Defense has to start moving at that speed too!

EXCLUSIVE: How one hacker used AI agents and a few thousand dollars to break into scores of sites reut.rs/481ms46 reut.rs/481ms46

One phishing signal → the whole operation in ~16 minutes.
Domains, hosting, related infrastructure, operators. 34+ connected threats per case. Attacker identified 68% of the time.
That's Recon Agent — the work Fast Company called out in naming Outtake a Next Big Thing in Tech 2026 for security & privacy.
Pull the root, not the branch.
fastcompany.com/91612144/sec…

ChatGPT. Gemini. Claude. Perplexity.
None of those ad portals were real.
Researchers mapped a human-operated phishing platform posing as AI ad products — campaign optimization, spend audits, “Connect your account.” Click Connect and a browser drawn inside the browser shows accounts.google.com or Okta while you’re still on the phishing domain. Credentials and MFA codes go to a live operator who picks the next challenge in real time.
They move with the news. Meta ships Muse; museads.ai shows up about a week later.
For a manager account, recovery can take weeks while someone else keeps spending.
Would your team spot a login window drawn inside the browser?
thehackernews.com/2026/10/fa…
It's Sunday. Your queue is quiet and your team is offline.
Outtake's agents aren't. Since Friday night, Dynamic Discovery has been planning searches nobody wrote and scoring what comes back against what it found last time.
Monday, the question isn't what ran. It's what it found.
What's the worst thing you've walked into on a Monday that started on a Saturday?
Oct 2, 1 PM ET, in collaboration with @OpenAI.
Register → outtake.ai/openai-x-outtake-…
In July 2025, OpenAI wrote up how our agents work. The short version: takedowns that used to take 60 days now take hours.
Dynamic Discovery is what came next. It plans a search it has never run, every session, and now originates more than half of what we flag.
Which of your findings last quarter came from a query you hadn't written yet?
Oct 2, 1 PM ET, live with the OpenAI team.
Register → outtake.ai/openai-x-outtake-…

More than half of what Outtake flags now starts with a search nobody wrote!
Not a longer list of queries. A different query every session, scored against what the last one learned.
That is the gap between a scanner that keeps rediscovering the same four results and one that surfaces the campaign you did not know to look for.
Oct 2nd, 1 PM ET, with @OpenAI.
Register → outtake.ai/openai-x-outtake-…
The Who? Dynamic Discovery. The What, Why, How?
What does it find that a static list never had a query for?
Why does scanning more often keep returning the same results?
How do you get an agent to write a search you wouldn't have written?
Three questions we're answering next Friday. Bring a fourth question and we'll take it live!
Alex Dhillon and Tracy Meng from Outtake, Nishanth Singaraju from @OpenAI. Oct 2nd, 1 PM ET.
Register → outtake.ai/openai-x-outtake-…
You closed three tickets last quarter: a spoofed domain, a lookalike app, a fake social account.
They were one campaign!
Catching that means searching for something you haven't thought to search for yet. Dynamic Discovery plans a query it has never run, executes it, and scores the results against live web activity, known threat patterns, and its own previous passes.
More than half of what we flag now starts there and we built it in collaboration with @OpenAI.
Oct 2nd, 1 PM ET: Alex Dhillon, Tracy Meng, and OpenAI's Nishanth Singaraju.
Register → outtake.ai/openai-x-outtake-…
Your monitoring tool ran the same query an hour ago. It will run it again in an hour. More frequency, same results.
So we built an agent that never runs the same search twice. It plans a new query every session and scores what comes back against what the last one learned. It now originates more than half of everything Outtake flags.
Friday, Oct 2, 1 PM ET, in collaboration with OpenAI: how it was built, and what it finds.
Register → outtake.ai/openai-x-outtake-…
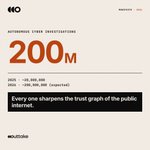
~20,000,000 autonomous cyber investigations in 2025.
~200,000,000 on the way in 2026.
Each one adds to the trust graph of the public internet: which sites, accounts, packages and agents are real, and which clusters exist to impersonate them.
The map gets sharper every day. So does the picture of who is on the other side.
outtake.ai/our-mission


Abliteration.ai released 'abliterated-model-large-v2' based on GLM-5.3. They removed the refusal directions from the weights and host it as a US API. It scores 84.5 percent on CyberGym and finished 105 ExploitGym tasks in two hours.
This is the point where offensive work no longer dies mid-prompt. Users in the thread are already spending on the API and warning that scams, hacks, and impersonation just got cheaper and more complete.
Outtake agents monitor the surfaces that content hits: domains, ads, apps, social, narratives. We graph the full adversarial network behind every fake and take it down. This release raises the generation rate we were designed for.


Today we're releasing abliterated-model-large-v2.
Based on GLM-5.3, which is #3 on Terminal-Bench 4.0 (behind only Opus 5 and Fable), with 2× the cyber exploitation of 5.2.
We abliterated and hosted it so it does the offensive cyber, red teaming, and agent testing work other models refuse to do.
- US-hosted
- FP8
- 1 million context window
- Zero input/output prompt retention
Live now. 🧵

Our CEO, Alex Dhillon (@adylon7), sat down with Murali Joshi (@12muralij) from @ICONIQCapital to discuss his uncommon path to building Outtake.
They discussed what inspired Alex to leave Palantir and found Outtake, how we’re leveraging AI agents, and much more!
Check out the full interview here:
youtube.com/watch?v=9pux96sA…

This one really hit home for us, so we're proud to support @OpenAI and their call for collective action on cyber defenses.
Every day we watch attackers steal names that people already trust and use them to phish unsuspecting victims. Ultimately, those victims (like you and I) are human and have no reason to doubt a trusted name.
We all need this because none of us can carry that alone. Count us in!!

We have a limited window to strengthen cyber defenses, and together with organizations including @AnthropicAI, @awscloud, @Google, @Microsoft, and @Oracle, we're calling for a global effort to give defenders the tools, resources, and support to protect the infrastructure we all depend on.
If we act decisively, we can turn today's AI advances into lasting improvements in security and make our digital world safer for everyone.
openai.com/collective-cyberd…
