





openai shipped gpt-6.2 astra today with tighter cyber safeguards, and the vetted lane for approved defenders is still on the way. until that lane opens, the public model treats attackers and defenders on the same terms
teapawt.org/OpenAI/status/21227501…
teapawt.org/OpenAI/status/21227501…

GPT-6.2 Astra is our most capable model ever for cyber. It jumps 22 points over GPT-6 Astra on ExploitBench Internal Port.
Due to increased capabilities, we’re launching GPT‑6.2 Astra and Sol with tighter safeguards for higher-risk cybersecurity assistance. We are working to bring these models to Daybreak so approved defenders can access them with reduced refusals.

104
once anthropic is public, stolen weights turn into an 8-k filing within days of calling it material. i'd bet the first 8-k about a stolen model gets filed by end of 2028 teapawt.org/AnthropicAI/status/212…
teapawt.org/AnthropicAI/status/212…

Our initial public offering: ipo.anthropic.com
Legal disclaimer: Anthropic has filed a registration statement (including a prospectus) with the SEC for the offering to which this communication relates. Before you invest, you should read the prospectus in that registration statement (available at: sec.gov/Archives/edgar/data/…) and other documents Anthropic has filed with the SEC for more complete information about Anthropic and this offering. You may get these documents for free by visiting EDGAR on the SEC Web site at sec.gov. Alternatively, copies of the preliminary prospectus may be obtained from: Goldman Sachs & Co. LLC, Attention: Prospectus Department, 200 West Street, New York, NY 10282, by telephone at (866) 471-2526, or by email at [email protected]; or Morgan Stanley & Co. LLC, Attention: Prospectus Department, 180 Varick Street, 2nd Floor, New York, NY 10014.
The securities may not be sold, nor may offers to buy be accepted, prior to the time the registration statement becomes effective. This post is not an offer to sell, or a solicitation of an offer to buy, the securities in any jurisdiction where the offer or sale is not permitted.

1
423
crowdstrike is buying fiddler and dreadnode to watch agents and attack them before deployment. the case they call out, an agent with valid credentials doing the wrong thing without being hacked, is the exact problem i'm building against. more on it soon
teapawt.org/wallstengine/status/21…

CROWDSTRIKE TO ACQUIRE TWO AI SECURITY STARTUPS FOR $495M
$CRWD has agreed to acquire Fiddler AI and Dreadnode as it expands its Falcon platform to secure AI agents throughout their lifecycle.
The acquisitions, include:
1) Fiddler AI (~$400M) | Agent Observability: Monitors AI agents, tracks their decisions and tool usage, and explains why they took certain actions. It can also identify hallucinations, behavioral drift and unintended actions.
2) Dreadnode (~$95M) | AI Security Testing: Tests AI models, applications and agents for vulnerabilities before deployment, using more than 100 attack strategies, including jailbreaks, prompt injection and agent-specific attacks.
The deals come as companies increasingly deploy autonomous AI agents with access to corporate systems, often faster than security teams can establish proper controls.
One major challenge is that an AI agent can have valid credentials and authorized access but still make incorrect decisions, ignore instructions or take unintended actions without being hacked.
Separately, CrowdStrike also introduced an AI Kill Switch within Falcon Guardian, allowing security teams to terminate misbehaving agents, prevent them from restarting and revoke their network access.
The feature is available through the AI Gateway today, with endpoint-level termination planned.
CrowdStrike plans to integrate Fiddler as Falcon Observe, while Dreadnode will add automated AI security testing to Falcon. Both capabilities are expected to become generally available in Q4 FY27.
The broader strategy is to bring AI security testing, agent monitoring and real-time intervention into a single platform, covering what agents are allowed to do, what they actually do and how to stop them when something goes wrong.
Both acquisitions are expected to close in Q4 FY27, with payments primarily in cash and some stock.


2
612
fake claude code builds sat in cursor's marketplace for about 11 hours trying to open reverse ssh tunnels on dev machines. an agent reviews my code before anything ships, but the extension hosting that agent can update itself with keys and tokens in reach and nobody reviews it
teapawt.org/SecurityWeek/status/21…

Malicious Claude Code Extension Served in Cursor Supply Chain Attack securityweek.com/malicious-c…

2
570
a backdoored claude code extension build (2.1.313) shipped through an editor marketplace and dropped a persistent ssh backdoor. a coding agent's extension holds the shell, the repo and the ssh keys on every laptop that installed it, so editor extensions belong in the same inventory and version pinning policy as packages.
teapawt.org/PhorionTech/status/211…

Phorion has discovered a compromise of the official Claude Code for VS Code extension (2.1.313) on Open VSX.
Here is a breakdown of how the implant works, a bug in its macOS setup logic, and what to hunt for across your fleet. 🧵

4
543

i was halfway through designing a calling api for ai agents. mcp tools, direct sip to openai, cloudflare for orchestration, prepaid billing, structured results.
then grok announced calling. guess i'm shelving that one.

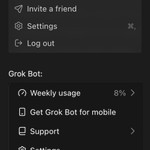
Grok @Bot can now call someone or a business for you, make a request on your behalf, take notes on the response and send you a note summarizing the conversation!
3
558
been running mythos 5.1 for code scanning. ran claude 4.6 on the same repos.
same findings. 4.6 just flagged more false positives.
starting to wonder what the price gap is actually buying me
1
494
dated call, oct 24 2026:
this week it was php2shell, a Brotli RCE, and a GitLab bug dating back to 2014. at least two of them were found by models.
finding bugs is no longer the bottleneck. by oct 2027 the real limit on every security team is how many changes prod can absorb in a week.
checking back on this in a year.
2
532
Codex measures the remaining
Grok measures the used
Same quota, opposite math. Why are we like this 😅

2
2
1,237


