

Beyond testing tools, solutions that deliver expertise. 🌐 Chip & binary security testing https://teapawt.org/t.co/1dUvkjLR8L https://teapawt.org/t.co/BCMLXCF49H
Joined July 2015
- Tweets1.1K
- Following336
- Followers1.9K
- Likes379


We’re publishing a full Android kernel exploit chain built on CVE-2023-20938, a use-after-free in Binder, on a Pixel 6 running Android 12.
👉 Start part 1: eshard.com/blog/kernel-uaf-1…

Kernel UaF to Root, part 3:
Turning the address we leaked in part 2 into a kernel write, on a Pixel 6 running Android 12.
🔗Read: eshard.com/blog/kernel-uaf-t…
Next in our drone security series: having the right security mechanisms doesn't always mean they'll withstand a physical attack.
From encryption to secure boot and readout protection, we explore why testing the actual implementation matters.
eshard.com/blog/drone-securi…

Next week! 🔥 #PQC

Last chance to join our October PQC training. 🚨
2 days, online, hands-on: recover keys via power analysis and fault injection, forge Dilithium signatures with one bit-flip.
Register: eventbrite.fr/e/pqc-physical…
🔥 50% off for students: "STUDENT"

Part 2 of our Android kernel exploit chain (CVE-2023-20938): the stale read returns garbage until you control what reclaims the freed slot.
Land the right object there and it hands back a live kernel pointer instead. That’s your KASLR bypass.
eshard.com/blog/kernel-uaf-2…
In case you missed it: we started publishing a full Android kernel exploit chain built on CVE-2023-20938.
Part 2 is coming soon.
eshard.com/blog/kernel-uaf-1…

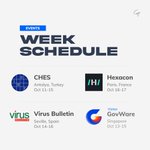
Live from Paris at @hexacon_fr 🔵 We’re here with the team until tomorrow, come say hi!
If you want something to dig into, our Android kernel UaF series is live, and you can explore the trace at ttd.eshard.com


We’re publishing a full Android kernel exploit chain built on CVE-2023-20938, a use-after-free in Binder, on a Pixel 6 running Android 12.
🔗 eshard.com/blog/kernel-uaf-1…
𝚘𝚏𝚏𝚜𝚎𝚝𝚜_𝚜𝚒𝚣𝚎 = 15.
That’s all it takes for Android’s Binder driver to free an object it’s still using.
Part 1 of our CVE-2023-20938 exploit chain: the trigger. Every stage recorded with time-travel debugging, hosted trace included.
🔗 eshard.com/blog/kernel-uaf-1…
Recording a malware sample used to be a long list of manual steps.
Now one sentence to an LLM connected to Epoch covers it all, from a clean isolated VM to a verified, indexed trace.
eshard.com/blog/record-malwa…


What can an adversary actually extract from a captured autonomous system?
Keys, firmware, protocols, algorithms, AI models and more can all become part of the attack surface.
eshard.com/blog/what-can-an-…
Live from CHES in Turkey. 🔵 Come by our booth to discuss PQC implementation security, and meet us at the poster section for the latest research on HQC.


Last chance to join our October PQC training. 🚨
2 days, online, hands-on: recover keys via power analysis and fault injection, forge Dilithium signatures with one bit-flip.
Register: eventbrite.fr/e/pqc-physical…
🔥 50% off for students: "STUDENT"
We tested Botan 3.7.1’s ECC from source code to EM attacks on an iMX 8.
Constant-time on paper wasn’t constant-time on silicon: a timing leak and a table lookup leak both worked on real hardware.
Accepted at HS3 @ ESORICS 2026.
eshard.com/blog/botan-physic…


Lite VM Studio builds a quiet Windows VM from one prompt: emulation CPU drops from 86% to 1.3% of a host core on Windows 10, about 66x less noise.
🔗 See how we did it: eshard.com/blog/lite-vm-stud…
Lite VM Studio builds a quiet Windows VM from one prompt: emulation CPU drops from 86% to 1.3% of a host core on Windows 10, about 66x less noise.
🔗 See how we did it: eshard.com/blog/lite-vm-stud…