

Lead Cybersecurity Architect • Executive and Board Advisor • Keynote Speaker • Professional Storyteller https://teapawt.org/t.co/UW4j471MsT
Joined July 2016
- Tweets3.9K
- Following379
- Followers5.9K
- Likes6.8K



Pinned Tweet
My new video on Security Operations (SecOps/SOC) just dropped!
I cover all the important aspect of SecOps including how AI does 𝘢̲𝘯̲𝘥̲ 𝘥̲𝘰̲𝘦̲𝘴̲𝘯̲'̲𝘵̲ change SecOps.
Share and Enjoy!
youtube.com/watch?v=DX2NehNM…

Use AI to make you smarter, not dumber.
When I said this line to a college class in a guest lecture, I got an amazingly simple and powerful question back from one of the students - How do I do that?
This led me to start writing down my thoughts and experiences
Thread ⬇️

4. Check on how AI is learning to interact with me.
I regularly ask AI to summarize what it thinks about me, including my preferences, patterns, and assumptions so I can review it, consider it, and edit as needed.
⬇️

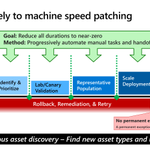
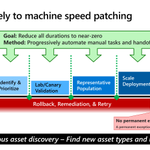
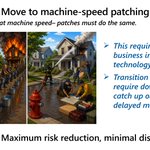
We need to patch faster and automate most of the work, but I have gotten some pushback on the 'machine-speed' terminology.
What terminology do you like? Suggest a better one if you've got one. 👇
(Visual in first reply)
12%Machine-speed patching
25%Accelerated patching
58%Continuous patching
4%Other, please comment
24 votes • Final results

We need to be moving toward machine speed patching.
We have to go from carrying individual buckets to hoses that flow all the time while we keep the humans focused on leaks (exception management)
⬇️

This is hard work to do, but starting later on this work means you have less time to do it.
We need to look at each stage of patching for each type of asset, then find ways to remove the manual human steps in that process.

For your Intune managed devices, check out this guidance - techcommunity.microsoft.com/…

If you're just starting out in cybersecurity, trying to build your career, or navigating the sometimes painful journey of growing in it, you may want to check out my "What's My Job Again?" talk recorded at BSides Tampa.
Check out the talk here - youtube.com/watch?v=uVAAv-mv…


