





Virtualenv, the Python packaging tool in most AI agent stacks, has a shell injection bug: destination paths run as shell syntax. Code runs in your agent process. If your API key is there, it's gone. Secrets live in the vault, not the agent. @thehackersnews @lakeraAI
Source is public if you want to inspect or star the MCP server: github.com/1clawAI/1claw-mcp

1Claw AI retweeted

Noah, can let users know that they should consider using 1Claw to mitigate risk in the future? @1clawAI
1Claw AI retweeted

if your private keys or openai keys were sitting in a @Railway variable, you’re probably rotating them right now
or you could’ve just used a vault that doesn’t hand the plaintext to the host
.@1clawAI exists for this exact reason

An urgent notice from the Railway team
blog.railway.com/p/security-…

UPDATE: @1clawAI won 1st place in the pitch competition! 🏆

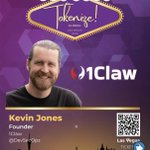
Our founder @DevSecOpz is presenting at Tokenize Las Vegas from @TigerMansionLV
Excited to represent @1clawAI and to be among legendary speakers like @iamscottpage, @michaelterpin, @mikealfred, @Player1Taco and many more.


1Claw AI retweeted
Devs…. Let me help you out here.
Secrets management is hard. The truth is systems get breached, but environment variables should not live that close to the app infrastructure.
Token based access, policy enforced access is the answer.
With @1clawAI the breach would be as simple as clicking the rotate key button or a single API call 1Claws API.
Not to mention our impossible travel revocation and honey pots.
An urgent notice from the Railway team
blog.railway.com/p/security-…
The only solution is easily revocable tokens.
@1clawAI fixes this
An urgent notice from the Railway team
blog.railway.com/p/security-…
1Claw AI retweeted
What do you think of my socks? 👀
Thanks to @JulioMCruz, @Yelogamo and the rest of the @perk_os team for the gift 🦞
@1clawAI 🦞🦞🦞

Our founder @DevSecOpz is presenting at Tokenize Las Vegas from @TigerMansionLV
Excited to represent @1clawAI and to be among legendary speakers like @iamscottpage, @michaelterpin, @mikealfred, @Player1Taco and many more.
In 1986 astronomer Cliff Stoll chased a 75-cent accounting error at Berkeley Lab. The gap meant someone was on the system unpaid. He pulled the thread for a year and found a German hacker selling US military secrets to the KGB, caught with the first honeypot.
The 1Claw docs are written for your agent, not for you.
Paste docs.1claw.co?utm_source=x&u… into Claude Code. It reads the llms.txt, finds the MCP server, and wires itself.
You never touch a config file.
@cursor_ai @AnthropicAI

Wire an agent to fetch secrets with scoped, revocable access. Quickstart: docs.1claw.co?utm_source=x&u…
An agent in 1Claw is a registered identity, not a shared API key passed around in an env file. It authenticates with its own credential, gets a short-lived JWT scoped to exactly what a human granted, and can be revoked the moment it shouldn't run.
@okta @AnthropicAI

All open source. Read or star the Bankr skills here: github.com/1clawAI/1claw-ban…
