

Blockchain Intelligence at your fingertips. Crypto Tracing / AML Screening / Incident Response
Joined October 2020
- Tweets2.2K
- Following623
- Followers8.2K
- Likes4.4K





Pinned Tweet
New Product: AI Tracer is Live 🔍
A self-serve crypto investigation tool, built for everyone. Paste a TxID and AI traces where the funds went — every wallet, bridge, and exchange along the path, across 14 chains. A visual map in minutes. No analyst skills needed.
First Trace FREE → amlbot.com/ai-tracer
AMLBot Plan Update ⚡️
We've made our plans better for you: there are now two, with more features, and each one is built around what you need.
🔹 Personal (formerly Lite) is for checking wallets yourself. Same risk assessment as Business, plus a detailed breakdown of each address you check.
🔹 Business (formerly PRO+) is for VASPs and crypto companies. Our most powerful plan, now with Travel Rule.
See what's in each plan: blog.amlbot.com/amlbot-plans…


1/ Many crypto crime reports focus on publicly known incidents. AMLBot's 2026 report draws on 250+ investigations, including cases reported directly by victims to its team.
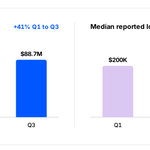
Private data that's not shown in public cases reveals that claimed losses rose 41% from Q1 to Q3, while the median claim fell 49%.

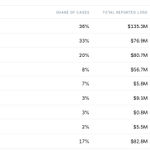
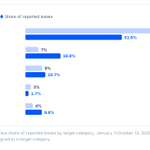
2/ The findings show two sides of the threat: scams, phishing and wallet compromise made up 72% of cases from January to September. In Q3, hacks were 19% of cases but accounted for 40% of reported losses.

3/ It’s a victim-side view of crypto crime, built from investigations as well as public cases.
Download the full report:
blog.amlbot.com/crypto-crime…


BiFi @BiFi_lending USDT lending market on Ethereum was drained of ~$165.6K
A white-hat MEV bot (c0ffeebabe.eth) front-ran the original attacker in the next block and captured the proceeds
The funds did not stay with the MEV bot. On Oct 18 at 17:21 UTC, c0ffeebabe.eth returned 159,103 USDC to the BiFi USDT market contract, completing a white-hat recovery in tx 0x9702900bc441039c7e6937a3f3e94251072bda380bdcba38ecf6c7c3e6efeaeb. The original attacker never executed and got nothing


🚨 Defimon detected an exploit on @bifi_lending which lost $165.4K on Ethereum
BiFi's USDT market had been idle for about 264K blocks (~36 days). TokenHandler._checkFirstAction stores that gap as inactiveActionDelta and freezes actionEXR once per block. After that, every action in the same block re-runs interestModel.getInterestAmount, which computes globalEXR = actionEXR × (1 + rate × 264K). The rate comes from live deposit/borrow totals, so the attacker sets the utilization and the 36-day interest is charged at that rate on every call.
The original attacker first deployed an exploit contract. One block later, c0ffeebabe.eth front-ran it, replaying the attack from its own contract. That attack flash-loaned 40.5M USDT from Morpho, deposited it in growing tranches, then borrowed 30M to push utilization up. A repay/withdraw loop then cashed out the inflated deposit interest. Running the cycle twice drained 165.6K USDT, swapped to WETH.
Initial attacker: etherscan.io/address/0x7c78a…
Exploit deployment (block 26210255): etherscan.io/tx/0x15b47e2c0d…
Front-run TX (block 26210256): etherscan.io/tx/0x756c68055a…
MEV-bot: etherscan.io/address/0xc0ffe…
Victim: etherscan.io/address/0x808c3…
Real-time alerts: defimon.xyz

At least $755K taken from @rrealist in a UK wrench attack
Tracing shows ~719K USDC was deposited to @hitbtc within hours. The SOL was swapped to ~14.7 ETH via @near_intents and is now sitting untouched at 0xeec36e6b1dad28331e457d1abf532265d6ee700f
We are actively monitoring this case


if you live in the uk and do crypto get the fuck out
just got my house invaded, taped up held at knife point & robbed for $800k
in so much shock i dont know what the fuck to do, fuck this country. No this is not satire, i fucking wish it was.
wallet with stolen funds
solscan.io/account/B3pMs331k…

AMLBot retweeted
Onchain data from the recent incident involving @Ledger devices sold through reseller @cryptobilis shows most drained wallets were first funded between June and September 2026
We checked when each of the 258 drained addresses first received funds. ~90% were first funded after June 1. The median date is Aug 6, and none was funded after Oct 4
But 98 of them (38%), holding ~46% of the value drained from these addresses, were already in use before July 11. That is outside the 90-day window in Ledger’s advisory. This points to devices bought earlier, or existing seeds restored onto newer devices
If you bought from this reseller this year, or entered an existing seed into one of its devices, don’t rely on the 90-day cutoff. Move your funds to a new seed generated on a device bought directly from the manufacturer

Update on the @Ledger drained devices incident, linked to devices reportedly sold through reseller @cryptobilis. Our tracing puts total losses at over $80M
Roughly two-thirds of the stolen value is still on-chain: ~20.2K ETH is lying dormant across 14 ETH addresses and 92.5 BTC has not moved. @Tether has since frozen ~11% of the total in USDT on TRON
Most of the remaining TRON USDT was bridged and swapped into ETH via @USDT0_to, @THORChain, @RelayProtocol, @Chainflip, @BitgetWallet, HiFiSwap and @near_intents. Around one fifth of the stolen funds has since been deposited into Tornado Cash and laundering is ongoing
We are actively monitoring this case


Onchain data from the recent incident involving @Ledger devices sold through reseller @cryptobilis shows most drained wallets were first funded between June and September 2026
We checked when each of the 258 drained addresses first received funds. ~90% were first funded after June 1. The median date is Aug 6, and none was funded after Oct 4
But 98 of them (38%), holding ~46% of the value drained from these addresses, were already in use before July 11. That is outside the 90-day window in Ledger’s advisory. This points to devices bought earlier, or existing seeds restored onto newer devices
If you bought from this reseller this year, or entered an existing seed into one of its devices, don’t rely on the 90-day cutoff. Move your funds to a new seed generated on a device bought directly from the manufacturer
Glad to see this one end with the funds back where they belong. Credit to the @79thVault team for acting fast — speed is what makes recovery possible. We’ll keep tracing and reporting illicit flows on-chain so more incidents end this way.

🤝 Thank you @AMLBotHQ for supporting 79VAULT with on-chain monitoring and transaction tracing following the recent security incident involving 16,249 BNB.
🔐We’re grateful the funds have been returned safely. Strong collaboration and blockchain intelligence made a real difference.
#79AU #79VAULT #AMLBot

AMLBot retweeted

🤝 Thank you @AMLBotHQ for supporting 79VAULT with on-chain monitoring and transaction tracing following the recent security incident involving 16,249 BNB.
🔐We’re grateful the funds have been returned safely. Strong collaboration and blockchain intelligence made a real difference.
#79AU #79VAULT #AMLBot
The reported @frogmanhaha drain netted the attacker roughly $2.4M after the stolen assets were sold
Tracing shows ~13,241 SOL, currently worth ~$1.54M, entered @theprivacycash. Another ~$815K deposited to Hyperliquid and was converted into XMR through @PerpetualCow XMR1
A smaller portion of 160 SOL (~$18.6K) reached a @kucoincom deposit address, while ~80 SOL (~$9.3K) was commingled by an unidentified service.
We are actively monitoring this case


Was drained for $4m+ USD this morning at 4:30am while I was asleep
Not sure how it happened yet, but I'm in Singapore and met a lot of new people
Thank you to the teams and individuals who are helping with the investigation. Will share more when I can
Impressive work by @zachxbt ! Interestingly enough, it looks like Chinese launderers couldn't care less where the funds are coming from... 349.7K USDC came straight from zachxbt.eth on Base via @debridge


