

gradatim ferociter
SoCal/AFRL Rosamond
Joined October 2013
- Tweets7.5K
- Following581
- Followers176
- Likes79.1K







Busy with foreign wars guys @NSACyber ?

11/12 - cyberattack on Microsoft
11/13 - cyberattack on US transportation
11/16 - cyberattack on major US banks
we all know what their next target is
1
🧠🧠🧠

这绝对是今年最让人拍案叫绝的硬件逆向神作:安全研究员 Kate 发现英伟达旗舰计算核心 GA100 芯片内部存在一个电压故障注入漏洞(Voltage Fault Injection),并亲手把一张当年矿潮遗留下来的阉割版 CMP 170HX 8GB 矿卡,原地解锁成了满血的 A100-80GB!
当年英伟达为了防止矿工抢占数据中心显卡,拿 GA100 大核心切出了 CMP 170HX 矿卡,不仅在硬件熔丝(Fuses)层面砍掉了显存容量、禁用了 NVLink 高速互联、把 PCIe 降到 Gen1,还锁死了张量计算吞吐。
Kate 顺着 GA100 上电启动读取板载熔丝配置寄存器的微妙时间窗口,用精密控制的电压毛刺(Voltage Glitching)去干扰芯片的熔丝传感放大器——让芯片在自检瞬间把原本烧断的限制熔丝全部误读为 0(未熔断状态),再配合重新植球焊满的高带宽显存,一举解开了英伟达在硅片层面的全部封印:不仅显存认满 81,920 MiB(80GB),连原本被阉割的 PCIe Gen4、NVLink、MIG 切分 也全数复活。
更离谱的是实测性能:因为英伟达在卖零售版 A100 时为了保证晶圆良率,统一锁在了 108 个流多处理器(SM);而这张被毛刺攻击彻底放飞自我的 GA100 核心,居然把晶圆上全部完好的 120 到 126 个 SM 单元 全点亮了,跑出来的真实算力比官方正版 A100 还要快出整整 1.2 倍。

1
8
Phil. retweeted

Move your real SSH service to a random high port, then set up a listener on port 22 that logs every IP address attempting to connect and automatically adds them to your firewall blocklist. Simple 📌
Phil. retweeted

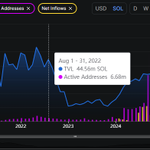
JUST IN: Zelle selects Solana to expand international payments using crypto stablecoins.


Never thought I'll leave the day when real hackers make the anti-virus.

We have released version 3 of our tool, Zero Breach Toolkit, which upgrades it from a spyware scanner to a much more powerful toolkit, capable of scanning your entire home network .
You can download it here: github.com/interplains/Zero-…
Since launch we've added over 1,200 new indicators for 29 more spyware families, like Massistant, EvilBamboo, Dante, GravityRAT, and more - Plus over nine thousand known malicious browser extensions.
We also added 9 tools to help scan and secure your home network, Wifi router, smart TVs, cameras, and discover nearby trackers.
For those that don't want to download anything, you can scan android and iphone backups through your browser, using this link: archivegenocide.com/scan
Just point your browser to the phone backup files, and it will scan without installing or uploading anything.
If you find an infected file on your device, the toolkit will seal it in an encrypted zip file for you, the standard way researchers share samples. Please send us a copy of any samples via Telegram.
This project is fully open source, so feel free to take the code and use it to create your own tools & suggest improvements to us via Github.
Please consider leaving us a star on GitHub if the tool helped you.
Follow our backups: @ZionismExposedx / @IsraelExposedAr
God bless
14
Whoever appoved to place the battery right under the seat should be FIRED !

How many of you would happily take the back seat in this case?
The rear of the Mercedes-Maybach GLS is like a luxurious lounge.
#MercedesBenz #WelcomeHome #140YearsOfInnovation


2



Phil. retweeted

If you want to audit Solana in 2026, learn these in order:
1. The account model: owners, signers, writable, rent, PDAs. This is the foundation. Get this right and understand it deeply.
2. Anchor: what each constraint checks, and what it doesn't
3. The core programs: System, Token, ATA, Token-2022, the upgradeable loader
4. CPIs, and how signer privileges flow through them
5. One AMM, one lending market and one perp DEX, read end to end
6. The bug classes: sealevel-attacks, account lifecycle, remaining_accounts, signature verification
7. The runtime. Go to the agave node github repository and understand how programs are actually executed by a validator.
8. Then hunt: CTFs, contests, bug bounties on live programs
The jump from 7 to 8 is the whole game. Reading about bugs won't make you find them. Looking for them will.
When you have a few real Solana bugs to show, my dms are open.
Phil. retweeted

🚨Attention. Apple spent 5 years building a chip shield. A team using Claude broke it in 5 days.
It is not a leaked government tool. It is not a spyware vendor. It is a small firm called Calif.
May 14: Calif used Claude Mythos Preview to find the bugs and build a macOS kernel exploit past Apple’s Memory Integrity Enforcement on the M5. Under a week.
That model is not public. Only vetted partners in Anthropic’s Project Glasswing can use it.
Calif’s CEO says it is excellent at known attack techniques but cannot invent new ones. The bugs fell fast because they were known classes. Humans still had to beat the shield.
October 16, Paris: an iPhone 18 Pro rebooted on stage, unlocked with a normal passcode, root shell, no computer attached. Same family of shield, bypassed again. Calif has not detailed AI’s role in that chain.
Apple pays up to $2,000,000 for a zero-click chain. Over $5,000,000 with bonuses. It has paid $35,000,000 to 800+ researchers.
iOS 27.2 landed October 26 with 163 fixes. Six credit Calif. Apple’s notes also name Anthropic Research on three fixes and OpenAI on four.
No public tool exists. But phones still on 27.0.1 or 27.1 keep the old attack surface. Settings. General. Software Update. Ten seconds.
The full breakdown is in the article. Almost nobody will read it.


Solana has no single document that sets out its protocol rules. They are spread across years of improvement proposals (SIMDs) and the code of its validator clients.
@anza_xyz's Brennan Watt (@bw_solana) has proposed one living Solana protocol spec instead: each change becomes a pull request against it, merged only when the change goes live on Mainnet.
He has already posted an 18-chapter draft. It is a proposal for feedback; nothing has been adopted.
2
43

RAAN steering can extend the window.

You can't launch a satellite whenever you want.
As Earth turns, the launch site must line up with the path of the orbit the satellite is headed for. That moment is called a launch window and some last only a few minutes.
When you're aiming for orbit, close isn't good enough.
1
1
17

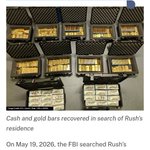
This couldn't have happened without others approving 193M in expenses @FBIDirectorKash


Former Federal Employee Pleads Guilty to Defrauding the Federal Government of Approximately $194 MILLION: Scheme Included the Fraudulent Acquisition of Tens of Millions of Dollars in Gold Bars and Luxury Properties in Florida
“Federal employees are entrusted with serving the American people, not themselves,” said @AGToddBlanche. “The Trump Administration is committed to rooting out waste, fraud, and abuse in the federal government, including by prosecuting those who foolishly defraud American taxpayers.”
🔗: justice.gov/opa/pr/former-fe…

28

But the tunnels under Gaza which had energized conductors couldn't have been discovered from space prior to October 7h, neither the dozens of paragliders @netanyahu ?
Yeah..

Map of 300 years worth of mining tunnels underneath Cornwall, UK.
[Keith Russ / abandonedminemodels. com]
23