

Blockchain security auditing, trusted by Magpie, 1inch, Paraswap, Kodiak, Rango, Orbs, ... (https://xitter.cf/t.co/74XaWrdj3c)
Web3
Joined December 2023
- Tweets165
- Following1.5K
- Followers637
- Likes4.4K




Congratulations to the @feastmeme team on the Feast launch! 🎉 We were glad to audit the contracts, and the full audit report is available here: github.com/astrasecai/audit-…


合约审计报告公开了 🔍
主网上线前,Feast 的合约由 AstraSec 审计:
🟢 严重 0 · 高危 0
🟡 中危 4,全部已处理
⚪ 低危 4,2 项已处理、2 项已知悉
审计能降低风险,但降不到零。报告全文和合约源码都公开,自己查:
📄 feast.meme/audit/2026-10_Ast…
💻 github.com/feastmeme/feast-c…(开源,main 即审计终版)
🚨~$7.8M Gnosis Safe Drain via Flawed Multicall Authorization Check
Root Cause
The root cause was a flawed authorization check in the Multicall contract. Setting the 'target' parameter to address(this) caused the inner 'multicall' to pass the validation because msg.sender (Multicall itself) was one of the authorized callers of the target Safe module (0xea18b). This ultimately allowed attacker-controlled calls to execute on the victim Safe.
Exploit
The attacker used the bypass to move ~2,900 aEthrsETH into a Uniswap V4 pool paired with a worthless “Permissionless Attacker Token” (PAT), leaving the Safe holding only a worthless LP NFT.
The original attack transaction was front-run by the MEV bot yoink, which captured ~2,882 rsETH (~$7.8M) and sent it to 0xC70f00CD7E461686b04B0E912E309becA8b80ea0.
TX: etherscan.io/tx/0x0e7680b06c…


KelpDAO has blocked the address 0xC70f00CD7E461686b04B0E912E309becA8b80ea0 for ~24 hours.
tx: etherscan.io/tx/0xe9deac1fe6…

🚨@ether_fi AtomicQueue contract on Ethereum was exploited for ~15.45 ETH.
Root cause is a combinatorial vulnerability:
- The 'solve()' function allows the caller to freely specify any address as solver. As long as 'solver.finishSolve()' succeeds, the contract executes 'transferFrom()' with no real authorization check.
- Certain victim contracts (e.g. EIP-7702 wallets) implement a default 'fallback()' that returns success for any 'finishSolve()' call.
Any contract that has approved the AtomicQueue and implements a default-successful fallback can become a victim of this vulnerability.
Attack tx: etherscan.io/tx/0x7cbe0b4349…

Huge congrats on 5 years, @RangoExchange!
$9B volume and 0 exploits is an incredible milestone in cross-chain. Honored to be your security partner in the past years and keep building the future alongside you! 🫡🚀

Rango turns 5! 🎂
Thank you to every user, builder and partner who helped us make cross-chain swaps simpler and more secure🫡
Together, we’ve executed over $9B in swap volume, with zero exploits to date🪖
Five years down, The next chapter has started🥂
#BUIDL
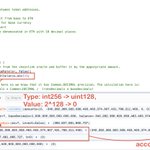
🚨 @NotionalFinance V1 was exploited for ~$1.73M in DAI and USDC. Root cause was an unchecked integer truncation:
the attacker used the official OTC fCash interface to mint a debt of exactly -2^128, and when the protocol priced that debt in ETH it cast a large int256 down to uint128 via 'uint128 absBalance = uint128(balance.abs())'.
Since uint128 maxes at 2^128-1, the value truncated to 0, the account looked debt-free, and the attacker minted unbacked fCash, used it as collateral for DAI/USDC near maturity, then redeemed the real tokens from public Escrow.
txs:
etherscan.io/tx/0xe1589a19fe…
etherscan.io/tx/0xc3f3e318f7…


Notional V1 Security Incident
Notional's legacy V1 contract was exploited last night for ~$1.7M of user funds.
We have identified the vulnerability and paused the affected contract.
No other user assets, including assets in Notional Exponent, are at risk.
We are pursuing all available avenues to recover user funds.
We will provide an update as soon as we have a detailed post-mortem or more important information to share.
Thank you for your patience as we work through this.
🚨 @COLDCARDwallet Entropy Flaw: Urgent Security Advisory
1/ COLDCARD hardware wallets had a serious entropy generation flaw: A 2021 library migration accidentally routed seed generation away from the hardware RNG to a software PRNG. Mk3 effective entropy dropped to ~40 bits, Mk4/Mk5/Q around ~72 bits — far below the 128-bit target.
2/ Critical note: Updating firmware does NOT fix old seeds! Affected users (especially Mk3 on 4.0.1+ without 50+ independent dice rolls) must generate a new seed and migrate funds carefully. Full details in the official technical post.


🚨URGENT COLDCARD SECURITY UPDATE
Read carefully before acting.
👉Mk3 seed generated on 4.0.1+ without ≥50 private, independent dice rolls: begin a careful migration now.
👉Mk4/Mk5 <5.6.0 or Q <1.5.0Q: update first, generate a new seed, then migrate.
blog.coinkite.com/entropy-te…

3/ This isn't isolated. In the past year, several major wallet generation flaws have surfaced:
- Libbitcoin Explorer (bx): Weak Mersenne Twister 32-bit + time-seeded RNG exposed over 120,000 Bitcoin private keys.
- Lubian mining pool wallets: Catastrophic 32-bit entropy allowed brute-force attacks, resulting in massive BTC theft.
- @secondfiapp: Ed25519 nonce flaw made private keys reconstructible from on-chain data, leading to >$2.4M drained and the project shutting down.
🚨 $Pro Token Exploit on BNB Chain – Quick Analysis
@CryptoDAOGlobal 's $Pro was exploited on July 28 via smart contract vulnerability, attacker profited ~$52K.
Root Cause: Flawed slippage control in the exec() function.
Attack Flow:
- Flashloaned $Pro from PancakeSwap and dumped to deflate price
- Looped exec() calls that swapped $Pro with flawed slippage (amountOutMin calculated on manipulated pool state)
- Reversed swap to repay flashloan and pocket USDT
Attacker: 0x427671b2C8e91034A91FE698F9B7259b2345F45D
⚠️ Critical Post-Attack Update:
The team upgraded the contract to restrict exec() calls to validated "executors". However, the core flawed slippage control was NOT fixed. This means the exec() function can still be sandwiched by attackers, unless the exec transaction goes through a private pool.
#BNBChain #Web3Security

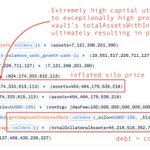
🚨 @summerfinance_'s LVUSDC vault was drained of ~$6M through a nested vault share-price manipulation attack.
Attack flow:
LVUSDC → SiloManagedVaultArk → donated overvalued vgUSDC → bUSDC-155
The attacker exploited prolonged 100%+ utilization in bUSDC-155, inflating its share price from ~0.001 to ~0.55 USDC through massive accrued but uncollectable interest. This inflated value was inherited by vgUSDC → SiloManagedVaultArk → LVUSDC, allowing the attacker to redeem LVUSDC at the inflated price and drain real assets.
📌 Root cause: Naive balance-based accounting + unvalidated downstream share pricing. High utilization + poor price validation = dangerous combination in nested vaults.
tx: etherscan.io/tx/0x0db528c44f…
#DeFi #Hack #SummerFinance

This quoted post is unavailable.
📒Lessons Learned from @edeldotfinance exploit:
Root cause: Price manipulation of ERC-4626 wrapped xStocks. Attacker leveraged two accounts with alternating borrow/supply on wGOOGLx, then used redeem + donation to massively inflate the wGOOGLx:GOOGLx exchange rate. This allowed a supply-only account to borrow large amounts of other assets.
📡Key takeaway for lending protocols: Avoid using share/LP tokens as collateral — their prices are too vulnerable to leveraged manipulation.


An Update from the Edel Team
Earlier today, Edel identified and contained an exploit affecting Edel Lending.
The exploit involved manipulation of the wrapped xStocks exchange rate between wGOOGLx and GOOGLx, causing wGOOGLx collateral to be valued at approximately 78x its correct value. The attacker used that inflated collateral value to borrow from the protocol, creating approximately $403k in protocol bad debt.
Immediately after detection, the Edel team paused all V1 contracts. Edel V1 remains paused, and users should not interact with the V1 deployment while protocol activity is suspended.
The team has preserved the relevant protocol records and is using them to determine affected balances for restoration.
No depositor will bear any loss from this incident. The Edel team will absorb the bad debt and restore affected depositor balances 1:1.
Edel V2 is being deployed with a redesigned oracle architecture intended to prevent this class of exchange-rate manipulation. Once deployment and balance restoration are complete, restored balances will be available directly in the Edel application. We will share timing as soon as it is finalized.
We have traced the attacker’s transactions and are coordinating with exchanges, ecosystem partners, and other relevant stakeholders. In parallel, we have extended a formal whitehat settlement offer to the responsible party, providing a defined window to return the remaining funds in exchange for an authorized security bounty.
A full technical post-mortem will follow with the exploit path, root cause, and the changes introduced in Edel V2.
This incident also reinforces the importance of EIP-01, which will introduce governance over protocol risk parameters, supported collateral, and future market configuration while preserving the team’s ability to respond immediately to security-critical events.
Our immediate priorities are containment, user restoration, and transparent follow-up.
We will continue updating users until affected balances have been restored in full.
The Edel Team
🚨@ThetanutsFi Legacy Index Vault was exploited for ~$105.5K USDC.
Attacker flashloaned most TN-IDX-USDC-PUT tokens, claimed them, and drained nearly all underlying assets — leaving just 3 wei in totalSupply.
They then used multiple crafted mints to generate large amounts of new IDX-USDC-PUT tokens (without depositing any assets), exploiting the mint math (underlying_amount * shares / totalSupply) due to precision loss at near-zero totalSupply.
💡Reminder: Allowing flash-loans on share/LP tokens carries very high risk.
- attacker: etherscan.io/address/0x30498…
- tx: etherscan.io/tx/0xbba9f138fe……


🚨@gnosispay Gnosis Pay Incident: Root Cause Disclosure
While the attack was still ongoing, the team refrained from publishing the root cause. Now that the incident has been fully contained, we believe it is the right time to disclose the root cause.
💡Root Cause
A logic flaw in SignatureChecker::_isValidContractSignature() within the Zodiac Delay Module.
During EIP-1271 signature validation, the function performed a staticcall to the signer contract but only checked the returned data — it did not verify whether the call was successful.
The attacker exploited this by forcing the staticcall to revert, while embedding the EIP1271_MAGIC_VALUE (0x1626ba7e) in the revert data. The flawed checker mistakenly matched the revert payload and treated the failed call as valid authorization.
This bypass allowed the attacker to:
- Queue arbitrary malicious transactions into victim Gnosis Safe wallets (without real permission)
- Wait for the mandatory cooldown period to expire
- Execute them via executeNextTx() and drain funds

