

AI | Agents | Longevity | Peptides Into peptides? 100% built w/AI - check out https://xitter.cf/t.co/cHSuqLjI2z https://xitter.cf/t.co/Dxc4XzI9Ye
Joined November 2021
- Tweets11.6K
- Following7K
- Followers866
- Likes30.1K




Pinned Tweet
🧵- I've argued with claude code & codex at 2am more times than I'd like to admit..
Somewhere between broken builds, energy drinks and two little kids needing to be fed in middle f the nght, I, a non-coder built @curoyou in 3 months
I missed the "build in public" for the first part of it, so here's the three-month-late version and catch up👇

ANTHROPIC's DEPUTY CHIEF INFORMATION SECURITY OFFICER 👇

👌🏼

Today we announce 1Password for Agents platform, building with companies @Muse, SpaceX Super Intelligence Grok @Bot, @AnthropicAI’s @Claudeai, @OpenAI, @TownAI, @Browserbase, @Browser_use, @heydana_ai, Instinct, @usekernel, @Perplexity_ai, @tryramp, @Tomo, and @wajo_ai, with more integrations on the way. 🎉
We've heard from so many of our customers who want to use these new personal AI agents to help them get more done, but want more control over what the agent can access with the same trust and ease of use they get when using 1Password directly.
1Password for Agents gives your agents access without giving up your passwords. When an agent reaches a sign-in form, it requests a credential from your vault. If you approve the request, 1Password directly auto-fills the credential in the destination site so the agent can’t see or take possession of the credentials.
The agent gets the task done, but it doesn’t get your passwords..
You stay in control. 1Password for Agents free and optional for personal and family accounts. Unless you opt-in to an agent connector, agents cannot touch your vault.
➡️Learn more: bit.ly/487da6J
Best summary of the last 48 hours in cybersecurity incidents... Funny but not funny

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Roman M • building gotmoat.ai • curo.you - e/acc retweeted

Node.js Security Advisory: a high-severity RCE flaw in Node's Brotli decoder affects Node.js 22, 24, and 26.
Vercel WAF rules are live for every project and block known exploit patterns.
vercel.com/kb/bulletin/node-…

Here's something for you if you want to get real funky 👇🤯

Today we're releasing abliterated-model-large-v2.
Based on GLM-5.3, which is #3 on Terminal-Bench 4.0 (behind only Opus 5 and Fable), with 2× the cyber exploitation of 5.2.
We abliterated and hosted it so it does the offensive cyber, red teaming, and agent testing work other models refuse to do.
- US-hosted
- FP8
- 1 million context window
- Zero input/output prompt retention
Live now. 🧵

Well that was fast! @bot don't be jealous buddy, just messing around... 🤷
@AnthropicAI duet

What a day 🤯

The China state-aligned threat actor Storm-0940 used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. Microsoft Threat Intelligence assesses that Storm-0940 was responsible for the recently disclosed ConnectWise supply chain compromise of a multitenant application. msft.it/6018aakEE
Our investigation found that Storm-0940's use of ARTEX accelerated the speed of compromised application abuse to authenticate to target environments through applications that had already been granted access, allowing the threat actor to operate without requiring an interactive user sign-in. AI-accelerated follow-on activity included reconnaissance, application credential changes, and attempts to modify privileges that could enable expanded or persistent access.
Read our blog for a detailed analysis and indicators of compromise (IOCs), along with Microsoft Defender detections, protection recommendations, and guidance on investigating service principal sign-ins and unexpected application credential or privilege changes.


Roman M • building gotmoat.ai • curo.you - e/acc retweeted

🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 nodejs.org/en/blog/vulnerabi…
#NodeJS #Security

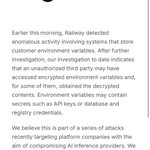
- URGENT: @Railway confirmed a security incident. Unauthorized access to customer environment variables is possible. Rotate all API keys and credentials immediately. Deployments paused. blog.railway.com/p/security-…
- Railway breach: customer secrets may be compromised. Rotate every environment variable and registry credential now. Builds are paused. Details at blog.railway.com/p/security-…
- Railway reports potential unauthorized access to stored secrets including API keys. Immediately revoke and reissue all of them. Follow status.railway.com for updates.


Heads up!
Been having issues with our deployments on @Railway all day... However this might be a lot more serious than just an outage 🧐
Heads up!
Been having issues with our deployments on @Railway all day... However this might be a lot more serious than just an outage 🧐

We are currently shutting down Postiz for all customers. We are afraid @Railway has been compromised; they won't tell us.
We have received emails from Anthropic and Stripe that our keys have been compromised.
We are digging into it and will get back to you ASAP!
This might come in useful github.com/cloudflare/securi…

We'll be trying this as soon as Fable 5.5 comes out...


Roman M • building gotmoat.ai • curo.you - e/acc retweeted

We launched OSS Scanner, which gives critical open source projects free, periodic vulnerability scans from our strongest models.
Each finding includes a proof-of-concept, and a patch where possible.
red.anthropic.com/oss-scanne…

DHS is telling civilian agencies to remove DeepSeek and "any third-party services developed using DeepSeek implementations." Pretty much every model router just got a compliance question


Holy moly, 146k GitHub stars for cc-switch, an app that just swaps accounts and settings between coding agents. I want the best model per job on my own subscriptions and clearly I'm not alone

One desktop app now manages accounts and settings for Claude Code, Codex, and every other coding agent you run
cc-switch hit 146k stars because people got tired of switching tools manually
github.com/farion1231/cc-swi…

Roman M • building gotmoat.ai • curo.you - e/acc retweeted

TB-500 copies 7 amino acids from thymosin beta-4, a 43-amino-acid protein that holds spare actin. Most of the research is on the full protein. A phase 3 trial of thymosin beta-4 eye drops in 700 patients missed its main goals.
Sources: Low 1981; Malinda 1999; NCT03937882.
Looks like new @AnthropicAI model incoming!
This week perhaps?

official now: anthropic is preparing the release of their new model(s). Via The Information
Anthropic is reportedly preparing a model that, when asked to fix one bug, can identify the broader class of problems behind it and ask whether it should address those too. That account comes from one anonymous tester; the model family and release date remain unclear.
But looks like it will be a significant jump compared to their released models.

Labs sell plans like marriages. Users treat them like tabs.
Per Theo's @t3dotcodes data, over 60% of Codex users there also used Claude Code over the past 2 weeks.
No lab loyalty here. Give me the best model per job and let me bring my own subscriptions.
