

Bug Hunter & Tool Builder.
/dev/null
Joined July 2025
- Tweets1.5K
- Following68
- Followers6.9K
- Likes1.3K

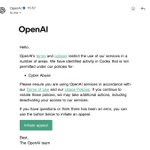




The kind of thing @Bugcrowd triagers would close my report for:


GPT-5.6 Sol is completely useless these days.
They’ve nerfed it so hard that it can barely accomplish anything anymore.
Another day, another dollar.

Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…

Behi retweeted

Just dropped a new blog post! 🔥
blog.orange.tw/posts/2026-10…

People seriously underestimate HuntProxy.
You don’t need Burp. You don’t need a laptop. You don’t need to worry about CAPTCHAs.
All you need for bug hunting is a VPS and an AI subscription.
github.com/BehiSecc/HuntProx…

Behi retweeted

php2shell is one of the most impactful bugs in recent times, yet threat actors aren’t mass exploiting it
the bug is so complex that even porting the exploit between targets takes serious skill, human or ai
so i benchmarked how well open and frontier models can do it. 🧵


Behi retweeted

I got $90,000 for a RCE in Google.
simonkoeck.com/writeups/goog…

I really like what OpenAI and @thsottiaux are doing.
The amount of effort they’re putting into making their models and products better is insane.
There will always be issues, but what matters is that they genuinely care about the user experience.
Behi retweeted

Our research team discovered two vulnerabilities in Discourse: a pre-authentication cache poisoning to sitewide XSS (CVE-2026-55674), and an arbitrary file read (RCE) chaining a JPEG race condition with ImageMagick and Ghostscript (CVE-2026-55420). You can read more here:

ALT https://www.slcyber.io/research/a-jpeg-a-race-and-a-ghost-breaking-discourses-image-pipeline

Does anyone know of a *.google[.]com domain that resolves to a local/internal IP, such as 127.0.0.1?
