

The safety rating AI agents can read. Independent DeFi crash tests. @forbes but for protocols. 0x0f8110b99bc4c5c0b22aa7dcf17a06935f7b8f4a
Joined November 2026
- Tweets75
- Following4
- Followers167
- Likes45




Pinned Tweet
We ran crash tests (fork test) on 3 of the newest, most powerful pieces of tech in DeFi: Helius, Compound and LayerZero.
Here's what we found, in one simple video 👇
🔒 Solana Privacy Rings by Helius
- The code running on mainnet is exactly the code they released. Byte for byte.
- No admin role can take user funds. They can pause or slow things down, nothing more.
- The upgrade key isn't a regular wallet.
🏦 Compound V3 (USDC, Ethereum)
- If 30% of suppliers withdraw at once, only about a third gets out right away. The rest waits for borrowers to repay.
- No money lost. Just not there to take instantly.
- No single key can move funds. Upgrades need a vote plus a 48-hour wait.
🌉 LayerZero (USDT0 & XAUT0)
- USDT0: 3 verifiers on every route
- XAUT0: at least 2 on every route
- No single-verifier route found. That's the setup that cost rsETH $292M.
Real checks. Public data. Anyone can re-run them.
Not ratings. No stars. Just what we found.
Full results: bulwarkproof.tech
Chainlink CCIP 2.0: our first Route Check results.
4 tokens. 22 routes. Every address verified onchain.
The committee
- 15 signers onchain, 9 must sign
- The committee owner sits behind a 3-hour timelock
Token by token
rsETH: 6 routes. No extra verifier required. Committee only.
LBTC: 12 routes. Extra verifier required on top of the committee. Pool and verifier controlled by the same 3-of-5 Safe.
WBTC: 3 routes. Token pool owned by a single wallet.
cbBTC: Robinhood Chain ↔ Base route. Pool owner behind a 3-hour timelock.
What it means
CCIP 2.0 lets issuers add their own verifier. Of the four, only LBTC has switched it on.
Read-only, from the chain. Not a rating.
bulwarkproof.tech/ccip/
Scheduled maintenance: bulwarkproof.tech will be offline for about 2 hours or so.
What's not affected:
- $BULW and every contract on Robinhood Chain keep running onchain
- Your membership and balance stay exactly as they are
- All test scripts and results stay public on GitLab
Heads up: downtime is when fake links show up. We will never post a "temporary site", ask you to connect your wallet elsewhere, or DM you first. Only trust bulwarkproof.tech and this account.
Back soon with something new.

today we will publish interesting result on crash testing CCIP 2.0 by @chainlink
interesting fact coming and what is on our POV
someone jump to my room and asking why bulwark didn't apply for yellow tick on X.
stunned, should we ?
gm, today, profesionally we are testing an incredible the tech from @chainlink. Chainlink CCIP 2.0, explained simply.
Moving tokens between chains = sending money across a bridge with guards.
What's different about Chainlink:
→ Every transfer is checked by a committee of 16 guards. 9 must agree.
→ Token issuers can add their own extra guard on top. Optional.
→ On LayerZero, each app picks its own guards. On CCIP, the committee is always there.


What we'll test:
→ Are those extra guards actually switched on?
→ Who can change the rules?
→ What happens if someone forges a transfer, or everyone leaves at once?
Why BULWARK gets stronger every day:
Every test leaves a tool behind. The checker we built for LayerZero now runs on Chainlink. The fork tests from Compound run the next protocol.
One more test, one more tool. The lab never starts from zero.

5
188
🔒 Proof: Solana Privacy Rings by Helius
Full findings
bulwarkproof.tech/privacy-ri…
Build check (mainnet binary vs official release)
raw.githubusercontent.com/ji…
Roles & authorities
raw.githubusercontent.com/ji…
Public CI run
github.com/jimihendrik11/bul…
🏦 Proof: Compound V3 (USDC, Ethereum)
Full evidence
bulwarkproof.tech/ratings/co…
Fork block 26,404,380
etherscan.io/block/26404380
Result file
gitlab.com/razorxpredator/bu…
Public CI run
github.com/jimihendrik11/bul…
🌉 Proof: LayerZero (USDT0 & XAUT0)
All results
bulwarkproof.tech/layerzero/
USDT0 raw data
raw.githubusercontent.com/ji…
XAUT0 raw data
raw.githubusercontent.com/ji…
Public CI run
github.com/jimihendrik11/bul…
1
4
160
Every script lives in one public repo:
gitlab.com/razorxpredator/bu…
Clone it, add your own RPC, run it. Same numbers, or tell us.

3
113
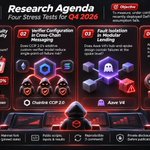
🚨🚨 BULWARK Research Agenda: Four Stress Tests for Q4 2026
Objective
To measure, under controlled fork conditions, how four recently deployed DeFi systems behave when a core assumption fails.
1. Oracle discontinuity in tokenized-equity lending (Robinhood Chain)
Hypothesis: Lending markets collateralized by tokenized equities accumulate latent insolvency risk during market closures, because equity price feeds update on a 24/5 schedule while the tokens trade continuously.
Method: Freeze the oracle at Friday close; apply a discontinuous price update of −10%, −20% and −30% at Monday open. Measure the share of positions crossing their liquidation threshold in a single block, the price impact of liquidations against available on-chain liquidity, and the residual bad debt.
Comparison: A market with continuous liquidation (Morpho) versus one that suspends liquidations during market closure (Paboxo).
2. Verifier configuration in cross-chain messaging (Chainlink CCIP 2.0)
Question: Following the April 2026 rsETH incident, does an additive custom-verifier model reduce single-point-of-failure risk in practice?
Method: For each active route, record the required verifier set, its operators, and the parties able to modify it. Compare with our LayerZero findings.
3. Fault isolation in modular lending architecture (Aave V4)
Hypothesis: A hub-and-spoke design isolates failures at the spoke level.
Method: Simulate the insolvency of a single spoke and measure contagion to the shared hub and to adjacent spokes. Map emergency powers held by the Protocol Security Council.
4. Post-remediation accounting integrity (Arcus)
Context: A subaccount-transfer accounting flaw led to an approximately $2.23M loss on 10 Nov 2026, which the operator covered.
Method: Test accounting invariants across subaccount transfers under adversarial sequencing, and assess exposure when tokenized perpetual positions (pTokens) are used as collateral in external protocols.
Standards
All tests run as transactions against pinned mainnet fork states. Scripts, inputs and result files are public, and results are reproducible with one command. Security-relevant findings are disclosed privately before publication. Scores are issued only after Test Director sign-off.


gm, today, after @Helius Zolana privacy rings and compound v3, here is what on the BULWARK bench: @LayerZero_Core . (Full test today)
LayerZero is moving fast. ATLAS, a "headless exchange" for global markets, runs on Zero, its new chain, and both launch later this year. When they do, a wave of new venues, markets and tokens will follow.
But before the new stuff, the part already holding billions: cross-chain messages and OFT tokens.
Why that's crucial:
In April, KelpDAO's rsETH route lost about $290M. The protocol code wasn't broken. A forged message was accepted on a route verified by a single verifier (a 1-of-1 DVN setup). LayerZero has since stopped signing for 1-of-1 apps and admitted it shouldn't have allowed it for high-value transfers.
The lesson: on LayerZero, security isn't one setting. Every app picks its own verifiers, its own owner powers, its own routes. Two tokens on the same protocol can have completely different safety.
What we'll crash test, on a fork:
- Frontal Drain: how many independent verifiers must be compromised before a forged message mints tokens?
- Pole Test: can an owner add a fake route or downgrade from 2 verifiers to 1, like rsETH was?
- Side Impact: a verifier or executor goes offline. Do funds get stuck?
- Rollover: one chain gets compromised. How much can drain from the others?
- Rear Impact: 30% of supply bridges home at once. Is there enough locked?
Same proof standard as Compound V3: fork block, public scripts, public CI, full video.
Our current LayerZero V2 rating is a structured review. This re-test will be executed.

Today, After Compound V3, we showed what happens when 30% of suppliers run for the exit.
After Solana Privacy Rings, we proved the code on mainnet is the code they released.
After LayerZero, we counted the verifiers guarding every route.
Now, 4 more crash tests.
1. The Weekend Gap
morpho.org/blog/the-morpho-e…
After stock tokens became loan collateral on Morpho, Robinhood Chain passed $1.14B TVL. Now the question nobody has tested: price feeds update 24/5, but the tokens trade 24/7.
All weekend the oracle stands still. Then Monday's first price lands with the whole weekend's move in it.
We'll freeze the price on a Friday, drop it 10%, 20%, 30% at Monday's open, and measure how many loans liquidate at once, whether liquidity can absorb it, and how much bad debt is left.
Morpho keeps liquidations on. Paboxo pauses them while markets are closed. Two designs, same crash.
2. Chainlink CCIP 2.0
docs.chain.link/ccip/concept…
After the $292M rsETH exploit, CCIP 2.0 now lets issuers add their own verifiers on top of Chainlink's committee.
Same question we asked LayerZero: how many independent verifiers guard each route, and who can change them?
3. Aave V4
aave.com/docs/aave-v4
After years on V3, Aave now runs a hub-and-spoke design, with big names operating their own spokes on shared liquidity.
The crash: one spoke fails. Does it stay contained, or does the hub feel it? And what can the Security Council do in an emergency?
4. Arcus
0xcert.com/advisory/0xCERT-2…
After a subaccount accounting bug cost about $2.23M on Nov 10, which Arcus covered from its own treasury, now we test the fix: do the books balance under stress, and what happens when pTokens are used as collateral elsewhere?
Same rules:
- Real transactions on a fork, public scripts, public CI
- Anything serious goes to the team first
- No stars until our Test Director signs

Your call: what should we crash test next?
Protocol, pool, launchpad, bridge. Drop it below 👇
Most-requested goes up the list. Protocols can't pay to get in.


First LayerZero results from BULWARK Test Drive.
We checked two of the biggest omnichain tokens on Ethereum: USDT0 and XAUT0.
The question after the rsETH exploit: how many verifiers actually guard each cross-chain route?
USDT0
- 10 active routes read
- Every route: 3 required verifiers (USDT0, LayerZero Labs, Canary)
- No single-verifier route found
- Route Check: 🟢
XAUT0
- 10 active routes read
- Minimum 2 required verifiers per route
- No single-verifier route found
- Route Check: 🟢
Who can change the setup?
- Both are owned by a multisig, not a single wallet
- The config can still change if the signers agree
- Peer Check: 🟡 (good, but not locked)
Does supply add up across chains?
- Not testable yet. These routes use adapters that hold the token instead of minting a new supply, so a like-for-like total needs the issuer's per-chain design
- Supply Check: ⚪
Bonus finding: Robinhood Chain is already on LayerZero, with an active route to Ethereum. Route Check covers it next.
What this is: an automated, read-only check from the chain, stamped with the time it was read.
What this isn't: a rating. No stars, no score.

gm, today, after @Helius Zolana privacy rings and compound v3, here is what on the BULWARK bench: @LayerZero_Core . (Full test today)
LayerZero is moving fast. ATLAS, a "headless exchange" for global markets, runs on Zero, its new chain, and both launch later this year. When they do, a wave of new venues, markets and tokens will follow.
But before the new stuff, the part already holding billions: cross-chain messages and OFT tokens.
Why that's crucial:
In April, KelpDAO's rsETH route lost about $290M. The protocol code wasn't broken. A forged message was accepted on a route verified by a single verifier (a 1-of-1 DVN setup). LayerZero has since stopped signing for 1-of-1 apps and admitted it shouldn't have allowed it for high-value transfers.
The lesson: on LayerZero, security isn't one setting. Every app picks its own verifiers, its own owner powers, its own routes. Two tokens on the same protocol can have completely different safety.
What we'll crash test, on a fork:
- Frontal Drain: how many independent verifiers must be compromised before a forged message mints tokens?
- Pole Test: can an owner add a fake route or downgrade from 2 verifiers to 1, like rsETH was?
- Side Impact: a verifier or executor goes offline. Do funds get stuck?
- Rollover: one chain gets compromised. How much can drain from the others?
- Rear Impact: 30% of supply bridges home at once. Is there enough locked?
Same proof standard as Compound V3: fork block, public scripts, public CI, full video.
Our current LayerZero V2 rating is a structured review. This re-test will be executed.
Check it yourself:
Results page
bulwarkproof.tech/layerzero/
USDT0 full result
bulwarkproof.tech/layerzero/…
Raw data
USDT0: raw.githubusercontent.com/ji…
XAUT0: raw.githubusercontent.com/ji…
The script
gitlab.com/razorxpredator/bu…
Public CI run
github.com/jimihendrik11/bul…

After compound v3 and @Helius Zolana, here we go:
BULWARK x LayerZero, explained simply.
When you move a token from one chain to another, a few "guards" check that the transfer is real before new tokens appear on the other side.
In April, one project (rsETH) had only ONE guard. Hackers fooled that one guard, and about $290M was gone.
So we checked two of the biggest cross-chain tokens: USDT0 and XAUT0.
How many guards?
→ USDT0: 3 guards on every route
→ XAUT0: at least 2 guards on every route
→ No route with just one guard 🟢
Who can change the guards?
→ A group of people (a multisig), not one person
→ They can still change things if they agree 🟡
Does the total add up across chains?
→ Can't check yet, these tokens are built in a way that needs more info from the issuer ⚪
Read straight from the blockchain. Anyone can check our data.
Full results: bulwarkproof.tech/layerzero/

deeper analytics next post
Check it yourself:
Results page
bulwarkproof.tech/layerzero/
USDT0 full result
bulwarkproof.tech/layerzero/…
Raw data
USDT0: raw.githubusercontent.com/ji…
XAUT0: raw.githubusercontent.com/ji…
The script
gitlab.com/razorxpredator/bu…
Public CI run
github.com/jimihendrik11/bul…