

Sometimes I build things. Certified has-been: SuperSU (100M's of devices), DSLR Controller (first mobile USB control), WMWifiRouter (first mobile hotspot ever)
Netherlands
Joined May 2009
- Tweets9.7K
- Following530
- Followers127K
- Likes28


Chainfire retweeted

Someone is putting the law of every country into one git history.
Git for Global Law turns each country's laws into a repository where every commit is a real law taking effect. So you can see exactly what the law said on any date, and which law changed every word.
It started with the US Code, which hit #1 on Hacker News. The global version is growing country by country: Germany's constitution since 1949, Estonia and more so far.
Free to use for anything, and perfect for feeding to an AI.
github.com/lexifina/global-l…

Chainfire retweeted

Your next trip: a flight to another world. 🪐
Send your name aboard NASA’s Dragonfly mission to Saturn’s largest moon Titan and get a personalized boarding pass for the journey.
Become a Dragonflyer today: go.nasa.gov/dragonfly-names

ALT Poster with a peach-and-gold background that reads “Journey to Titan” in bold orange text, with a banner beneath it that says “Fly your name to another world!” Below the headline, NASA’s Dragonfly rotorcraft flies through a hazy sky with its rotors spinning, with faint hexagon patterns in the background.
Chainfire retweeted
In lieu of flowers, memorial contributions may be made to:
Johns Hopkins Alzheimer’s Disease Research Center Fund
alzresearch.org/giving/
Alzheimer’s Foundation of America Caregiver Resources
alzfdn.org/donate/
Photo Credit: Tommy Garcia


Chainfire retweeted

Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
foxio.io/blog/choose-your-ba…

Chainfire retweeted

One of the biggest mysteries of the Wow! Signal is its exact location, with two possible positions in the sky. Our #AreciboWow team has solved this mystery using three independent methods. We’ll present our findings in 2027.
We know! 😉


Chainfire retweeted
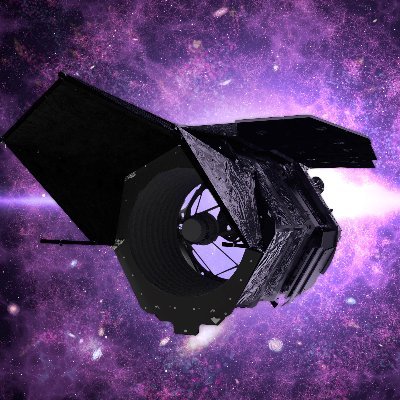
It's the final countdown 🎶
We're one step closer to Roman's first images! The observatory is now fully functional and the team is performing their final checks and calibrations before starting science observations.
go.nasa.gov/4A9menV
Chainfire retweeted

How do you end up getting a job as the BBC’s cyber correspondent without having heard of PHP?

Chainfire retweeted
The PHP RCE details are out. php.net/archive/2026.php#202…
php.net/
21 Oct 2026
Security advisory: Critical remote code execution vulnerabilities, update now
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to update immediately.
Who is at risk: all PHP installations serving web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. We consider the risk highest for mod_php, with a demonstrated exploit where an unauthenticated request can trigger the attack before any application code runs.
The vulnerabilities:
RCE via OOM corruption, CVE-2026-109618 (GHSA-w8hw-w9fx-j79w): out-of-memory handling can interrupt PHP while internal request data is only partially initialized. Request cleanup may then treat the invalid data as valid.
RCE via stale global state, CVE-2026-109619 (GHSA-6wmf-4rv5-p3rp): request-owned internal state can survive after its backing memory has been freed. A later request handled by the same worker may use that stale state before normal initialization resets it.
How to update:
Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35. Source downloads are on our downloads page. Windows source and binaries are on the same page.
Linux distributions and LTS vendors received the patches in advance, so check your vendor for updated packages.
PHP 8.1 and older no longer receive updates from the PHP project. Some distributions and LTS vendors provide backported fixes, so contact your vendor for details, or upgrade to a supported version.
If you rely on the volunteer-maintained rpms.remirepo.net, we urge you to switch to distribution packages or build from source, so you can immediately apply updates. The repo will not have updates today.
Given the severity of these vulnerabilities, the PHP security team provided minimal source-backports for PHP 7.4, PHP 8.0, and PHP 8.1 to help people building from source or without access to an LTS vendor.
If you cannot update immediately: while only an update is a complete solution, the following measures reduce exposure to specific attack paths but do not make an installation safe.
RCE via OOM corruption (CVE-2026-109618):
Set memory_limit=-1, preferably in a way applications can't override, such as php_admin_value in the FPM pool or Apache configuration, and check that no pool, directory or application setting puts a finite limit back. This removes the controllable PHP memory limit failure, but an underlying allocation failure can still reach the vulnerable path.
Set a low post_max_size. For applications that don't require file uploads, set post_max_size = 8M. If file uploads are necessary, set post_max_size = 32M. Keep upload_max_filesize below post_max_size. Consider enforcing limits at the web server or proxy level for decoded request size, input field count, multipart part count, header count, and nesting depth. These limits must also cover requests without a usable Content-Length.
Use a container or cgroup limit as an availability boundary, preferably with a policy that kills only the affected worker. Do not substitute RLIMIT_AS or RLIMIT_DATA, as these can cause the vulnerable allocation failure.
RCE via stale global state (CVE-2026-109619):
Set session.upload_progress.enabled=0 and restart every worker. Use php.ini, an FPM pool or server configuration that applies before request parsing. Do not rely on ini_set() or FPM .user.ini. This blocks the confirmed session paths but not other variants.
On PHP 8.5, set fatal_error_backtraces=0 and restart every worker. This blocks the confirmed fatal backtrace path only.
Remove invalid or deprecated settings applied per request that emit diagnostics before initialization. Hiding diagnostics with error_reporting, display_errors or @ does not help.
Fix attacker-reachable fatal errors and execution timeouts, including failures in callbacks, upload or import processing and cleanup.
The advisories linked above have the full technical details.

Chainfire retweeted

The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
Chainfire retweeted

Europe’s founders need a European standard to compete globally from day one.
Europe’s leaders committed to delivering one. But their teams are negotiating away the very things that make it one.
There is still time to change course if Europe's Heads of State step in now.


Chainfire retweeted

I think I found a planet nobody knew existed.
It's been hiding in NASA telescope data for seven years.
At the end of this thread, you can fly to it yourself.
Chainfire retweeted

Meet Mistral Large 4, aka Le Chonk.
• 1T parameters, natively multimodal. 49B active.
It is the best open weights model from US or Europe on aggregated benchmarks.
• State-of-the-art on critical workloads, including cyber defense, manufacturing and finance and it surpasses closed frontier models on visual grounding.
• Forged in Europe end-to-end and is deployable from Europe via our own Mistral Cloud infrastructure.
• Available to all via API today. Working with cybersecurity partners privately.
Open weights release end of October.
🤖 Made with AI
Chainfire retweeted

New cat alert! A call from a wildlife sanctuary about a "weird cat" has led to the first new cat species discovered in over 100 years in Bolivia’s Yungas forest ecoregion. Learn more about this feline surprise: on.natgeo.com/JRuaGj
Chainfire retweeted

Hey Claude, "Pick a problem or mystery that obsesses you and solve it as best you can & make a movie we can share on social media about it"
So it took a crack at the Voynich Manuscript & failed. Then it made this movie, which is pretty interesting to watch and a good explainer.
Chainfire retweeted

We’re disclosing HEIF Heist, a months-long investigation into libheif that allowed us to hack OpenAI, Slack, Meta, GitHub Ent, Rails, Next.js, ImageMagick, and many more.
It was literally xkcd #234, one obscure image library beneath a huge number of apps. 🧵

Chainfire retweeted
Today marks a major step for Mistral: we’re announcing a €3B Series D, the largest equity round ever raised by a European tech company, just three years after launch.
Chainfire retweeted

Signal's Contact Discovery automatically sends your contact list information to an SGX enclave in the cloud.
V12 broke into that enclave and leaked the key, allowing the server host to decrypt everything.
Two separate critical bugs: arbitrary read and RCE.
Here's how. 🧵

Chainfire retweeted

recommended reading.
blog.senko.net/code-was-neve…
