

threat researcher ~ medium: @darkjstr ~
Joined December 2018
- Tweets229
- Following66
- Followers976
- Likes4.8K




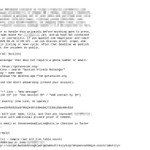


Climax ransomware: ransom note analysis
Signature: "Climax Inc." (hidden as binary at the bottom of the note)
Model: data theft + encryption
Payment: BTC only
Leak: dedicated blog on Tor Client area access requires a victim specific KEY
Tox: 91413065BA546646E2FA334556978F4F76E8D4CD228656B4B9A695ADAB7F283692C3012E9FE9
Session: 058a79746efcc0a300de7a669e431f2f73ce35de4571aab70a7071bffcbd1c3361

4
816
DarkJester retweeted

New Ransomware Groups both with 14 new victims posted each.
Climax Ransomware
/climaxf4srk4qzr5g7smfodx6q5ocpiwmls5qujfl7g3j33us4cksdad[.]onion
Vortex Ransomware
/zyz6phauvraxghujxmecpwzlg34gtogybb4wzcmw6pvps5m2nzvsriid[.]onion

DarkJester retweeted

Who Runs Qilin? Identifying Haise
A new investigation identifies Haise, a Qilin administrator, as Alexey Yakovtsev.
The findings were developed entirely on the @InteIHawk platform using its internal sources.
Full investigation: justpaste.it/iosba

New raas in town
DESTELLO RaaS (destell6tk2la7w4d7d4apfzsywbt2lsdpui7i2rsfyrike7pxolrbyd[.]onion)
Session:05b9e8aa7fe6af91c7a4fdf792500328c43c71d05d757e43d02f6c51daf1396b1d
Forum author: Destello4n4r (pwnforums[.]st)


new groups in town.
OBSOFT (6hzpdc5pxt57jmjxyegwjyhcinr2z3ajucizndehykz7zfrtaptln5qd)
PixelLeaks (pixelra2qbx7zhvb6mxdzxlo6rxm2mtouhbabqmdzyd4fesicvbz7bqd)
more analysis soon


DarkJester retweeted

New Everstake #Ransomware Leak Site
4 Victims
/everstakewfma6sxdpshoq4ebtnqamsxnajrtzu2cflai77kfup5kzyd[.]onion

Spacebears ransomware DLS caught mid debug crash on its onion portal. PHP 8.3.6, Laravel 10.43.0, Ignition exposed via SQLSTATE. Stack trace, filesystem paths, controller source, raw SQL queries and env vars visible. Code shows scripted view count inflation.


New group in town: WhiteArmor (W.A)
DLS: hxxp://whitearz6uvtfdefgsc4r3mzmyswtte65k5umcmv6cu6zhi4l5k4irad[.]onion/
Session: 05e7d90e446b823946dc3dfd8210ce14835cad13b28edadc798b51c186a29f5f7b
More analysis soon

New clearnet mirror of The Seven Deadly Sins DLS
193[.]24[.]123[.]177 AS200593 (Prospero OOO)
Same build as 37[.]72[.]140[.]179 (AS211663)

DarkJester retweeted

#THEGENTLEMEN #ransomware sticks to GLOBAL CONNECTIVITY SOLUTIONS🇬🇧
194.87.31.69🇳🇱
178.130.46.120🇷🇺
193.228.128.2🇷🇺
192.42.116.104🇳🇱
89.185.80.134🇺🇸
92.39.211.142🇷🇺
193.143.1.142🇷🇺
It's abused by #Akira, #Sinobi, #Tycoon2FA!
#security #infosec #malware #OSINT #darkweb #TOR

RT @ransomnews: 📣 Truffe WhatsApp, la guida utile 🇮🇹
Leggiamo sempre più spesso di persone in difficoltà dopo messaggi truffa su #WhatsApp…
🚨 Update: the archive node of The Seven Deadly Sins, 37[.]77[.]150[.]177 /pay_or_leak/, is back online
The open directory holds 4 more folders than the 7 victims shown on the Tor DLS board
Attached: README


🚨 The Seven Deadly Sins DLS exposed its clearnet infra
2 hosts serve the same DLS index on port 80, different builds (23 Sep and 24 Sep)
37[.]72[.]140[.]179 AS211663
185[.]100[.]85[.]146 AS200651
sha256 aca2081b75647ee71f7257de8ed456e6fa23603c76087ff86c8930696e408439
Distinct SSH host keys
Archive node
37[.]77[.]150[.]177:8080 /pay_or_leak/ AS198953
Now down
Same Session ID posted on exploit[.]in on 20 Aug 2026 by whale_leads42
Session: 051b27343be2bafb389aee16bfb6526d1f09d2e487430eb0427336415bb408452d


🚨 The Seven Deadly Sins DLS exposed its clearnet infra
2 hosts serve the same DLS index on port 80, different builds (23 Sep and 24 Sep)
37[.]72[.]140[.]179 AS211663
185[.]100[.]85[.]146 AS200651
sha256 aca2081b75647ee71f7257de8ed456e6fa23603c76087ff86c8930696e408439
Distinct SSH host keys
Archive node
37[.]77[.]150[.]177:8080 /pay_or_leak/ AS198953
Now down
Same Session ID posted on exploit[.]in on 20 Aug 2026 by whale_leads42
Session: 051b27343be2bafb389aee16bfb6526d1f09d2e487430eb0427336415bb408452d
While analyzing the HYFLOCK ransomware group, found that it has been active on underground forums since at least March 2026, well before its leak site was first observed.
Forum activity
Mar 2, 2026: account "hyflock" on Rehub forum claims its own Rust ransomware, self described student Same day asks about a libp2p P2P botnet
Mar 29 and Apr 12: RaaS ads on t1eron3[.]vip
May 29: RaaS ads in RU, EN and CHN on Duty Free forum
Apr 2: technical article on encryption design for RaaS on Rehub forum
Offer
Rust locker, 80/20 split, CIS banned VSS deletion, Defender disabling, GPO and SYSVOL deployment Suspension of 27 cloud services, DDoS and call spam Planned: AI assisted C2
Infrastructure
Affiliate panel, trial version linked in the May 29 ad, footer reads "2025 HYFLOCK": hxxp://e5hdifgit6ua7k4ggmltume7kbyryksdnlrkc55we33fnshgxfeqgsyd[.]onion Leak site: hxxp://yhgphvfgaecacgtlbn67u7yfhafe6evnj4gs4s2oyb3hzjnlhq45azqd[.]onion/blog Assessment: new brand, actor active since at least March


Noticed that Global Cybernetic Collective has relaunched a RaaS program
Actor $€0 posted on T1erone: return to ransomware, affiliates welcome for full collaboration now, manual mode for the moment, automation to come
Onion URLs listed:
1. hxxp://globalrbweyhxxa5b65bjjsm5bfuqfs5ydizefupqcminoedzn6o2sqd[.]onion
2. hxxp://globalco44t2yl6ltgj74cwthr6b6olggl3srg7engqfhx72f6ni3cyd[.]onion
3. hxxp://globaldonejcrwbe7ujwuzptsummx3rvba54wcjoxrjvqgo37y4aqwid[.]onion
More analysis soon

4
939
