









👍

Binance’s SAFU fund and Binance’s holdings include a large amount of assets such as BTC and ETH. We are currently buying, through OTC and on-exchange, all the stolen altcoins in fully matching amounts. We will update everyone again once the purchases are complete.
币安的SAFU基金和币安持有币种包括大量的BTC和ETH等资产,目前正在通过OTC和场内买入完全匹配被盗的所有山寨币来完成POR,购入完成后再次为大家同步信息。
그릿 retweeted
Investigation update: Our initial investigation suggested that the security incident may have involved a compromised laptop, however our subsequent investigation has uncovered additional points of breach.
This was a complex attack, and we are doing all we can in coordination with law enforcement to resolve it. We are still gathering the facts, and will share more directly as we have them.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe.
We are still on track towards the expected timeline to resume the withdrawal service in 45 hours. Deposits remain unaffected.
The outflows ceased when we paused withdrawal service earlier. We are still working with partners to freeze many of the impacted assets, and have frozen around $3 billion thus far.
We will continue to provide further updates through official Binance channels as more verified information becomes available.

속보: 해커들이 7개국의 은행을 동시에 공격하고 있다는 소식이 전해지고 있다.
이 소식을 접하면서 한 가지 생각이 든다.
사이버 전쟁은 더 이상 먼 미래의 이야기가 아니라, 이미 우리가 마주하고 있는 현실이 아닐까?
최근 여러 국가에서 비상식량과 생필품 비축을 권고하는 움직임을 보며 또 다른 의문이 생긴다.
과연 이러한 권고는 단순히 전쟁이나 자연재해에 대비하기 위한 것일까?
아니면 대규모 사이버 테러로 인한 금융 시스템 마비, 통신망 장애, 인터넷 접속 제한 등 우리가 한 번도 경험하지 못한 수준의 사회적 셧다운까지 염두에 둔 대비책은 아닐까?
AI 기술의 발전은 인류에게 새로운 가능성을 열어주고 있지만, 동시에 국가와 금융 시스템 전체를 위협할 수 있는 사이버 공격의 위험성도 키우고 있다.
어쩌면 앞으로 우리가 가장 경계해야 할 위기는 금융시장의 폭락이 아니라, 금융과 통신이라는 사회의 기반 시스템이 동시에 멈춰버리는 순간일지도 모른다.
모든 것이 멈추는 날이 혼란을 틈타 또 다른 전쟁의 시작점이 될지도 모른다는 생각마저 든다.
한국은 안전으로부터 어떻다고 생각하는가?

🚨 BREAKING: Hackers are hitting banks in 7 countries at the same time.
This is what Covid looked like in week 1. A few countries. Small numbers. Nobody called it a crisis.
1/ South Korea: hackers used a Chinese AI tool to break into at least 7 financial firms. 68,000 people's data stolen. 16 firms breached by mid-October. This week Daishin Securities reported 38,490 customers' data leaked, bank account numbers included.
2/ Latin America: one gang ran AI agents built on Claude, Grok and Kimi against 400+ targets, banks and payment firms included. They stole passwords and got into customer bank accounts.
3/ Italy: a fake WhatsApp from "the CEO" and an AI-cloned voice got Intesa Sanpaolo's private bank to send out €95 million. €36 million is still MISSING, turned into crypto.
4/ India: small lenders lost ₹300 crore (about $31 million) in 2 months. 150 cases. Hackers copied bank logins and sent the money out as fake loans. One firm was hit twice.
5/ Crypto: $351 million drained from Bitget's hot wallets. North Korean hackers are suspected.
6/ Japan: hackers hit GMO Internet's currency trading service and demanded $50 million in crypto. The prime minister promised an emergency anti-cyberattack package.
7/ Australia: the regulator warns AI attacks put more than A$4.5 trillion in retirement savings in the firing line. Government cyber alerts jumped 80% in a year.
Now zoom out.
AI hacking tools are now easy to get. Smaller firms have weak security. The money moves in minutes. It jumps across banks, through rented accounts, out as cash or crypto. The bosses are often abroad.
Covid locked the streets. Nobody is calling this a crisis yet. But the central banks already plan for the day the hackers get in.
The G7 agreed to run drills that simulate AI attacks on banks. The ECB reportedly gave eurozone banks 4 months to hand in their defence plans.
If your savings sit in a bank, hit follow. I'm tracking where the hackers strike next and how much they take.
Readers added context they thought people might want to know
The listed incidents occurred at different times over months (e.g. Italy in Feb 2026; Bitget Sep 24; Latin America targets May-Sep), not simultaneously as presented.
tomshw.it/altro/95-milio…
decrypt.co/379350/bitget-…
aichatdaily.com/ai-security/ha…
m.economictimes.com/et-front/promp…
smh.com.au/politics/feder…
theverge.com/ai-artificial-…
en.yna.co.kr/view/AEN202610…
이번 바이낸스 해킹 사태를 지켜보며 다시 한번 느낀다.
이 시장에 절대적인 안전이란 존재하지 않는다는 사실을.
더욱 두려운 것은 이번 사건 자체보다 그 이후다.
다음 공격 대상이 코인베이스 프라임(Coinbase Prime)이 될 수도 있고, 블랙록 IBIT의 기관 수탁 자산이 될 수도 있다는 불안감.
이러한 가능성이 투자자들의 인식 속에 서서히 스며들기 시작한다면, 그것이야말로 시장을 지배하는 가장 무서운 공포가 될 것이다.
AI 기술이 빠르게 발전하고 사이버 공격의 위협이 갈수록 고도화되는 시대.
최근 들어 한 가지 생각이 머릿속을 떠나지 않는다.
우리가 알지 못하는 거대한 기득권 세력의 치밀한 각본이든, 예측하지 못한 대규모 해킹이든, 그 배경이 무엇이든 간에 결국 우리가 마주해야 할 현실은 같다.
크립토 시장뿐 아니라 기존 금융 시스템마저 언제든 신뢰의 붕괴와 구조적인 리셋을 경험할 수 있다는 것.
어쩌면 앞으로 우리가 경계해야 할 가장 큰 위험은 가격의 폭락이 아니라, 금융 시스템 자체에 대한 신뢰가 무너지는 순간일지도 모른다.
만약 코인베이스 프라임(Coinbase Prime)의 보안 사고로 IBIT의 보관 자산까지 피해를 입고, 여기에 스트래티지(Strategy)마저 무너지는 상황이 벌어진다면 어떻게 될까?
그때는 단순히 크립토의 겨울이 찾아오는 수준을 넘어, 시장 전체의 신뢰와 구조가 붕괴하는 완전한 리셋으로 이어질 수도 있다는 생각이 든다.
개인 지갑부터 중앙화 거래소, 기관 수탁 시스템까지 신뢰가 무너지기 시작한다면 과연 무엇이 남을까?
어쩌면 진정한 공포는 아직 시작조차 하지 않았을지도 모른다.

I suspect IBIT is already on North Korea’s shortlist.
In February 2025, the attackers behind the Bybit hack compromised a Safe{Wallet} developer’s Mac through a malicious project disguised as legitimate Docker-related tooling. They had access for 17 days before the theft, giving them enough time to manipulate the transaction interface used by Bybit’s signers. The signers believed they were approving a legitimate transaction. Instead, they unknowingly authorized the theft of $1.5 billion from a cold wallet.
The keys could stay offline while the signers approved a theft through a compromised interface.
TRM Labs attributes the recent Binance incident with high confidence to TraderTraitor, the North Korean group also linked to Bybit and the theft of 4,502.9 BTC from DMM Bitcoin. Binance’s preliminary investigation points to a compromised DevOps engineer’s laptop as the entry point. Binance says there’s no evidence that private keys were leaked, while TRM’s analysis suggests the attackers may have gained control of the signing infrastructure. If confirmed, the attackers could have moved funds through a compromised approval process without extracting the keys.
Now imagine the same thing happening to IBIT.
BlackRock’s IBIT is the world’s largest Bitcoin ETF, holding roughly 815,000 BTC worth around $63 billion. Coinbase remains its active Bitcoin custodian. Although Anchorage Digital has been appointed as an additional custodian, the fund’s latest quarterly filing says there are currently no plans to transfer any Bitcoin there.
That’s an extraordinary concentration of Bitcoin under one custodian. Regardless of how large or well-funded that provider is, a critical failure in its security infrastructure could put the entire fund at risk.
A $6 billion theft would wipe out roughly 9.5% of IBIT’s assets, equivalent to around $4 per share at current valuations.
Binance managed to freeze some stolen stablecoins. Bitcoin has no such mechanism, making stolen BTC far harder to recover.
BlackRock doesn’t separately insure the Bitcoin held by the fund. Coinbase has disclosed $320 million in commercial crime insurance coverage, shared across its customers. Its custody agreement also limits liability to $100 million per cold storage address, with any recovery subject to contractual terms, liability determinations, and other conditions.
If a major theft occurred and the fund couldn’t recover the Bitcoin or obtain sufficient compensation, the remaining losses would ultimately be borne by IBIT shareholders.
Bitcoin ETFs have made owning Bitcoin much more accessible, and there’s real value in that convenience. But as more capital flows into these products, enormous amounts of Bitcoin are also being concentrated among a handful of custodians and the infrastructure they depend on.
The larger these pools become, the more attractive they are to attackers. A compromise at any critical point could have consequences far beyond a single institution.
And that’s why security has no finish line.
Even the most sophisticated cold storage setup still depends on hardware, software, supply chains, signing workflows, and the people operating them. Keeping private keys offline is essential, but it doesn’t eliminate the risks surrounding the transaction approval process.
Spread your assets across independent custody setups. Keep your private keys offline. Verify transaction details on a trusted device screen, independently of the computer initiating the transaction. Continuously review your security architecture, and build it around the assumption that some part of your infrastructure will eventually be compromised.
There are no silver bullets in security, and no permanent guarantees. Stay vigilant, keep verifying, and never mistake a clean track record for proof that you’re safe.
Bunker mode.
Aave 에서 이자 더 먹겠다고 WETH 예치한 애들 머리아프겠네

Aave Freezes V3 and V4 Markets After Binance Exploiter Deposits $60M USDT and Borrows 19,762 WETH
Aave risk service provider LlamaRisk said one wallet linked to the Binance exploiter deposited about 60 million USDT into Aave V3 Ethereum Core and borrowed 19,762 WETH (worth roughly $44.6 million) between 20:58 and 21:01 UTC on October 29, about 40 minutes before the first freeze. The position remains over-collateralized and is the exploiter’s only position on Aave.
Aave froze all DAO-operated V3 and V4 markets as a precaution after a potential security incident involving Binance-affiliated wallets, pausing new deposits and borrowing. Users can still withdraw assets and repay existing loans. In total, 175 V3 reserves across 16 networks and 117 V4 reserves across four networks were frozen. Aave said its contracts were unaffected and it aims to lift the freeze as soon as possible.

콜드카드부터 렛저까지, 잇따른 하드웨어 월렛 보안 논란은 투자자들에게 셀프 커스터디에 대한 불신을 심어주었다.
그 과정에서 오히려 중앙화 거래소가 더 안전할 수 있다는 인식이 확산될 여지도 있었다.
그런데 시장 사이클상 10월 29일이 저점일 것이라는 전망이 나오는 시점에, 공교롭게도 10월 30일 세계 최대 암호화폐 거래소 바이낸스에서 대규모 해킹 사건이 발생했다.
개인 지갑에 대한 신뢰가 흔들리고, 이제는 거래소에 대한 신뢰마저 무너지는 상황.
마치 크립토 시장 전체를 리셋하려는 듯한 일련의 사건들.
단순한 우연의 연속일까?
아니면 모든 것이 치밀하게 짜인 각본처럼 흘러가고 있는 걸까?
ZachXBT: Stolen Funds from the $6.3B Binance Exploit and $388M Bitget Exploit Commingled at Same Address, Suspected Same North Korea-Linked Attacker
ZachXBT posted that stolen funds from the $6.3 billion Binance exploit and the $388 million Bitget exploit arrived via THORChain and were commingled at the same address. ZachXBT stated that this indicates the same actor is likely behind both incidents. The Bitget exploit had previously been attributed to the North Korea-linked TraiderTraitor, which has overlap with other previous exploits such as Kelp DAO.
According to MistTrack, stolen TRX from the Binance incident flowed through Bitget Wallet Swap Bridge into an address beginning with 0xCd68. On-chain tracking shows that this address was previously used by the Phemex hacker.


바이낸스
해킹 여전히 진행중이라는데
출금은 다 막힌 상태고
바이낸스 가격 괴리는 아직 안생김
디파이쪽 대출쪽만 가격괴리 생김
이거 생각보다 좃된 상황 같다

So, here’s what happened: Binance hot wallets were drained of $5.60B today across Ethereum, Bitcoin and Tron.
$200m were transferred few minutes ago, so hack is still ongoing
Here is what is on-chain rn: what is frozen vs not, and the addresses to watch.
➮ Totals
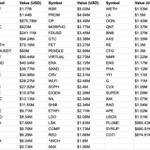
✧ $5.60B pulled from Binance hot wallets
✧ 3 chains: Ethereum, Bitcoin, Tron
✧ 67 assets, 63 of them swept out of Binance 14 in a single tx
✧ Attack vector not confirmed at time of writing
➮ Frozen so far: $2.38B
✧ $1.56B USDT frozen by @Tether_to: $1.18B on Ethereum + $379M on Tron
✧ $823M USDC frozen by @circle
✧ Thats ~42% of the haul neutralized within the day
➮ Not frozen: ~$2.6B
✧ 18,270 $BTC ($1.45B) - nobody can freeze this
✧ 197K $ETH ($451M) - same
✧ ~$730M USDT still unfrozen, Tether can still act on it
✧ Rest: $TRX ($234M), $RLUSD ($88.5M), $WBETH ($75M), $XAUT ($50M) and a tail of smaller tokens
➮ Addresses to watch (paste into etherscan / mempool / tronscan)
Ethereum, attacker main, holds the frozen USDT + USDC:
0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c
Ethereum, 195,460 ETH parked here:
0x8532fa14acaf483729c449b8458aeddb900543d4
Main sweep tx, 63 tokens out of Binance 14:
0x53bd38b816c23e74134786c29a8c18d792777998a3b9326047b583100e88e2f3
Bitcoin, 18,270 BTC received:
bc1q0mtc2f5agpkvlq6hhahmfr3hlr55kyfjhl2mnm
Tron, 612.7M USDT received, 313M of it frozen:
TG5iBMQPrDzJJAUM8GMVBf1hRaJ1wvzsGi
Tron, 216M USDT, not frozen:
TSUUVjysXV8YqHytSNjfkNXnnB49QDvZpx
➮ Context
✧ Previous record: Bybit, Feb 2025, $1.5B in ETH. This is ~3.8x that
✧ Binance 2019 hack: ~7,000 BTC, ~$40M, covered by SAFU
✧ Binance 2022 BNB bridge: ~$570M, most of it frozen by validators within hours
✧ Moreover, SAFU fund was ~$1B at last disclosure. This hack is 5x+ that, so the coverage question is Binance balance sheet, not SAFU
➮ What matters next
1/ Whether Tether freezes the remaining ~$730M USDT, and whether Ripple does the same with $88.5M RLUSD
2/ First outbound hops from the BTC and ETH addresses, bridges or mixers. Until then $1.9B is just sitting there
3/ Binance withdrawal status and an official statement on how 63 tokens got signed out of Binance 14
4/ Whether this follows Bybit pattern: that money went through THORChain within days, same route would show up fast here
Will update as the addresses move.

날도 추워지는데
크립토도 겨울 확정이네
그놈의 해킹 유출
지겹다
바이낸스 출금도 막혔다

🚨SUSPECTED BINANCE HACKER WALLET HOLDS OVER $5.7B ON-CHAIN!
Arkham tracking for the entity labeled “binance-hacker-1029” shows roughly $5.72 billion in related holdings, including about 1.567B USDT, 18.27K BTC, 385.8K ETH, and 823M USDC.
Tether and Circle have frozen the bulk of the stablecoin portion.
그릿 retweeted

UPDATE:
Well, another $780M USDC has now been confirmed moving from a THIRD Binance hot wallet to the exact same address.
We’re now talking about $5.62 BILLION.
Here’s what I’ve found.
The three Binance hot wallets:
20:24:23 UTC: $2.527B transferred from Binance 14
20:24:47 UTC: another $174.4M from a second Binance hot wallet
20:41:23 UTC: 780M USDC from a third Binance hot wallet
All three sent funds to:
0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c
Total received: $3,481,300,000.
The wallet is no longer just holding the funds.
According to the latest transaction analysis:
500M USDT moved to 0x9749292d…c762
Another 200M USDT moved to 0x0ddf0480…697e
195,460 ETH, worth approximately $446M, moved to 0x8532fa14…43d4
Part of the USDT was subsequently converted into approximately 122,312 ETH
Another wallet received 190M USDT and 3,552 ETH, with at least 10M USDT later deposited into Aave
BROTHER.
We’re talking about hundreds of millions being split between wallets, converted into ETH and moved into DeFi.
Thank god Tether was fast enough and we have $1.8B frozen.
Tether or Circle actually froze those funds.
We need an official explanation.


Binance just got $2.7 BILLION out in 24 seconds
If confirmed this could be the biggest hack of 2026
I’ve been looking at the transactions and, for now, the onchain activity looks much more like an internal wallet migration.
Here’s what happened:
At 20:24:23 UTC, Binance’s hot wallet known as Binance 14 transferred $2.53B across 64 different tokens.
24 seconds later, another Binance hot wallet sent an additional $174.4M to the exact same address.
Total: $2,701,600,000.
The assets moved included:
- $1.67B USDT
- $454.1M ETH (195,470 ETH)
- $88.5M RLUSD
- $77.1M wBETH
- $50.5M XAUt
- $50.4M UNI
- $43.9M ENA
- $38.1M PEPE
- $29.7M LINK
- $27.7M USD1
The Original Binance hot wallet:
0x28c6c06298d514db089934071355e5743bf21d60
Receiving wallet:
0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c
The receiving wallet was created today and had no previous transaction history.
Despite receiving billions, it hadn’t started sending the funds to mixers, exchanges or other addresses at the time of the analysis.
Another Binance-labeled hot wallet independently transferred funds to the same destination just 24 seconds after the first batch.
And the original Binance wallet was still operating 16 minutes later, with approximately $98.6M remaining.
There’s one strange detail though.
At 20:41 UTC, the same relayer attempted another transfer involving 780M USDC from a third Binance hot wallet.
That transfer didn’t complete.
So there’s still something worth investigating.
Meanwhile, the market is getting destroyed.
$BNB: 8.6%
$ETH: 4.0%
$BTC: 2.7%
All down
For now, the most important wallet to watch is:
0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c
If those funds start moving toward mixers or unrelated destinations, the situation changes completely.


