

Pinned Tweet
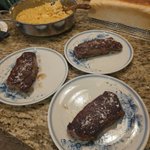
here is how the prime rib came out for the party yesterday. it was a perfect medium rare. we went through the entire thing.
instead of slicing it all up at once, i stood at the end of the buffet line and sliced as each person came up. this stopped it from getting cold.



this brotli thing is way worse than anything else that has happen this month and the biggest reason is that no one understands their exposure


i created a grok bot named gtwy and told the other bots to stop asking me for permission, ask gtwy instead
𝕘 𝕥 𝕨 𝕪 retweeted

There’s a world of difference between user-authorized agents (Muse, Instinct, Grokbot, etc.) and true unauthorized/rogue agents that could constitute cyberattacks.
Most of the activity described in the Axios story appears to be the former: customers sharing credentials with agents so they can take actions on their behalf. This may violate bank terms requiring humans to log in themselves, but these are in no way cyberattacks.
The direction banks should go is to support user-directed agents. For example, Amex is an authorized connection in Muse, making it easy for users to grant, limit, and revoke access.
Read-only permission levels are a sensible interim step. Several banks already support or are moving toward them. Full write access (with user credentials) is a different risk category and should be approached carefully.
Frightening the public by blurring the line between user-authorized agentic behavior and cyberattacks is irresponsible.

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…


𝕘 𝕥 𝕨 𝕪 retweeted

Make sure you logout of all web sessions before bed and change your passwords you’ll thank me later also turn on 2FA
PHP has a major exploit and they’re gonna be stealing passwords like crazy.
You may want to change passwords for anything you use in cross sessions such as Google and Others