

From the merger of HWG srl and Sababa Security, HWG Sababa offers a complete suite of customized cybersecurity solutions.
Piazza Tre Torri 2, Milan
Joined November 2019
- Tweets506
- Following125
- Followers136
- Likes783



⚠️ The #LazarusGroup recently targeted a #Bitdefender researcher using a fake job ad on LinkedIn. #hackers impersonate recruiters to spread #malware via compromised GitLab repositories.
🔒 Stay protected – learn more: hwgsababa.com/en/defense-cen…

New #ransomware group #Kairos is making waves with double-extortion tactics, targeting sectors like healthcare, engineering, and finance.
With our #DefenceCenter, we help you stay ahead of threats like these. 👇Learn more: hwgsababa.com/en/defense-cen…

🎙️ Raffaele Fazio, Head of #DefenceCenter, su @RaiNews commenta l’attacco hacker filorusso #Noname057 ai ministeri e forze armate. Lavoriamo con #ACN per contrastare le minacce.
👉 Intervento: youtu.be/8t3L7Bnvdsg?si=FKtz…
➡️ Il nostro Defence Center: hwgsababa.com/defense-center…

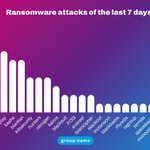
Top groups making headlines:
#Lynx
#Lockbit3
#Ransomhub
#Incransom
Stay ahead of the threats. Learn how our #SOC can protect your organization: bit.ly/3HPuPmz
#CyberSecurity #Ransomware

💻 #Ransomware Attacks – 1st Week of Jan 2025 📊
🔴 #Bashe hit manufacturing infrastructure.
🔵 Double extortion tactics surged across industries.
🔐 We Make You Cyber Safe, discover how:
➡️ hwgsababa.com/en/defense-cen…

⚠️#Mozilla has released security updates to address #vulnerabilities in #Firefox, #FirefoxESR, and #Thunderbird, including 3 rated as high severity.
Vulnerability types:
🔴 Arbitrary Code Execution
🔴 Spoofing
We Make You Cyber Safe👇
hwgsababa.com/en/
#CyberSecurity

🚨 #Cyberattack on #InfoCert, major #SPID provider: 5M+ records stolen, now on the #darkweb. Confirmed via third-party #breach.
Learn about boosting cyber resilience in the supply chain 👉hwgsababa.com/en/cybersecuri…

🚨 #DDoS Attacks in Italy: #NoName057(16) Strikes Again
Pro-Russian group intensifies DDoS attacks on infrastructure.
💡 Protection with CDN, WAF, and traffic filtering is key!
👉 Discover how we protect critical infrastructure: hwgsababa.com/en/resources/c…
#CyberSecurity #Hacking

🇩🇪 The German Federal Information Security Agency (BSI) has blocked the #BADBOX operation, a sophisticated #malware attack affecting 30,000+ devices. By isolating malicious IPs, they disrupted the attack.
#Cybersecurity #ransomware

🎄 #𝗠𝗲𝗿𝗿𝘆𝗖𝗵𝗿𝗶𝘀𝘁𝗺𝗮𝘀 𝗳𝗿𝗼𝗺 𝗼𝘂𝗿 𝘁𝗲𝗮𝗺!
This year, many of us gathered from our 🇮🇹 offices. Though some, especially abroad, couldn’t join, our team spirit keeps us united! 💪
Here’s to growing together and facing new challenges in 2025! 🚀
#CybersecurityTeam

🚨 #Mirai Alert: Default #passwords = disaster!
#Juniper warns of Mirai #malware infecting SSR devices for #DDoS.
🔑 Fix it:
Change default passwords
Check logs
Use firewalls & update systems
We Make You Cyber Safe, discover how: bit.ly/3HPuPmz
The Romanian Cybersecurity Directorate (DNSC) confirms that the #Lynx group is behind the #ransomwareattack on #ElectricaGroup, one of Romania's largest #electricity providers. Investigations are ongoing. #CyberSecurity #Ransomware

Attenzione!
#Phishing: come funziona e come proteggersi?
➡️Scopri di più: hwgsababa.com/attacchi-phish…


‼ #Phishing: rilevata campagna a tema #sondaggio che sfrutta loghi e riferimenti relativi alla compagnia assicurativa #Generali al fine di carpire gli estremi delle carte di credito
🔗 csirt.gov.it/contenuti/phish…
⚠ verificare scrupolosamente i mittenti delle e-mail ricevute

Active since early 2024, #RansomHub targets industries like IT, healthcare, and finance using advanced techniques:
🔹 Exploiting Zerologon (CVE-2020-1472)
🔹 Disabling #EDR tools (EDRKillShifter)
🔹 Obfuscated scripts to evade detection
Stay Alert: bit.ly/3HPuPmz

🚨 #MISP Alert: #Vulnerabilities #CVE-2024-54674 & CVE-2024-54675 discovered.
🟡 Risk: MEDIUM (64.35/100).
❗ Affected: MISP ≤ 2.5.2.
✅ Update to the latest version now!
#CyberSec #CyberAlert
#MISP: sanate 2 vulnerabilità nella nota piattaforma open source per lo scambio delle informazioni e correlazione dati
Rischio: 🟡
Tipologia:
🔸 Security Restrictions Bypass
🔗 csirt.gov.it/contenuti/risol…
🔄 Aggiornamenti disponibili 🔄

🚨 Russian authorities have arrested Mikhail #Matveev, a notorious #cybercriminal linked to the Hive and #LockBit #ransomware gangs.
Matveev, wanted by the U.S. for global #cyberattacks, is accused of of creating ransomware for #dataencryption & extortion.
#CyberSecurity

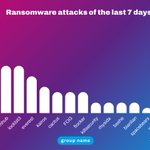
🚨 #Ransomware trends this week: #Bashe and #Eldorado remain among the top trends, while #Incransom is growing.
Discover our SOC: bit.ly/3HPuPmz

🚨 2,000+ #PaloAltoNetworks firewalls hacked! 🚨
Hackers exploited recent PAN-OS zero-days (CVE-2024-0012 & CVE-2024-9474) to gain remote admin access and escalate privileges. Palo Alto urges securing firewall access. 🔒
Source: @redhotcyber
#CyberSecurity #ZeroDay #PANOS

🚨 7-Zip Vulnerability (CVE-2024-11477) 🚨
A remote code execution flaw in 7-Zip (versions < 24.07) was fixed in June 2024. Attackers could exploit it to run arbitrary code.
🔴 Risk: MEDIUM (63.84/100)
💡 Action: Update to 24.07+ ASAP.
#SecurityAlert #InfoSec #CyberSecurity
🚨 #Ransomware trends this week:
#Bashe – leading with rapid, targeted attacks.
#Eldorado – cripples critical infrastructures, demanding high ransoms.
#Blacksuit – known for stealth and evasion tactics.
Discover our SOC: bit.ly/3HPuPmz
