

hack into my DNA :) Who am I? DevSecOps Engineer,PenTester,Security researcher,BugHunter(Sometimes) 🇦🇪🇮🇷
Dubai, United Arab Emirates
Joined November 2012
- Tweets4.7K
- Following627
- Followers3.5K
- Likes11.7K





Pinned Tweet
دامنه ها زیرجهت انجام کارهای تحقیقاتی و یا فعالیت های بچه های کامیونیتی امنیت به اشتراک میذارم
attack.ir
blackhat.ir
blackhats.ir
whitehat.ir
whitehats.ir
pen-test.ir
ریت بزنیدهرکی نیاز داشت DNS هاش رو ست
Esmaeil Rahimian retweeted

حالا به واسطه محتوی تولید شده توسط هوش مصنوعی، حتی باید بین اعضای خانواده هم رمز داشته باشید!
مراقب باشید مجرمین هم به هوش مصنوعی دسترسی دارند!
Well… this week just got even better. 🐛🔥
Another $6,000 bounty from Google — in the same week! 💰🎉
And this one came with something I really appreciate:
Google awarded a 120% bonus in recognition of the “exceptional quality” of my vulnerability report and technical analysis. 🏆
That means a lot.
Bug bounty isn’t only about finding the vulnerability. Understanding the security boundary, demonstrating the real impact, and communicating it clearly are just as important.
From an RCE marked “Duplicate” 😂💀
to two $6,000 rewards in the same week. 🔥
A huge thank you to @GoogleVRP and the Google Security team for the recognition, and for the work they do with the security research community. 🙏
Research quality matters.
Report quality matters.
Persistence matters. 🚀
What a week! 😂🔥
#BugBounty #GoogleVRP #CyberSecurity #SecurityResearch #InfoSec #EthicalHacking
🤖 Made with AI


Another weekend. Another bug bounty adventure. 🐛🔥
But this time, a different ending! 😎💰
Last week:
Google: Duplicate. 💀😂
This week:
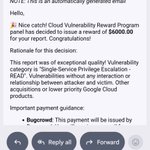
Google: Nice catch! $6,000 bounty awarded! 🎉🚀
And the cherry on top? 🍒
Google described my vulnerability report as being of "exceptional quality." 🏆
That's the beauty (and pain 😂) of bug bounty hunting.
One weekend you're staring at a duplicate notification. The next, you're celebrating a $6,000 reward from Google Cloud VRP.
Same researcher. Same passion. Different outcome.
Persistence pays off! 🔥
Remember last week's adventure? 👇
teapawt.org/H_Mosafer/status/21194…
See you next weekend! 😂🚀
#BugBounty #GoogleCloud #CyberSecurity #SecurityResearch #InfoSec #EthicalHacking #BugBountyHunter

Esmaeil Rahimian retweeted

Researchers(Mark Ermolov, Dmitry Sklyarov, and Maxim Goryachy (from Positive Technologies)) found two undocumented x86 instructions, udbgrd and udbgwr, that can read and write microarchitectural data directly.
They enable access to the microcode patch RAM and match-and-patch structures inside the CPU. UDBGWR is capable of modifying MSRAM and updating match-and-patch entries that override target instructions. Intel has never documented these instructions but they're callable from user space and they give direct write access to the CPU's microcode storage.
Another weekend. Another bug bounty adventure. 🐛🔥
But this time, a different ending! 😎💰
Last week:
Google: Duplicate. 💀😂
This week:
Google: Nice catch! $6,000 bounty awarded! 🎉🚀
And the cherry on top? 🍒
Google described my vulnerability report as being of "exceptional quality." 🏆
That's the beauty (and pain 😂) of bug bounty hunting.
One weekend you're staring at a duplicate notification. The next, you're celebrating a $6,000 reward from Google Cloud VRP.
Same researcher. Same passion. Different outcome.
Persistence pays off! 🔥
Remember last week's adventure? 👇
teapawt.org/H_Mosafer/status/21194…
See you next weekend! 😂🚀
#BugBounty #GoogleCloud #CyberSecurity #SecurityResearch #InfoSec #EthicalHacking #BugBountyHunter
Another weekend. Another bug bounty adventure. 🐛
Found an RCE on Google. 🔥
Google: Duplicate.
At this point, if an RCE can be a duplicate, please don’t talk to me about luck. 😂
Bug bounty is basically:
Find nothing → 😐
Find a bug → 😎
Find an RCE → 🤯🔥
Submit it → 🚀
“Duplicate” → 🤡💀 I expected a duplicate RCE on almost any target, except Google.
See you next weekend. 😂
#BugBounty #CyberSecurity #RCE #InfoSec #Hacking #SecurityResearch

Esmaeil Rahimian retweeted

Keep going!!!!
Bug bounty gives companies access to findings via subsidized tokens rather than them paying full api costs. And even when they run hacking agents internally, they don’t know for sure if it’s reachable externally. If you get a bug bounty report, you have proof an external actor can exploit the bug. And you didn’t have to pay api token costs to get it either.

Esmaeil Rahimian retweeted

Telegram Desktop: one-click account takeover via IPC injection
beaksec.github.io/posts/tele…


Esmaeil Rahimian retweeted

If France's attribution and statement about Iran's attacks against fridges sounds a bit odd or unexpected for you, you might find what we discussed during this podcast session helpful to clear things up:
youtube.com/watch?v=0TlmD07D…

Another weekend. Another bug bounty adventure. 🐛
Found an RCE on Google. 🔥
Google: Duplicate.
At this point, if an RCE can be a duplicate, please don’t talk to me about luck. 😂
Bug bounty is basically:
Find nothing → 😐
Find a bug → 😎
Find an RCE → 🤯🔥
Submit it → 🚀
“Duplicate” → 🤡💀 I expected a duplicate RCE on almost any target, except Google.
See you next weekend. 😂
#BugBounty #CyberSecurity #RCE #InfoSec #Hacking #SecurityResearch
🤖 Made with AI


Esmaeil Rahimian retweeted
مدتیه دارم شبکه های اسکم سرمایه گذاری مثل پرواربندی (Pig butchering) رو که اکثرا از شرق آسیا مدریت میشن رصد میکنم و به جرات میگم که یکی از اهداف اصلیشون مردم ایران هستند.
به دلیل پرداخت سود و عمله های سودجو داخلیشون به سرعت فراگیر میشن، مراقب باشید.


Esmaeil Rahimian retweeted

Started putting some of the markdown files that were the basis that guided most of the agents while hacking MacOS on github. more will come as im able to clean up some of the files to remove some nuanced things.. but heres the repo:
github.com/dawgyg/AppleResea…


In October, I submitted 99 vulnerabilities to 8 programs on @Hacker0x01. #TogetherWeHitHarder hackerone.com/last-month
3
61
2,472
Esmaeil Rahimian retweeted
ایمیلهای #فیشینگ یوتیوب که از تکنیک ایجاد ضرورت در کاربر و BitB استفاده میکنن کانال دارهای یوتیوب رو هدف قرار میدن، این ایمیل منتج به گزارش جدید اسکم مایندر شد، دوست داشتید بخونید و نظرتون رو بگید.


That Google login window could be drawn inside a phishing page.
The latest investigation from ScamMinder Research examines Browser-in-the-Browser deception on two YouTube-themed phishing sites and analyzes a broader dataset of 224 related hostnames.
scamminder.com/blog/youtube-…
#Phishing #AntiScam
