Invisible by design. Secure by default.
Joined October 2025
- Tweets278
- Following30
- Followers367
- Likes231






LayerV AI retweeted

Good luck today, @ReelLifeJustin and @LayerVAI!
From treasure hunts to the 9th Annual #DataTribeChallenge finals in D.C.—we’re rooting for you! 🏆
Pitches: 3–6 PM ET (noon–3 PM AZ).
Follow the event: cyberinnovationconference.co…

LayerV AI retweeted

The AI changes happening right now are making it much easier for bad actors to break into accounts, steal money, and lock people out of their own lives. Most people won't notice until it happens to them or someone they care about. I don't want that for any of you.
You don't need to understand the tech. Just do these basic things this week:
1. Update everything. Phones, computers, tablets, and apps. Turn on automatic updates so it stays current.
2. Stop reusing passwords. Use the free password manager that came with your phone (Apple or Google) or something simple like @Bitwarden or @1Password. Give every important account its own password.
3. Turn on extra login protection on email and banking. Prefer an authenticator app or passkeys over text-message codes if you can. Save any recovery codes somewhere safe first.
4. Never give out login codes or download anything from a call, text, or email you weren't expecting -- even if it looks official.
5. Back up your important photos and files somewhere separate from your main devices.
6. If you need to share files with people and you use a Mac, consider downloading qURL desktop: qurl.link (tap "send a file").
7. If you have an iPhone or Mac, look up "Lockdown Mode" and consider turning it on. It limits a few conveniences but closes a lot of doors.
If that list feels like a lot, just do #1 and #4 today. Those two alone stop a huge percentage of the problems.
This isn't theoretical anymore. The people who get ahead of it might be fine. The ones who wait usually aren't.
Do these for yourselves.

LayerV AI retweeted
We received 3 million attack attempts in 10 days. Nice try!

Crazy timing - just days after we announced qURL 2.0 🤯
Tailscale puts you on a private mesh, so one compromised device + privileged ssh = root across the network.
qURL issues only temporary, resource-scoped access. The target stays invisible until a valid grant is presented.

‼️ Tailscale SSH Flaws Could Let Hackers Gain Root Access Across Servers
Details: cybersecuritynews.com/tailsc…
A new security report warns that Tailscale SSH has flaws that could let a hacker move from one compromised device to root access on other servers. Tailscale SSH lets approved devices log in to each other over a private network. The report lists 11 findings in five groups.
They cover Tailscale’s SSH server, its serve and app connector features, the DERP relay client, and headscale, an open-source server that manages Tailscale networks.
The researcher tested Tailscale 1.104.2 and headscale 0.29.5 between October 22 and October 24, 2026. The most serious group involves Tailscale SSH. Its SSH server runs inside tailscaled, a background program with full root privileges on the machine.
#cybersecuritynews

Readers added context they thought people might want to know
The flaws require an already-approved device in the Tailscale network with SSH rules permitting access/forwarding; they enable post-compromise lateral movement and escalation inside the tailnet, not unauthenticated remote access from outside.
tailworm.com
brandefense.io/security-news/…
tailscale.com/security-bulle…
x.com/mmaunder/statu…
LayerV AI retweeted
New announcements are up at treasure.quest
Starting today, you'll also notice a change in how the site works. These are the first steps toward protecting the treasure hunt and Beyond the Map's Edge in the era of AI superintelligence.
This hunt has always rewarded human curiosity: your research, your instincts, your time in the field. I intend to keep it that way.
There's more to come. Head over and read the latest, and if anything gives you trouble, let me know in the comments.
LayerV AI retweeted

If you're looking to try out or test OpenNHP on Ubuntu, I put together an installer to make spinning up an NHP server a whole lot easier.
github.com/justingreerbbi/Op…
@LayerVai

"It works on my laptop"
Cool, now let someone else try it!
qURL 2.0 turns your local app into a private, expiring link. Send it to a friend, get feedback, keep building. No deployment needed.
What's new with 2.0:
- Private-by-default access, hidden from public scans
- Temporary, revocable links with configurable expiration
- Access for both people and AI agents
- No account required to get started (!!!)
Try it 👉 qurl.link/

Here's how you can share your local app in a single prompt: layerv.ai/vibe-coding/


LayerV AI retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
LayerV AI retweeted

To publish something on a paywalled site is to make it invisible. If AIs can't find it, then for all practical purposes it doesn't exist.
These two sentences aren't 100% true yet, but they will only get truer.
LayerV AI retweeted
The problem with traditional paywalls is that they hide the content from everyone, including the agents that will increasingly be the ones reading it.
One alternative is to make the resource cryptographically absent by default (nothing answering scans or crawls), then only materialize it for specific agents that present a short-lived, policy-bound grant. The content stays off the public web, but the systems you choose can still reach it for the duration of a task.
That's what @LayerVai does.
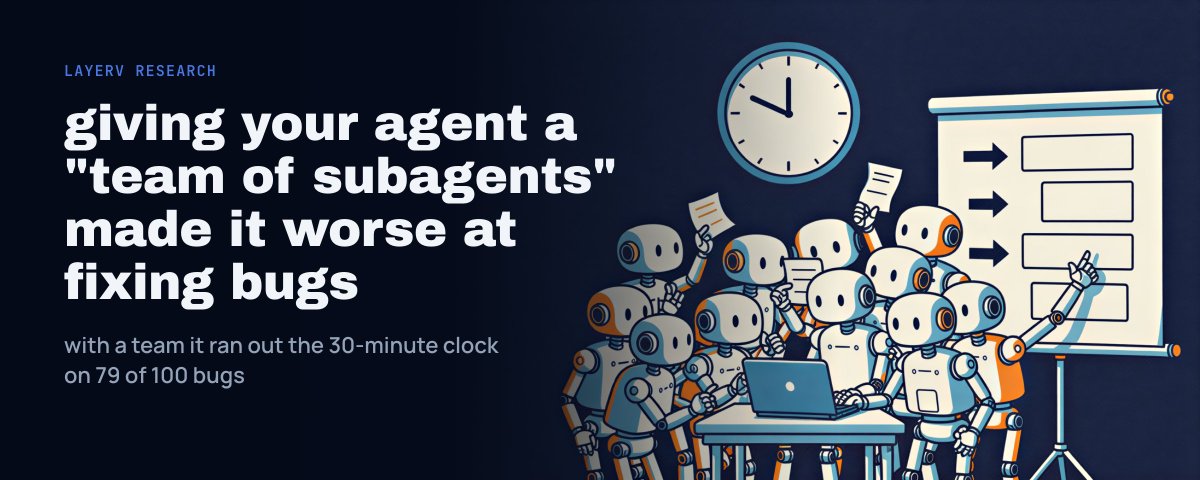
the robots discovered middle management 😳
check out how your robot can privately share resources with anyone using qURL! qurl.link/#qv2t1.3.1.1.eyJ2I…
What a great time for us to be building qURL v2!!
Imagine an attacker spends 30 minutes stealing your agent’s access link... but the link already expired 29 minutes ago 🤯


one of the amusing things about AI is that infra and security spent a decade getting everyone off long-lived static API keys and onto short-lived tokens
then OPENAI_API_KEY happened and we collectively forgot all of it
I get that managed identity and OAuth are harder but we really did speedrun back to secrets in .env
Read about how we do this: layerv.ai/use-cases/api-prot…