

🎮 Pokémon Content Creator 📰 News, guides, leaks & theories 🎨 Official artwork & Pokémon lore 🎁 Giveaways for the community 🌐 https://xitter.cf/t.co/yMJGGwJ2je
Area Zero
Joined November 2020
- Tweets16K
- Following146
- Followers53.9K
- Likes13.9K





Pinned Tweet
Get EXPIRED Shiny Koraidon & Miraidon Mystery Gifts for FREE in Pokémon Scarlet & Violet! ✨
A like and repost are super appreciated! 💖
youtu.be/DcsILmlg92U


The craziest part about the Switch 2 datamining situation is that people deep within the scene have known about this vulnerability for a long time, but kept quiet to avoid triggering a massive response from Nintendo.
Now, we're seeing people extract and publish code and data from multiple games at an unprecedented scale.
It's exciting for preservation and research, but it could also backfire hard. Nintendo will inevitably start patching whatever they can, potentially shutting down access to things the scene has been quietly working towards for months.
We're witnessing a goldmine of discoveries, but also potentially the beginning of the end for a lot of work that was never meant to become public this soon.

Pokémon Pokopia DLC datamine 👀
🍎 Dipplin & Hydrapple
Their event may happen BEFORE DLC 2.
🎄 Holiday Events
DLC 2 may introduce Christmas and New Year's Eve events.
🍰 Alcremie new flavour?
A new character similar to Mosslax may be introduced in DLC 2.
❓ New Wooper Form?
Wooper may also be getting a new form!
⚠️ All of this is subject to change, as the information was datamined from the current game build.


Pokémon Pokopia DLC: These Pokémon are coming in the DLC!
#10: Caterpie
#11: Metapod
#12: Butterfree
#84: Doduo
#85: Dodrio
#209: Snubbull
#210: Granbull
#225: Delibird
#300: Skitty
#301: Delcatty
#387: Turtwig
#388: Grotle
#389: Torterra
#488: Cresselia
#548: Petilil
#549: Lilligant
#653: Fennekin
#654: Braixen
#655: Delphox
#684: Swirlix
#685: Slurpuff
#868: Milcery
#869: Alcremie
#1011: Dipplin
Subject to change. This list was extracted from the current build, and more Pokémon may be added.


Sneaky Pokémon Winds & Waves teaser? 👀
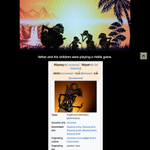
The official Asian Pokémon channel uploaded and promoted a video featuring traditional Indonesian shadow puppetry.
Interestingly, the four figures at the beginning are characters from Indonesian folklore. The largest appears to represent a traditional wayang figure, potentially linked to indigenous Javanese mythology that predates Hindu influences.
Could this be a subtle hint at something in Pokémon Winds & Waves? 🌊💨
🎥 youtube.com/watch?v=55LRNivE…


Notes from Mike Heskin (HexKyz, Atmosphère lead) regarding the vulnerability discovered in Nintendo Switch 2:
- The FS bug was actually known before. It made its way into Atmosphère a long, long time ago. I, at least, deemed it not exploitable, and it had just been there in the event something would change in FS that would make it useful. As it turns out, not even that was needed; it was exploitable from the get-go.
- The main obstacle to exploiting it was the FS heap layout: it is very scarce in useful pointers. The technique the LLM used was known too, but in a slightly different incarnation: you find something that can create new IStorage objects in the heap and take over their read/write pointers. This one used "BufferedStorage", but it's the same concept. The really difficult part was keeping the objects in the heap long enough and all our previous attempts (using other bugs, not this one) would land in empty memory.
- The whole heap groom dance is the truly novel and valuable contribution from the AI. It is an ungodly mess, but it proves that it can indeed work. It is also /barely readable inhuman horrors beyond comprehension/, which will make porting it quite challenging but doable nonetheless.
- From arbitrary read/write onwards, the rest is well-known and used before: set client PID to 1, mitm loader, stealing handles, etc.
- With FS access, you can use it as an oracle to dump any below-KIP-level binary, that is, games, apps and non-KIP sysmodules.
- You can't get keys or key material from FS.
- Escalating further up (kernel and so on) is just as hard from FS as it is from any other sysmodule.
- You may be able to compromise other KIPs, though. There's a technique they didn't consider/address in the blog post that could work.
- SmileBASIC isn't a requirement. Any entry point can be used for this, regardless of it being an S1 game, an S2 game or the browser. Obviously, this was developed for this SmileBASIC entry point, so people will rush to get it, but know this can be ported to anything. The FS command exposing the vulnerability is available pretty much everywhere.
- Lower firmwares still have undisclosed fun stuff that may or may not lead to deeper exploitation. In fact, we had an FS bug in 19 that let us dump part of its memory before, for example.
- There are other private FS bugs, but this one was proven, by far, to be the best. There is a very real chance this will be the only opportunity in a long time to exploit the system this deep.
- This exploit chain is the modern equivalent of the Switch 1 "nspwn". If you don't remember or weren't around, that was a flaw in FS that allowed arbitrary code execution in a similar fashion.
- This can, in theory, be made "untethered". It will require early system savedata manipulation, but we've proven before with a different set of bugs that it can be done. Ensuring that the heap has a useful layout on boot is a whole different can of worms. That will be the main challenge, if it is even possible.
There are a lot of pros and cons about updating or not for this.
On one hand, this is a very powerful exploit. You can't go any higher than FS within userland. That means anything above userland is out of reach for this exploit and compromising FS does not make it any easier to exploit, e.g., the kernel.
On the other hand, this gives you full control of userland, so dumping, modding, etc. All that is possible but will forever be locked up to firmware 23.0.1, as this will be promptly patched.
Lower firmware versions lack a lot of mitigations, which makes exploitation on those easier. This can become a relevant factor in the future. Do note that having access to every sysmodule code is considerably irrelevant for exploitation purposes: no other sysmodule is more powerful than FS.


