
Open to negotiate for threat hunting and threat analysis remote services
Joined May 2018
- Tweets219
- Following413
- Followers1.3K
- Likes3.7K




Pinned Tweet
🎯 New report: Battle of the Shadows: APT Wars in C2 Takeovers & Payload Verification
Uncover how elite APTs:
🔹 Defend their C2 infrastructure
🔹 Verify payloads to avoid takeovers
🔹 Engage in tactical "shadow wars"
link.medium.com/ZV6ibDXjdPb
#threatintelligence

How do you know this is Chinese? Just because of aliexpress?
This Post is from an account that no longer exists. Learn more
It seems like the Fortinet team is under heavy pressure as they’ve released a list of attacker IPs. However, I advise against blindly blocking these IPs. They might belong to CDNs or could have already been reassigned to legitimate services. Always verify before taking action.

🚨 After seeing the Snake driver sniff inbound traffic from a mail server using an incredible technique, now we encounter something new: a Linux kernel module that hijacks inbound network traffic to compromised systems.
Innovation in attack vectors is relentless.


Whenever you encounter a combination of interviews, video calls, and macOS, you might be targeted by a Lazarus campaign!

Initial infection chain of the new #Lazarus Willo Video Interview campaign is outlined in detail within the infographic
Releasing an in-depth blog abt the campaign soon. Happy New Year!
@banthisguy9349
#cyber #dfir #infosec #cybersecurity #malware #threatintel #cti #dprk #apt


Does anyone know which threat actor is attributed to stealing IIS machine keys for persistence (executing commands on a web server remotely through IIS insecure serialization)?
#threatintel
Security vendors with remote command capabilities could be a potential source of lateral movement and command execution.

Malware download and use of the Wazuh SIEM agent for remote access and telemetry harvesting.
"remote_commands" option
securelist.com/miner-campaig…
ref:
github.com/wazuh/wazuh


APT29 and APT28 separately targeted diplomatic entities within a year using decoy and phishing tactics, including a car sale lure. Each group employed distinct methods, such as hosting payloads on public services like webhook.
#threatintelligence
Thanks Unit42


CHM files are being used for Initial Access (Phish-to-Persist), particularly by DPRK-attributed threat actors and more recently in cybercrime operations.
#threatintelligence #threathunting

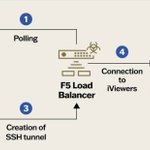
F5 The Perfect Place to Hide
China Threat Group Abuses F5 Load for Persistence. The investigation confirmed that the threat actor maintained a presence in the organizations on-premise network for about three years. The overall goal to the target network for espionage.
SygniaTeam

Enterprise Threat Hunting to catch and follow Lazarus recent campaign with passive DNS.
Validin provides extensive passive DNS records, which map domains to their associated IP addresses over time. This allows analysts to see where a domain has been hosted and track any changes.


1) Great talk in Positive hack days about OPSEC mistakes, challenges and techniques for my dear partnerships from positive technologies. I have talked about various Threat Intelligence tips and tricks and OPSEC mistakes like NOBUS WebShell, Operations Security (OPSEC),


Threat Hunting retweeted

You can either hunt for it or check and apply our Sigma rules
If you're unsure whether a detection idea is already covered by an existing rule, you can use the sigmasearchengine.com/, which was developed by my team member @ph_t__
We've also integrated the API of that service into the Sigma VSCode extension


Initial Access with Compiled HTML File (CHM) have been used by different TAs including APT37 and APT41.
For hunting/detecting them you should check hh.exe spawning mshta.exe or any other related LOBINs in Event ID 1 of Sysmon or 4688
See the execution flow in the following pics


APT28 has been targeting Iranian Embassy in Albania with the Browser In The Browser (BITB) phishing technique. Kudos to @_CERT_UA for first discovering this.


1/3 #APT37 recent sample with OneDrive C2 communications and PowerShell script block with internal create thread
#threathunting


2/3 Do not forget about PS script block logging and look for suspicious connections to cloud providers like OneDrive. To enable PS script block logging:
HKLM:\SOFTWARE\Wow6432Node\Policies\Microsoft\Windows\PowerShell\ScriptBlockLogging
$Name = "EnableScriptBlockLogging"
Value:1
You can reduce the initial access attack surface by disabling mounting of image containers like ISO files.
The policy :
•Computer Configuration => Administrative Template => System => Device Installation => Device Installation Restriction
#threathunting
