





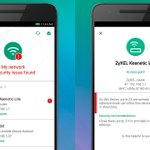

Android Campaign from Known OceanLotus APT Group Potentially Older than Estimated, Abused Legitimate Certificate
labs.bitdefender.com/2020/05…

Frida Cheatsheet and Code Snippets for Android
Quick reference guide for Frida code snippets used for Android dynamic instrumentation.
erev0s.com/blog/frida-code-s…
Android Reversing for Examiners
summit-labs.frida.ninja

Mobile Security retweeted

Published my slides and released objection 1.7.0 which includes all of the goodies you saw in my @defcon talk today! Thanks so much for everyone that attended and all of the support along the way. You rock! 🤘
github.com/leonjza/public-ta…
github.com/sensepost/objecti…
Mobile Security retweeted

Mobile click farm, birthplace of fake engagement.
Fake impressions, boosts new social media trends, ad fraud, helps create influencers, leaves fake review, spreads likes, shares, install apps...
xitter.cf/EnglishRussia1/status/…
Unpacking the Packed Unpacker: Reverse Enineering an Android Anti-Analysis Nqtive Library
youtu.be/s0Tqi7fuOSU
By @maddiestone
@BlackHatEvents USA 2018
Mobile Security retweeted

Finally! After many months of procrastinating, RE #iOS Apps Part 2 is out! Learn how to #dump classes, #disassemble the binaries with #Hopper and modify the apps' behaviour at runtime with cycript iOS 11 edition! #security #appsec ivrodriguez.com/reverse-engi…
USB Restricted Mode at iOS 11.4.1 Beta blog.elcomsoft.com/2018/06/i…

Mobile Security retweeted

"Ghost in the Machine: Challenges in Embedded Binary Security" youtube.com/watch?v=pMRa8xDF… great work by Jos Wetzels, @bl4ckic3! Must see!

Mobile Security retweeted

Inspired by @maddiestone I decided to try my hand at hardware reverse engineering basics: maldr0id.blogspot.com/2018/0…
Mobile Security retweeted
Just don't install them!
16 apps from Google Play right after lunch request SMS subscription payment (~$2.7+/week). Even though apps can't run in every country they still have more than 100K installs in total.
First unsubscribe then uninstall.


Google is starting to require that OEMs roll out regular security patches
xda-developers.com/google-re…
Rowhammer in the wild:
GLitch is first instance of a remote Rowhammer exploit on ARM Android devices
lnkd.in/eCDn2TK
Android Reverse Engineering Tools: Not the usual suspects
virusbulletin.com/blog/2018/…
by @cryptax
Android App Vulnerability Benchmarks
bitbucket.org/secure-it-i/an…
Apps with vulnerabilities related to Crypto, ICC, Networking, Permission,Storage, System, and Web APIs.
Huawei Mate 9 Pro
Mobile Pwn2Own 2017 Explanation
labs.mwrinfosecurity.com/ass…
by @mwrlabs

KSMA: Breaking Android kernel isolation and Rooting with ARM MMU features
blackhat.com/docs/asia-18/as…
#MobileSecurity #Android #Root #BlackHat