

Your reliable & simplified #passwordless solution provider. Prevent #credentialstuffing & password attacks. Give your users the best login experience
Joined February 2021
- Tweets1.1K
- Following665
- Followers275
- Likes348





Pinned Tweet
⚙️ MojoAuth = 1 API for Email, SMS, WhatsApp & Authenticator OTPs.
⏱ Integrate in hours, not months.
🌍 Global delivery <3s.
👉 Build faster: mojoauth.com
#OTP #Security #SaaS


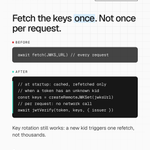
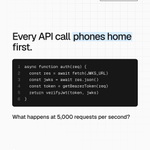
This middleware fetches your IdP's signing keys before it checks any token.
Staging: 5 calls/s. Fine.
Production: 5,000 calls/s to your IdP, a round trip on every request, and one IdP slowdown fails all auth.
What would you change?
#javascript #oauth


Set-Cookie: sid=8f3a91c2
Sent over HTTP. Readable by any script. Carried on cross-site requests. Alive until the browser quits. A subdomain can plant a copy.
Five words fix it: __Host- Secure HttpOnly SameSite=Lax Max-Age
How many does yours have?
#websecurity #webdev

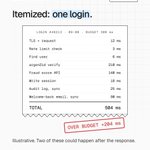
One login, itemized: 504 ms against a 300 ms budget.
Two lines on this receipt could happen after the response. Which two?
#performance #backend

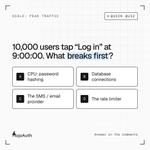
10,000 users tap "Log in" at 9:00:00. What breaks first?
A) CPU: password hashing
B) DB connections
C) SMS/email provider
D) Rate limiter
Reply with a letter and why.
#backend #systemdesign

Monday, 9:00. Login p99 is 14.2s.
Pods at 100% CPU. New pods need 3 min.
Marketing just emailed 2M users.
The load test? One user, 10,000 times.
Six messages. Three minutes. All fixable on Friday.
Which one would you have caught?
#sre #incidentresponse #devops
50% CPU: a login waits about 2× its work time.
90% CPU: 10×.
99% CPU: 100×.
Queues don't get slow slowly. They fall off a cliff.
What CPU target do you scale at?
#sre #performance #backend


19 MiB per argon2id hash: OWASP's minimum.
That's memory, not CPU. 1,000 logins hashing at once need about 18.6 GiB. Are your auth pods sized for that?
#security #backend #capacityplanning

RAM in use = hashes in flight × memory per hash. 1,000 × 19 MiB = 19,000 MiB ≈ 18.6 GiB.
Hashes in flight = logins per second × seconds per hash (Little's law). At 100 ms per hash, 1,000 in flight means 10,000 logins/s; at 500 ms per hash, 2,000/s.
Where the numbers come from:
19 MiB (m = 19456 KiB), t = 2, p = 1 is the minimum argon2id setting in the OWASP Password Storage Cheat Sheet. Memory-hard by design: the cost is RAM, not only CPU.

• 100 ms per hash is a scenario. On a current server core the same setting lands anywhere from tens of ms up; that's why the post says "measure yours".