

Building @ Monetise | Architect of Unitflow for AI-native firms. Documenting the journey from Start to Supersonic. https://teapawt.org/t.co/7hbtLTebIv
London
Joined June 2025
- Tweets2.6K
- Following861
- Followers810
- Likes15.1K





Pinned Tweet
AI works, that's no longer the question.
The question is, how do you turn AI into a business? Over the last year I've noticed something interesting.
AI doesn't become strategic because the models get better, it becomes strategic because new stakeholders enter the conversation.
The engineer asks:
Can we build it?
The CFO asks:
What does it cost?
Treasury asks:
What's our financial exposure?
Operations asks:
Which workflows create value?
The CEO asks:
What's the return?
Those questions create a need for operational visibility.
Visibility creates accountability and accountability creates ownership.
Ownership turns AI from an experiment into business infrastructure, that's the transition I'm exploring.
4
37
2,128
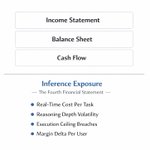
A token is a unit of consumption, not a unit of business value.
An AI agent can burn 100,000 tokens, call 12 tools, retry 5 times and still fail.
Another execution might use twice the compute and deliver an outcome worth 10x more.
So why are we still measuring AI economics primarily in tokens?
The metric that matters is cost per successful outcome. That's where the next layer of AI infrastructure needs to focus.
FT: The token bill, why AI agents need a new economics of information.
ft.com/content/fc2f8d39-a53f…

4
4
67
We're teaching AI agents how to do more, but we're not teaching them when it's no longer worth doing. Think about it.
An agent decides:
→ Which tools to use.
→ Which models to call.
→ How many times to retry.
→ Whether to keep reasoning.
→ When to continue.
→ When to stop.
And every decision has an economic consequence, a budget cap tells you how much an agent can spend.
Observability tells you what happened, policies tell it what's allowed.
The more important question is:
Is the next action actually worth taking?
That's the problem we've been exploring with Unitflow at Monetise.
We believe autonomous AI needs more than usage tracking and spending limits.
It needs an economic governance layer that understands execution, resource consumption, task progress and expected outcomes.
Not just controlling how much AI spends, but understanding whether the work it's doing makes economic sense.
Because giving AI more autonomy is relatively easy, making that autonomy economically sustainable is the real challenge.
More to share soon, we're getting closer to showing you what Unitflow looks like in practice. 👀
8
8
195
The AI boom has a $40bn question:
Who pays for all this capacity and where's the economic return?
Billions are flowing into chips, servers and data centres. Meanwhile, communities are pushing back against the land, power and infrastructure AI demands.
More GPUs.
More megawatts.
More tokens.
None of these tell us whether AI is creating economic value. The race isn't just about who builds the most capacity, it's about who makes that capacity pay off.
We're measuring what AI consumes, it's time to measure what value it produces.
3
93
Revolut reportedly cut AI inference costs by ~90% with self-hosted open models.
Impressive, but cheaper intelligence doesn't automatically mean cheaper work.
Retries, excessive reasoning and unnecessary tool calls can quickly erase those savings.
Not every task needs a frontier model, some need a smaller one and some need no AI at all.
Real optimisation isn't cost per token, it's cost per successful outcome.
Know which intelligence to use, when to use it and whether the work was worth the cost.
8
8
233
For those interested in the Revolut example, David Abitbol shares how Revolut reduced AI coding inference costs by around 90% using self-hosted open models.
Worth watching, especially the slides explaining the economics.
ai.engineer/talks/Ok6QdZHCcI…

2
97
AI is taking our jobs, well maybe not.
Maybe this was the AI opportunity all along.
Happy weekend, builders.
wired.com/story/comedians-ma…

1
6
98
Enterprise AI is entering its accountability phase. The question is no longer:
"Can we use AI to do this?"
It's becoming:
"Can we prove it's actually worth doing?"
Goldman Sachs has reportedly restricted access to certain AI coding tools following productivity and risk reviews.
BCG's research suggests that while AI value creation is improving, only 5% of companies have the full controls needed for autonomous agents.
This doesn't mean enterprise AI is failing, it means the honeymoon is ending, adoption isn't proof of value and usage isn't ROI.
Automating a task doesn't automatically make the business more profitable. Enterprises need to understand what AI actually delivers, what it costs and what risks come with it.
Moving forward AI adoption will be about proving what it can do, by proving the value it brings.
A couple of interesting developments behind this:
• BCG's research on enterprise AI value creation and governance: bcg.com/publications/2026/th…
• Goldman Sachs' reported restrictions on AI coding tools following productivity and risk reviews: bloomberg.com/news/articles/…
Worth reading in the context of where enterprise AI adoption is heading.

4
80
Most AI governance happens at two points:
Before execution.
Policies, permissions, budgets and risk assessments.
After execution.
Logs, audits, incident reports and post-mortems.
Both are necessary, but autonomous agents create a third requirement, governance while the system is running.
What happens when an agent starts repeating actions?
When resource consumption increases, but progress doesn't?
When a task becomes riskier than expected?
When the original plan no longer makes sense?
Waiting for the final report is too late and no policy written in advance can anticipate every execution path.
The real challenge is turning governance principles into controls that respond to what is actually happening.
Because with autonomous AI, trust isn't just about what you allow a system to do, but knowing when to let it continue, when to intervene and when to stop.
That's the layer we're working on with Unitflow.
3
9
156
A $5 AI task can be a waste of money.
A $50 task can be a bargain.
So why are we governing AI agents with budget caps alone?
A spending limit tells an agent when to stop spending, it doesn't tell it when to stop wasting time.
The real question isn't just how much an agent spends, it's whether the next action is worth it.
2
7
145
An AI agent can succeed and still waste 90% of its budget.
30 tool calls, 5 retries, correct answer.
Everyone celebrates the result, nobody questions the execution. We're measuring whether AI gets the job done, not whether it was worth the cost.
Task success isn't economic success.
5
12
235
Anthropic’s S-1 reveals a striking shift in AI economics.
H1 2026 revenue: $16.3B, up from $1.16B a year earlier.
Compute & infrastructure costs: $8.9B, up from $2.3B.
Scaling is real. But what does this mean for the economics of AI execution?
Cheaper models ≠ cheaper workflows.
What to look for is; cost per successful outcome and the business value it creates.
1
9
215
Source: Anthropic’s S-1 👇
Read the filing
The bigger question isn't just how efficiently a model uses compute. It's how efficiently an AI-enabled workflow turns that compute into business outcomes.
That's the layer of AI economics I'm exploring with Monetise.
sec.gov/Archives/edgar/data/…
6
109
An AI agent can succeed at its task and still be a terrible business investment.
30 unnecessary tool calls
5 retries to solve one problem
10x the cost because nobody defined "good enough"
Every step looks reasonable, the economics don't. Task success ≠ economic success.
As AI agents become more autonomous, we need to measure three things:
→ What did it consume?
→ What did it achieve?
→ Was the cost justified by the outcome?
Because the real unit of AI efficiency isn't the token, it's the successful outcome.
3
10
161
AI models will change, tools will change, infrastructure will change, but the real advantage won't come from choosing the right model.
It will come from understanding how AI actually performs in production:
Which workflows create value
Where costs leak
Why failures happen
When more autonomy stops making economic sense
That operational knowledge compounds with every execution, regardless of which model runs it.
The lasting advantage isn't owning the intelligence, it's knowing how to operate it economically.
1
8
160
Static rules can tell an AI agent what it's allowed to do, they can't tell it whether continuing still makes sense.
As execution unfolds, costs rise, progress stalls, and risks change.
Real governance needs a feedback loop; observe, reassess, adapt or stop.
Rules define the boundaries, Runtime intelligence governs what happens inside them.
2
8
156
An AI model can pass every evaluation and still be part of a failing production system.
The model reasons correctly.
The tool works as intended.
The permissions are valid.
Yet the agent repeats actions, follows the wrong path, or keeps working long after the outcome is good enough. The problem isn't necessarily any individual component, it's what happens when they interact over time.
AI assurance can't stop at evaluating what a model can do. We also need to evaluate how the complete system behaves during execution, when it should continue, adapt, or stop.
Passing an evaluation proves capability, it doesn't prove control.
4
8
192
Interesting AI developments last week:
Anthropic has given independent evaluators from METR unusually deep access to its internal systems to assess AI risks.
Important question to explore, but evaluating a model before release and governing an agent in production are different challenges.
Model evaluation can reveal what a system is capable of, but production controls are needed to help answer what it's doing, what permissions it has, how its behaviour is changing and when intervention is necessary.
We need both, AI assurance can't end at the evaluation report, it has to continue into execution.
2
8
224
The AI industry just made voluntary commitments on frontier AI safety at the White House.
That's a starting point.
But there's a difference between agreeing on how AI should behave and being able to enforce those principles when an agent is running.
Who defines its boundaries?
Who detects when behaviour changes?
Who can intervene before a failure compounds?
And what evidence proves the controls actually worked?
Policies define intent, evaluations test capability, but autonomous systems also need controls that operate at runtime.
Responsible AI can't stop at what companies promise, it has to show up in what their systems are allowed to do.
apnews.com/article/ai-safety…

8
157
About AI autonomy, “Should we let the agent do it?”
probably too binary.
Autonomy is a spectrum.
Suggest → execute → execute with limits → execute and escalate exceptions → fully autonomous. Different tasks deserve different levels of autonomy.
A marketing draft?
High autonomy.
A supplier recommendation?
Maybe.
A payment?
Very different conversation.
A regulatory decision?
Probably very different again.
The interesting enterprise AI question would then be:
“How much autonomy does this task deserve?”
Much better starting point.