

We secure software with deep-dive audits, cutting-edge research, and in-depth trainings. Secure your solana program with Riverguard @ https://xitter.cf/t.co/VmxVHzx2U2 🏞️💂
Germany
Joined August 2021
- Tweets388
- Following46
- Followers5.6K
- Likes391




Pinned Tweet
Introducing Riverguard 🏞️💂
A new security tool for Solana program deployers... 🧵
riverguard.io

Happy to publicly announce the new advisory!🎉

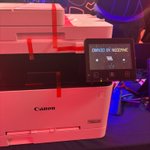
[ZDI-26-280|CVE-2026-4682] (Pwn2Own) HP DeskJet 2855e JobStatusEvent Stack-based Buffer Overflow Remote Code Execution Vulnerability (CVSS 8.8; Credit: Team Neodyme (@Neodyme)) zerodayinitiative.com/adviso…
Small update on the unfolding Drift timeline: as surfaced in other threads (eg xitter.cf/TheSoftwareJedi/status…), the malicious proposal and execution were nonce transactions (those can be signed offline and not immediately submitted to the network).
The thing about nonce accounts is, that they have an authority set.
So we can go look on-chain to find nonce accounts that are configured to work with any of the new and old drift multisig members. When we do that with dune, we find *three* nonce accounts:
One created March 31st, used in exploit for 6UJb, member of new multisig:
solscan.io/account/EmYEryTDX…
And two created March 24th. One used in exploit for 39Jy, member of old multisig: solscan.io/account/7s7s6saC5…
And one NOT used in exploit, for a key in old multisig 45cZ...: solscan.io/account/41zpDnNbC…
This can be an indication that they were prepared to attack the old multisig before the migration happened.
There are two additional nonce accounts created by the same authority as the above three, that seem also related to the attack but are not multisig members.
You also don't have to set up the nonce account before signing a transactions. It is perfectly possible to keep that also stealthy, and only create the nonce account once you are ready to submit the transaction. But it appears the attacker didn't do so, and thus "leaked" all keys he wanted to be able to create offline transactions for.


i missed the fact that these drift related squads txs had durable nonces... that changes things. perhaps all my wallet security rants are misapplied here.
the drift admins may not have completely exposed their keys. just signed a rogue tx sometime in the last 10 days / 2 days respectively. theres no way to tell when it was signed, just sometime in the window.
so if thats the case, perhaps proper wallet security was in place - but they were somehow tricked into signing something without knowing. a key thing to look at here would be a fake squads page, since it seems like those wallets were signing legit squads txs during the window.
wallet1: solscan.io/account/39JyWrdbV…
nonce1: solscan.io/account/7s7s6saC5…
nonce1 used in attack: solscan.io/tx/2HvMSgDEfKhNry…
wallet2: solscan.io/account/6UJbu9ut5…
nonce2: solscan.io/account/EmYEryTDX…
nonce2 used in attack: solscan.io/tx/4BKBmAJn6TdsEN…


There is no evidence of a squads compromise or a bug in the on-chain Drift program. This looks like a well executed attack on the multisig members.
Relevant transactions:
Transfer of Admin to new Multisig: solscan.io/tx/9zJGhyotEes1Ni…
Insurance Fund withdrawal (created): solscan.io/tx/5rvb1uJ3Qz9W78…
Withdrawal approved: solscan.io/tx/3rwkPMGwwMcWQZ…
Withdrawal executed: solscan.io/tx/BkUZ8nss1api3b…
Admin key transfer (created + approved): solscan.io/tx/2HvMSgDEfKhNry…
Admin key transfer (executed): solscan.io/tx/4BKBmAJn6TdsEN…
Fake market creation: solscan.io/tx/4a5962Rdqd9pkX…
Funding of attacker by CVT mint authority: solscan.io/tx/iYoYSB8BFCne3S…
First withdraw: solscan.io/tx/2jCAE2SakEHtaZ…

Excellent discussion on the current and future landscape of Solana auditing. Thank you @mikemaccana!

We spoke with Marius at @Neodyme - auditors for Anza, Jump, Marinade, Drift and more - on the past and future of Solana program security.
New blog post 🚨
We're diving deeper into a privilege escalation issue (CVE-2024-476) in Lenovo Display Control Center used across Windows enterprise environments.
👉 Read the full breakdown: neodyme.io/en/blog/lenovo_dc…

Neodyme retweeted

We've completed a security audit of Rusty Crystals with @Neodyme .
Rusty Crystals is our NIST Level 5 quantum secure Dilithium (ML-DSA-87) signature library (with full HD wallet support.)
All issues resolved.
The audit was led by Ruben Gonzalez, PhD in post-quantum cryptography.
Dr. Gonzalez's PhD advisor was Peter Schwabe, co-author of Dilithium.
Dilithium is the lattice-based digital signature scheme we've built @QuantusNetwork on.


Drones are hot - their security is not.
Here is how removed the NAND, dumped firmware, and reverse-engineered ECC on a consumer drone. Stay tuned for part 2!
neodyme.io/de/blog/drone_hac…
