

Non-Standard human, husband, and grateful father. USAF veteran. I mostly tweet nonsense, and my tweets are attributable only to me, no other entity.
Austin, TX
Joined February 2015
- Tweets5.8K
- Following1K
- Followers595
- Likes20K




Pinned Tweet
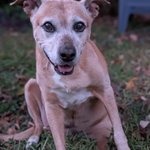
Rest in Peace my love. You protected our family, helped my wife and I start our family and will forever be loved and missed.
Amaya Jones 05/2014 - 09/2026

Shane Jones retweeted

Fair winds and following seas, Stan Nelson. We will remember you.

Readers added context they thought people might want to know
Stan Nelson, a D-Day Navy veteran shown in the image, died Nov. 20 2025 at age 105 and was not the last survivor of the invasion.
varsity.startribune.com/stan-nelson-ch…
kstp.com/kstp-news/loca…
en.wikipedia.org/wiki/John_C._R…
mysanfordherald.com/article/2053,l…
Shane Jones retweeted

Released TpDirectCallbackHijack, a process injection PoC where you overwrite one function pointer inside an existing thread pool object (TP_IO / TP_ALPC / TP_JOB), post a single completion packet, and the victim's own worker thread dispatches your shellcode. Restore stub puts the pointer back on the way through, so the thread pool keeps working.
No remote thread, no Get/SetThreadContext. Pool Party adjacent. Based on @_0xDeku's research.
github.com/Maldev-Academy/Tp…


Shane Jones retweeted

Make your payload "sleep" to look like any real Windows activity.
BusyWork is a Rust library that swaps each pause for randomized real work - hashing, file enumeration, registry queries, DNS lookups - drawn from 76 tasks across seven categories with ±30% jitter on every parameter.
No two "pauses" produce the same API sequence, and no timing primitives survive in the compiled binary.
A post by Daniel (@PatchRequest)
Source: patchi.fyi/blog/busywork-sle…
#redteam #blueteam

Shane Jones retweeted

The bypass of LDAP Signing Through Reauthentication described in @SpecterOps blog also works with pure Kerberos relay. too ;-)


Shane Jones retweeted

This is immersion breaking, this has never happened in Miami

GTA 6 includes a fully functional bus and train transportation system.
Buses have specific routes & times when they are meant to arrive at each stop.
(Source: gamesradar.com/edge/gtavi-co…)

Shane Jones retweeted
Sources tell WIRED that an Accenture employee’s personal Claude agent ran on a DOD network for two months before it was identified and the vulnerability could be patched. buff.ly/nUjCkPs

Shane Jones retweeted

Your Break-Glass Account Is Excluded From Every Policy. It Still May Not Get You In.
ridgelinecyber.com/blog/brea…


I want one

JUST IN: Palmer Luckey's genetically modified military dog startup, Warhound, comes out of stealth, aiming to create enhanced canines for the U.S. military.


Readers added context they thought people might want to know
This is NOT Palmer's company at all, his company Anduril is only supplying the tech for the dogs, and this is a wholly owed Collosal entiity
x.com/palmerluckey/s…

Shane Jones retweeted

Very cool technique to bypass SMB signing, appears to be patched on recent Windows versions.

I wrote up a way to defeat enforced SMB signing for relay.
It abuses a documented SMB re-authentication behavior.
I'm surely missing nuance and prior art. Corrections welcome.
Writeup:
blackfield.ch/blog/defeating…
PoC:
github.com/aas-n/reauthx

Shane Jones retweeted

Until we get confirmation Jira is safe from the PHP vulnerability, I don’t think anyone should be opening tickets or assigning me work.
Shane Jones retweeted
🦛🦛🦛Microsoft patched PetitPotam this October: EFSR now only resolves local paths. This means WebDAV to LDAP Coercion is fixed!
Remaining methods for clients are WSP (coercing SMB) and PrinterBug (coercing RPC), but both cannot be relayed to LDAP 💀💀💀
Shane Jones retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Shane Jones retweeted

redteamfortress/killerland: Collection of reversed vulnerable drivers weaponized into process killers. PPL won't save you. github.com/redteamfortress/K…

Shane Jones retweeted

SyscallRevenant - a new method of performing clean indirect syscalls. The main component resolves System Service Numbers (SSNs) and syscall instruction addresses dynamically
github.com/SilentisVox/Sysca…

Shane Jones retweeted
CloudKeyVaultEvents: Azure Key Vault Logs, Schema and KQL Hunting, by. @BertJanCyber #DFIR
kqlquery.com/posts/cloudkeyv…
Shane Jones retweeted
Token Theft in Microsoft Entra ID, by @insinuator
Part 1: Threat Landscape and Attack Techniques insinuator.net/2026/08/token…
Part 2: Continuous Access Evaluation insinuator.net/2026/09/token…
Part 3: Token Protection insinuator.net/2026/10/token…