

Not fun at parties. Not good with people. Social Democracy. Converse lots in others' replies. Shitposter. Follow at your peril.
Montreal
Joined November 2014
- Tweets42.8K
- Following1.4K
- Followers378
- Likes17.7K




Emo Support Nihilist🌎 retweeted

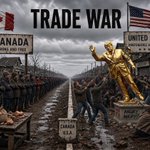
Obama: "That well-known evil empire Canada. That historical adversary of ours. Canada! *laughs* It's your neighbor. It's a few minutes' drive over the bridge! These are the people who gave us Martin Short and maple syrup. They are the nicest people! And someone we've gotten them so mad."
Emo Support Nihilist🌎 retweeted

This Forbes investigation is a must-read.
Donald Trump pulled in roughly $1.4 billion from crypto in 2025, plus more than $200 million from real estate, and faced a projected tax bill north of $500 million. So his company donated the "development rights" to his Jupiter, Florida golf course to a land trust, argued the course was a natural habitat worth protecting, and kept right on running the club. Forbes estimates the write-off could land around $825 million.
He has done this at least five times since 2005. New York's attorney general alleged two of those appraisals were inflated. In Doral, he claimed a deduction of up to $323 million, more than double what he paid for the entire resort.
A month after the Jupiter deal, he sued the IRS. The settlement his own Justice Department signed bars claims against him over matters that "could be pending," language that appears broad enough to cover this year's taxes. A federal judge found the case was brought to manipulate the judicial process. And the man now running the IRS, who took the job as this deal was being assembled, has a home backing onto those same Jupiter fairways.
This is absolutely ridiculous. Nobody should be able to use the presidency to write his own tax bill.
forbes.com/sites/danalexande…


Emo Support Nihilist🌎 retweeted
in light of the AI cyberattack mayhem going on right now, it's a good time to reshare Karapthy's Digital Hygiene guide
probably the most important thing you can read this week:
> use a password manager for every account
> set up physical security keys so attackers can't log in
> enable face id and fingerprint everywhere
> randomize your security question answers
> encrypt your hard drive
> get rid of unnecessary smart home devices
> switch to signal for private messaging
> use brave instead of chrome
> switch to brave search instead of google
> mint virtual credit cards for every purchase
> get a virtual mailing address
> never click links inside emails
> use a vpn on public wifi
> block ads and trackers at the dns level
> install a network monitor to see which apps are spying on you


All these hacks/exploits happening all pretty much at once pretty much seems like they're coordinated from one source, yes?
Who done it?
Maybe we need to shut down the Internet.

🚨 BREAKING: LINUX IS NOW FACING TWO CRITICAL SECURITY VULNERABILITIES, AND THERE ARE NO OFFICIAL KERNEL FIXES YET.
Both rated 9.0/10 in severity.
One could allow hackers to take control of vulnerable servers WITHOUT EVEN LOGGING IN.
And the most alarming part? The flaws were made PUBLIC before patches were ready.
Here's what's happening:
→ TWO CRITICAL RCE FLAWS: Both affect KSMBD, Linux's built-in SMB file server.
→ NO PASSWORD REQUIRED: One vulnerability could allow unauthenticated attackers to execute malicious code on vulnerable servers.
→ KERNEL-LEVEL ACCESS: Successful exploitation could potentially give attackers control within the Linux kernel itself.
→ NO MAINLINE PATCH YET: Both vulnerabilities were publicly disclosed before official kernel fixes were available.
→ DISCOVERED BY AI: Trend Micro's AI-powered security scanner identified the flaws.
→ SERVERS AT RISK: Linux systems running the vulnerable KSMBD service need immediate attention, especially if port 445 is exposed.
First PHP. Then Node.js. Then GitLab. Then Python.
NOW LINUX.
And this time, the vulnerabilities are PUBLIC before the fixes are ready.
If you manage Linux servers, CHECK YOUR EXPOSURE NOW.
Readers added context they thought people might want to know
KSMBD is a rarely used optional in-kernel SMB server distinct from the common Samba implementation; it is not enabled or shipped by default on major distributions like RHEL, and the flaws affect only systems explicitly running it with port 445 exposed.
thehackernews.com/2026/10/two-cv…
threatlandscape.io/blog/ksmbd-zdi…

I like this. Keep frontier model use very limited and private, prevent distillation and release amazing products/ideas from the models.

I getting a feeling that OpenAI and Anthropic soon will ditch customers completely, just use their models 100% internally and go all in on frontier science and engineering research
Like eg if they actually solve quantum gravity or cure cancer, and own the right to license the solution, can you imagine the ROI behind that? No more listening to users bitching about usage or model nerf or whatever
It should genuinely worry the hell out of everyone that Trump is openly leaning into his Putin relationship right as it looks like his party is about to get destroyed in the midterms and he is about to be subject to investigations and impeachments.
"My good friend Donald. You are such a great President. The greatest President. America was a dead country before your Presidency. Now, it is the hottest country. For the sake of America, you must stay in office forever...like me. I will help you. Here's what you have to do..."


Emo Support Nihilist🌎 retweeted

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea


a dangerous 🤡🤡🤡

Trump: We were in the midst of negotiating and a lot of stupid people said why aren’t you putting Russian sanctions—
Collins: But you said you didn’t give anything for his release
Trump: If I didn’t do that, you wouldn’t have him coming back.
Collins: So you did give something.
Trump: You don’t know anything. You’re fake news CNN.
Collins: You’re saying you lifted the sanctions in exchange for his release?
Trump: You don’t know what you’re talking about. You’re a low IQ person. You’re a dummy.
Seriously, the reason suburbanites on average don't have businesses within walking distance is not a zoning issue, it's density.
Higher density of businesses needs denser customer bases. You have to drive not because of zoning, but because the customers per sqkm is low.

Emo Support Nihilist🌎 retweeted

Americký karikaturista Jeffrey Koterba má jasno. A každý normální člověk taky.



Emo Support Nihilist🌎 retweeted

[Original in Polish. Text in the image translated and edited using AI]
🤖 Made with AI
