


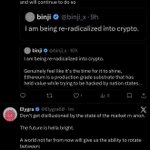



Procrypt retweeted

Phishing email seems to have gone out to Foundation Passport users.
No official word from @FoundationHQ yet.
Do not click any suspicious links.


Procrypt retweeted

Since I keep getting asked about day trading to this day, I decided to put all concepts from my old blog and courses together into a new post with some fresh examples, all free to read.
blog.tradingriot.com/p/sligh…
/end

Procrypt retweeted

Once again reminding the hardware wallet retards that the risk that becomes real when you leak people’s SHIPPING INFORMATION is not phishing. It’s fucking PHYSICAL ASSAULTS AND KIDNAPPINGS.

We owe you an apology.
On October 20, we detected unauthorized access to our official website. After verifying API activity with Shopify, we confirmed on October 23 that a third party obtained customer shipping information. You trusted us with those details, and we're sorry we didn't keep them safe.
Exposed: names, contact details, shipping addresses, and order details (items and prices).
Not exposed: payment card or bank details, recovery phrases, private keys, or wallet passwords.
We've blocked access, fixed the vulnerability, opened an investigation, and are emailing affected customers.
Scammers may pose as Keystone by phone, text, email, or mail, offering refunds, replacement devices, or "fixes" for your order or address. None of it is from us.
NEVER share your recovery phrase or private keys, and NEVER enter your recovery phrase into a device you didn't order. We will never ask for them. Don't click links in unexpected messages. Type keyst.one yourself.
A detailed report is coming soon.
Until then, trust only our official channels. If anything feels off, email [email protected]. We'd rather hear from you than have you take a chance.
Again, we're truly sorry to everyone affected.


Procrypt retweeted

a discussion

It’s a bit brutal but BTC is probably going to be the big winner of the AI revolution. I don’t think it will suffer any hacks, the scripting language formal verification is very advanced and work in formalizing the protocol too. Nodes running on different hardware make it very robust against hardware vulnerabilities, and their sources are probably one of the most audited code in the world. Combine that with self sovereignty which protects against political backslash from K shaped economy and acceleration of margins flowing to capital, I don’t see much else. To be honest this is my macro view but it’s a pretty grim one.

Procrypt retweeted

Bullshit fearmongering. 0days have always been abundant. These bugs are now being found and patched at an amazing rate, instead of being used by adversarial groups. Be happy, because most organisations have no clue how to run their infrastructure or detect anomalies

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea


Procrypt retweeted
Admin keys for Swell DAO's swETH and rswETH appear to be compromised (railway related?)
* Attackers are raising NAV by max 1% (unbacked) each hour
* Four malicious upgrade contracts have been deployed (although not queued yet through multisig) that could steal approx 2500 ETH


Procrypt retweeted

In the last 24 hours:
1. iPhone 11 through 16 are apparently vulnerable to remote attacks.
2. SSL certificates are broken until browsers remove eMudhra CA.
3. PHP >9 vulnerability CVE published (tomorrow).
The world is about to witness things that have never been seen before.
Readers added context they thought people might want to know
The post's iPhone claim is inaccurate; a leaked Cellebrite forensic tool targets a Bluetooth bug patched in iOS 26.5 and does not affect updated devices. The eMudhra CA and PHP issues are real incidents but framed sensationally.
justin.sh/blog/2026/10/c…
blog.mozilla.org/security/2026/…
php.net
Procrypt retweeted

it's like claude but for instruments
squishlabs.gumroad.com/l/oki…
a synth that becomes whatever you type, live in your DAW
spread the word, try it out (free) and lemme know what u think 🤓
Procrypt retweeted

Ledger spy implants went from a bunch of wires manually soldered to mass production circuit boards made to blend with the official hardware.
teapawt.org/MagicalTux/status/2100…

Spy implant in @Ledger Nano X, back in the days and now, that's quite an evolution.
Old implant picture from grandideastudio.com/portfoli…


Procrypt retweeted
Hi. If elliptic curves are broken so that any exposed public key leads to compromise and it's by a financially-motivated hacker who’s top priority is to steal crypto, the entire fucking world is going to zero.
Having your magic internet coins in bunker mode is not going to help you.
It would mean some random ass fucking cyber criminals > every developed nation state and private corporation in the world.

Procrypt retweeted

we have a few spots left. shoot your shot and see if you get accepted.
luma.com/0q5jmdd7

Procrypt retweeted

It’s beautiful to know that Robbie himself will absolutely hate this ❤️

Five years ago, I found a Lost Robbie in a drawer.
One of 300 frames of Robbie Barrat’s AI art, given away at Christie’s in 2018.
Today I’m launching a tracker for the finds, the sales and the story.
How many other drawers hold one?
@videodrome
