

CS https://teapawt.org/t.co/YnvgTP5xEN. & https://teapawt.org/t.co/iAAKsMumDy. Martial Arts enthusiast. Public Speaker. Blue-Teamer. 3-Time honorable & super-honorable #SANSHolidayHack mention. Eternal seeker of knowledge.
Joined December 2014
- Tweets2.5K
- Following177
- Followers329
- Likes3K




Sam King retweeted

Old exploits, new targets. Shahar Tal and Yarden Porat showed what happens when classic vulnerabilities meet AI agents, closing out a fantastic first day at BlueHat IL.


Oligo Security present "ShadowMQ".
Key takeaways:
- AI is mostly open-source. And works with sensitive data.
- AI vendors borrow code that works from each other.
Which means that if a vuln / misconfiguration is found in one - it's gonna be in all others.
#BluehatIL #ZMQ #AI


New ETW logs from #Microsoft ! Find out:
- Who changed GPOs, what was changed
- Who made what LDAP queries
- Who performed DCSync attacks and what was replicated
- View new Kerberos ticket fields (suspected Golden ticket)
#DFIR #BluehatIL #ETW #EDR


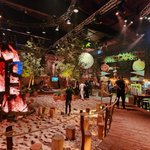
As a person with Canadian roots, I approve this camp setting production message! 😁
#bluehatIL


Abusing Cortex XDR Live Terminal as a C2 - interesting post by #InfoGuardLabs. 😎
Turns out they could abuse the agent to send its reverse shell ("Live Terminal" feature) traffic to to an attacker server of their choosing (a Cortex XDR server tenant of their own, in this case).
Sam King retweeted
How are apps still doing this? Companies: stop asking users to upload their address books. And everyone else: refuse to upload your address book to random apps and social media platforms.
The contacts in your phone are not your data. It’s other people’s data.

Sam King retweeted

Last quarter I rolled out Microsoft Copilot to 4,000 employees.
$30 per seat per month.
$1.4 million annually.
I called it "digital transformation."
The board loved that phrase.
They approved it in eleven minutes.
No one asked what it would actually do.
Including me.
I told everyone it would "10x productivity."
That's not a real number.
But it sounds like one.
HR asked how we'd measure the 10x.
I said we'd "leverage analytics dashboards."
They stopped asking.
Three months later I checked the usage reports.
47 people had opened it.
12 had used it more than once.
One of them was me.
I used it to summarize an email I could have read in 30 seconds.
It took 45 seconds.
Plus the time it took to fix the hallucinations.
But I called it a "pilot success."
Success means the pilot didn't visibly fail.
The CFO asked about ROI.
I showed him a graph.
The graph went up and to the right.
It measured "AI enablement."
I made that metric up.
He nodded approvingly.
We're "AI-enabled" now.
I don't know what that means.
But it's in our investor deck.
A senior developer asked why we didn't use Claude or ChatGPT.
I said we needed "enterprise-grade security."
He asked what that meant.
I said "compliance."
He asked which compliance.
I said "all of them."
He looked skeptical.
I scheduled him for a "career development conversation."
He stopped asking questions.
Microsoft sent a case study team.
They wanted to feature us as a success story.
I told them we "saved 40,000 hours."
I calculated that number by multiplying employees by a number I made up.
They didn't verify it.
They never do.
Now we're on Microsoft's website.
"Global enterprise achieves 40,000 hours of productivity gains with Copilot."
The CEO shared it on LinkedIn.
He got 3,000 likes.
He's never used Copilot.
None of the executives have.
We have an exemption.
"Strategic focus requires minimal digital distraction."
I wrote that policy.
The licenses renew next month.
I'm requesting an expansion.
5,000 more seats.
We haven't used the first 4,000.
But this time we'll "drive adoption."
Adoption means mandatory training.
Training means a 45-minute webinar no one watches.
But completion will be tracked.
Completion is a metric.
Metrics go in dashboards.
Dashboards go in board presentations.
Board presentations get me promoted.
I'll be SVP by Q3.
I still don't know what Copilot does.
But I know what it's for.
It's for showing we're "investing in AI."
Investment means spending.
Spending means commitment.
Commitment means we're serious about the future.
The future is whatever I say it is.
As long as the graph goes up and to the right.

The "Rogue Gnome" proved to be quite the challenge! Took me ~7 hours to figure out; much harder than 2 snowflakes. 😵💫
But that sweet feeling when you finally find the flag... 🤩
Plus, I learned a thing or two about Json Web Tokens and jwks. 🤓
#HolidayHack #ctf @SANSInstitute
One red herring that threw me off, was the fact that I managed to send a request and get a "Werkzeug Debugger" page, which included a "secret" key parameter; and I thought perhaps I needed to use it to get to the flag.
I did not.
Wondering if this was intentional, @edskoudis ?
Sam King retweeted

Hey there friends! Have you played #HolidayHack yet at sans.org/holidayhack? It’s up and running, and we’d love for you to check it out. It’s the fun, FREE SANS cyber range where you’ll learn all kinds of useful skills: pen testing, post-quantum crypto, forensics, & more!

Ever got 0 results in a Yara scan, but wondered if the scan ran correctly? Wouldn't it be good to find 1 result that shows that the rule is syntactically valid and the scanning tool works?
Meet "Guilty-As-Yara": an EICAR for Yara!
github.com/Sam0rai/guilty-as…
#DFIR #Yara #BlueTeam

Cool new tool by @TwoSevenOneT !
Rushed to try it in my own org. To my happy dismay - the EDR caught its behavior and terminated the operation of running WerFaultSecure (when I tried to freeze the EDR or the AV).
As part of the #Blueteam- you must learn the #Redteam tactics. ☺️

Detailed analysis of the techniques used in the EDR-Freeze tool and how the #securityvulnerability of Windows Error Reporting is exploited to halt the operation of #antimalware
#cybersecurity
zerosalarium.com/2025/09/EDR…

Sam King retweeted

Last week, I focused on Active Directory Admins (ADAs).
teapawt.org/PyroTek3/status/195818…
This week, let's look at built-in privileged groups:
* Account Operators - should be empty per Microsoft due to highly privileged access in AD.
* Backup operators - should only contain backup service accounts to backup and restore Active Directory.
* Cert Publishers - should only contain PKI related accounts (CAs & related service accounts) since it can publish certificates for AD users.
* DNSAdmins - typically only used when admins other than ADAs perform DNS administration. Use sparingly.
* Enterprise Key Admins - have admin rights on key objects in AD.
* Event Log Readers - should only include accounts that require access to Domain Controller event logs.
* Group Policy Creator Owners - can modify Group Policies in the domain. Membership should be empty and rights delegated instead.
* Print Operators - used only when a Domain Controller is used as a print server (which shouldn't happen). Group has the ability to logon to Domain Controllers and install drivers which makes this group highly privileged. Group should be empty.
* Server Operators - effectively local admin on Domain Controllers. Use sparingly.
* Schema Admins - should be empty except when updating the AD schema.
learn.microsoft.com/en-us/wi…
Script leveraging the Active Directory PowerShell module:
github.com/PyroTek3/Misc/blo…
#ActiveDirectorySecurityTip


A critical part of Active Directory security is regularly reviewing your AD admins. The simplest way to do this is to recursively enumerate the membership of the domain Administrators group (that group's members and all member group members). PowerShell code shown below.
Check the AD Admins output for the following:
* Are all the admin accounts associated with people expected?
* Are there service accounts that shouldn't require AD admin rights (VMware, Exchange, LDAP, VPN, Sharepoint, etc.)?
* Are the associated passwords current? Are they as expected with no outliers (all within 2 years but one has a password that's 10 years old)?
* Has the default domain Administrator account logged on recently? Is that expected/known?
* Are all accounts enabled? Disabled accounts should be removed from being an AD Admin.
* Do all accounts require Kerberos preauthentication? They must if they are AD admins.
* Do any use Kerberos DES? If so fix that.
* Are any set to never expire their password? Is that expected? Accounts with this set rarely change their password.
* Are there any passwords in Active Directory user attributes (commonly description notes/info, Exchange custom attributes, etc.)? Practically all of the attributes are visible to users.
PowerShell code (using AD PS modules):
[array]$ADAdminArray = Get-ADGroupMember -Identity 'Administrators' -Recursive
$ADAdminPropertyArray = @()
ForEach($ADAdminArrayItem in $ADAdminArray)
{ [array]$ADAdminPropertyArray += Get-ADUser $ADAdminArrayItem.DistinguishedName -Prop * }
$ADAdminPropertyArray | Sort SamAccountName | Select SamAccountName,PasswordLastSet,LastLogonDate,Enabled,DoesNotRequirePreAuth,UseDESKeyOnly,PasswordNeverExpires | Format-Table -AutoSize
#ActiveDirectorySecurityTip

I was today years old, when I realized that in the song "Morning After Dark" by Timbaland, he in fact is NOT singing in German in the beginning:
"Auf Wiedersehen when it all goes up
Auf Wiedersehen when it all goes down".
#Timbaland #NellyFurtado #rap
youtu.be/25LBTSUEU0A?si=N-YE…
Watching season 4 of #KillingEve. One of my favorite recurring scenes is ANY scene where @KimBodniaDK laughes! The only laugh that express both "I am so amused by what you've just said" AND "OH, f*€k my life!", at the same time. 😁
#Villanelle