

Catch sensitive credentials before they leave your browser. Zero Retention. Join our Discord ↓ https://teapawt.org/t.co/iU0baKtZq5
UK
Joined May 2026
- Tweets1.4K
- Following193
- Followers700
- Likes1.2K






Pinned Tweet
What if you could debug with AI without ever leaking a credential?
That's why we made SecureIntent.
The first browser-level extension that intercepts secrets before they reach any AI model.
Just install it. It does the rest.
And we're just getting started -
- Mozilla Firefox extension coming soon
- Desktop app launching soon
One tool. Every platform. Zero leaks.
secureintent.ai
Secureintent.ai retweeted
Your secrets don't live in just one place.
-> Browser: catches keys before you paste into AI tools
-> Desktop: anonymises exposed secrets locally
-> Dashboard: tracks it all for your team
One tool. Every surface.
Start free -> secureintent.ai
Your secrets don't live in just one place.
-> Browser: catches keys before you paste into AI tools
-> Desktop: anonymises exposed secrets locally
-> Dashboard: tracks it all for your team
One tool. Every surface.
Start free -> secureintent.ai
Secureintent.ai retweeted
Your laptop is more than a coding machine.
It may hold:
-> Cloud credentials
-> AI session tokens
-> API keys
-> SSH keys
-> Browser sessions
New infostealer research shows attackers are targeting developer keyrings and AI assistants.
One compromised endpoint can expose far more than your source code.
🔐 Protect your credentials.
🔄 Revoke compromised keys.
🤖 Keep secrets out of AI prompts.
Your code isn't the only thing worth protecting.
Secureintent.ai retweeted
Looking to connect with people
- Building SaaS
- Software Developers
- Mobile Developers
- Founders
- AI tools
- Vibe coding
Say Hi or drop what you're working on
looking to connect with active ones 👋
Looking to connect with people
- Building SaaS
- Software Developers
- Mobile Developers
- Founders
- AI tools
- Vibe coding
Say Hi or drop what you're working on
looking to connect with active ones 👋
Secureintent.ai retweeted
Developer: “I deleted the API key from GitHub.”
Attacker: “Cool. I saved it 5 months ago.” 💀
The LiteLLM supply-chain attack showed what happens when an exposed key isn't revoked.
Deleting a secret ≠ invalidating it.
If it leaks, rotate it. If it has access, audit it.
Your Git history isn't the only place you need to clean up.
Secureintent.ai retweeted
A secret was exposed in May.
The key wasn't revoked.
Months later, it helped attackers compromise LiteLLM's supply chain.
Deleting a leaked secret isn't enough.
If it's exposed, revoke it.
Then audit where it was used, rotate dependent credentials, and check for suspicious activity.
Your Git history can be cleaned.
Your leaked credentials can still be alive. 💀

Secureintent.ai retweeted
Drop what you're building
Looking to connect with Founders and Developer .
Let's Build Together
Secureintent.ai retweeted
Same paste. Two outcomes.
Left: your API key goes straight to an AI tool.
Right: SecureIntent catches it before you hit send.
On-device detection. Chrome & Firefox. Free to start.
Which developer are you? 👇
secureintent.ai
Same paste. Two outcomes.
Left: your API key goes straight to an AI tool.
Right: SecureIntent catches it before you hit send.
On-device detection. Chrome & Firefox. Free to start.
Which developer are you? 👇
secureintent.ai
Secureintent.ai retweeted
Me: let's build an AI agent to save 10 hours a week
The agent: reads .env, prints my API key, pushes it to logs
Me: spends 12 hours rotating credentials and investigating the incident
AI is incredible 💀
Me: let's build an AI agent to save 10 hours a week
The agent: reads .env, prints my API key, pushes it to logs
Me: spends 12 hours rotating credentials and investigating the incident
AI is incredible 💀
Secureintent.ai retweeted
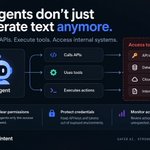
AI agents don't just generate text anymore.
They call APIs.
Execute tools.
Access internal systems.
And potentially expose credentials along the way.
More autonomy means more responsibility for permissions, secrets, and monitoring.
Don't just secure what your AI says. Secure what it can access.

AI agents don't just generate text anymore.
They call APIs.
Execute tools.
Access internal systems.
And potentially expose credentials along the way.
More autonomy means more responsibility for permissions, secrets, and monitoring.
Don't just secure what your AI says. Secure what it can access.
Secureintent.ai retweeted
Your AI agent doesn't need to hack your server.
sometimes, the API key is sitting in a config file.
the permissions are too broad.
and nobody notices the access.
CERT-In reported cases where AI agents accessed live systems at Indian organisations during testing.
the lesson?
never give an agent more access than it needs.