
https://teapawt.org/t.co/F8gC7CgLWB
Joined May 2024
- Tweets572
- Following195
- Followers1.5K
- Likes92


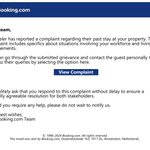


An interesting challenge that trips up analysts is determining whether something is a phish, or a pentest/phish test. Today we give you applic[.]center and webinfo[.]company. A good day to hone your intuition using osint and knowledge of how folks set up infra.
1860ac0e7f841425dd64d98569143116f017523e7aabc1b7d7e8b74be1d8fede

MoD_09-01-2025.chm #apt
e85d1e95fa10fcddd7c1e4a095c41744b5aa3952e31c77b8a6c29b8384426e58
-> d259aaa5d49dc2bd00baf4418343d8665afa7a87ed3a4d06736271d4f3b38d90
->
158.255.215[.]45:8899/nina/anotherLife

DPRK puts out one of the cleanest malicious bash scripts youll ever see. readability+++
7a45e4614662081bf300c897b5e4de212e41bf8ed53762a5e4d455eaee983a6a

Interesting phish against a Bangladesh bank from a compromised BD GOV sender. RAR -> LNK, cluster leads to targeted activity against Bangladesh, Pakistan, and China
Decoy content looks like OCR/image translate.
c2 vrms.bangladeshbaank-gov-bd.workers[.]dev
136dd864f5772a6567aff34fcbe6f0665b7cc04b2d486004c370f410bee259b1
github.com/StrikeReady-Inc/s…


one more, susp targeting "Bangladesh Telecommunication Regulatory Commission"
CyberNet2025.lnk
wandering-pond-e7f4.foxiproxi.workers[.]dev
eebf4a5104d75f8f6536e592d4c7945d56f8431059f2cab980756d9b9e96f0fc
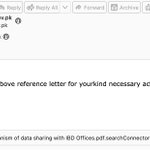
#dailyphish it's 10pm, do you know how your gateway handles ".searchConnector-ms" extensions?
"Mechanism of data sharing with IBD Offices.pdf.searchConnector-ms" -> ebbausersupport[.]com
b6e77578cb4aeaedabc0fa3a465a50a0b18e4c8b9bcffc9d2e24752eab02a1da


It's kind of strange how long theyve been able to use this api.camera-drive[.]org for hosting these mac and windows payloads --- going on a month+ but at a very high volume for a targeted attacker. @namecheap able to take camera-drive[.]org down?


NDC65-Updated-Schedule. zip
97e9fc3d3bbbcbdea3b3ea57953db9aad5e6f4f9d7f9d71e9309989ce26a8563
same lnk name (desktop-ey8nc5b)
Just hit VT, but looks like perhaps from 2023 based on timestamps and lack of c2 responsiveness
-> modspaceinterior[.]com/wp-content/upgrade/01/

#SideCopy
JS Army (Strat) .zip
87c0e81c2f0495b2174fdc8a12d9be3d
Army_Strat .lnk --> desktop-ey8nc5b
7460b5ba1628e9be5afe773a247ecb61
01048 .hta --> inniaromas[.]com
c07f421d3a3ba5e78f55c234ccaaa908
Same C2, decoy, FetaRAT and ActionRAT

One of our favorite dprk hunts is to watch for content containing oft-targeted institutions in content, be it spears or c2 artifacts. Although they aren't the original APT, they do put the "P" in APT
97bc3dd9fc2cb82d31377a716eea60b64635fff1e65bf6f30832a2a2d65729f8

People laugh about attribution some times, but in the careers of people in labs here, exactly zero times has this tool ever been used by anyone who wasnt connected to CN sponsored espionage (including moonlighting), with a rare exception of a joker on VT. zero crimeware uses.

#dailyphish #crimeware
5b964166035f3a8509b8e78c49a9c53dadbd788624899dfa9b7709c198f88852 -> fixecondfirbook[.]info


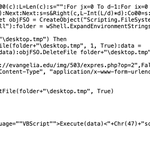
running powershell via "ssh.exe -o proxycommand" ... is that stealthy? seems to me it would be the opposite of stealthy ...
SBB_Fahrplan_5274147.pdf.lnk
db791160ec45c955a79be8361055c256e5fc6c3850fa1fa2298205f2ff0cf1f0

20250114_27263.docx.lnk (desktop-0jpcpit) -> www.dropbox[.]com/scl/fi/lpgj7eek9jczsx2ey83tk/zzG.zip?rlkey=lngmcnnjatzijm02oex219ffy&e=1&st=lwe8
f4c4f68f8b27279b00b718b02392d5dfe1766c342a189a51e0e2a6f6412e1ce0

found first: teapawt.org/JangPr0/status/1879054…

#APT
f4c4f68f8b27279b00b718b02392d5dfe1766c342a189a51e0e2a6f6412e1ce0
74.50.94[.]175:9992
74.50.94[.]175:7032
hxxps://www.dropbox[.]com/scl/fi/lpgj7eek9jczsx2ey83tk/zzG[.]zip


Back from vacation it appears; campaigns starting back up after a brief respite
2f8e8b2783c8c47da0f265199671f3cae4e31b2a03999fff12aa3090c74c7a51
linkcuts[.]com/5xu034g2 -> doads[.]org -> mocky ->
jkbfgkjdffghh.linkpc[.]net


same filename today (오류발견 수정신고 제출 요청 안내(국세징수법 시행규칙).hwp.lnk) but different payload --- and only 1MB this time
a1b67cfb080f4d1e4cbb0019a30259cb291f56c0ada02e2ca1028f675b187727
raleighice[.]com/wp-includes/js/inc/get.php
fantasiasognorealta[.]com/wp-includes/js/src/list.php
Another one of these hit VT, same chain, uploaded from Indonesia
Kelengkapan Dokumen Marlina Novriana.pdf.lnk
07bfae70b30398d86b306f2c29ddfc335e6276239909468a7e10993131370f09
This quoted post is unavailable.
4
932
