

Privacy Researcher. Check out my Articles 🥺. DM For Collabs & Partnerships. Founder @PhishCore - Human risk intelligence & Phishing simulation platform.
Navigating Digital Labyrinth
Joined November 2022
- Tweets7K
- Following515
- Followers48.2K
- Likes20.4K




getty images spent years watermarking every photo on the internet.
sued stability AI for training on their library. demanded the AI companies pay up. called it theft.
filed for chapter 11 bankruptcy this week.
the AI companies didn't pay. they just... kept going and designers stopped buying stock photos. and the $500 licensing fees stopped making sense when midjourney exists. and the debt piled up.
a company whose entire business model was "we own the visual record of human history, pay us" just got outrun by a model that learned from that record and started giving it away for free.
The irony is that the watermark is still on every image in the archive.
even the ones nobody's licensing anymore.

When post-quantum breaks RSA.
Banks freezing transactions because they can't verify anything. Certificate authorities gone dark. Every HTTPS padlock meaningless, governments pulling sites offline.
VPN useless, Your 2FA app secret is exposed. Every password manager vault encrypted before that day becomes an open file.
IT teams will get alerts at 3am with an incident they cannot close.
And somewhere in a signals intelligence archive, a decade of harvested ciphertext quietly becomes readable.
the PHP situation gave us the preview, two vulns, CVSS 9.2, governments took entire websites offline just to stay safe and update.
When there is no patch watch what happens.

A welsh broadband company left a test account called Test2 sitting live since 2012.
password: Password1
14 years later, ransomware walks in, takes 42GB of children’s data dating back to 2012, encrypts 182GB, and leaves.
the ICO issued a reprimand.
No fine. A letter.

Crowdstrike confirmed this week that a threat group used claude, grok, and deepseek to automate attacks on over 400 banks and financial institutions across latin america. reported first by the information.
AI agents handled reconnaissance, credential theft, and account access with little human involvement. one of the first documented cases at this scale.
how they got around the safety guardrails:
told the models they were running internal security tests. claude refused certain tasks anyway, they switched to kimi. kimi also refused, they fell back to traditional malware. the models were components in a pipeline, when one stopped cooperating, they used another.
This is the architecture now. Orchestrated multi-model workflows where each model handles the task it won't refuse.
Will defenders be able to keep up ?
php powers 43% of the web.
two critical RCE flaws CVSS 9.2 leaked before the patch was ready.
both confirmed real and working exploits are circulating attacks already started.
The dutch parliament went offline. the dutch national cybersecurity agency went offline. finland’s central government went offline. the university of vienna offline. every wiki on miraheze. explain xkcd. fur affinity.
They chose to go dark rather than stay online and get hacked.
the patch dropped at 14:00 UTC today.
php 8.1 and older no official patch. ever.
The PHP foundation developer who knows exactly what the bug does said: “I sadly know too much.”
so do we now.


php2shell — patch now.
two critical RCE flaws in PHP are confirmed real and being actively exploited. the fix is out.
update to:
8.5.12 · 8.4.27 · 8.3.36 · 8.2.35
on 8.1 or older: no official patch. PHP published source backports for 7.4, 8.0 and 8.1. check your distro for vendor backports. if you can’t patch, turn the server off until you can.
stopgaps if you can’t patch immediately:
— disable session.upload_progress.enabled in php.ini (breaks upload progress bars, nothing else)
— block multipart/form-data at the web server level (breaks file uploads entirely)
— Cloudflare has WAF rules live for all plans including free
PHP says: “there are no complete mitigations. updating is the only safe choice.”
Apache with mod_php is most at risk exploit fires before application code runs.
track it: cvemon.intruder.io
php powers 43% of the web.
two critical RCE flaws CVSS 9.2 leaked before the patch was ready.
both confirmed real and working exploits are circulating attacks already started.
The dutch parliament went offline. the dutch national cybersecurity agency went offline. finland’s central government went offline. the university of vienna offline. every wiki on miraheze. explain xkcd. fur affinity.
They chose to go dark rather than stay online and get hacked.
the patch dropped at 14:00 UTC today.
php 8.1 and older no official patch. ever.
The PHP foundation developer who knows exactly what the bug does said: “I sadly know too much.”
so do we now.
IT Guy retweeted
Whatsapp hid instructions inside its help pages telling its support chatbot not to mention privacy regulators.
if you couldn’t delete your account, don’t tell them about the data protection authority.
if you mentioned a lawyer, don’t cite GDPR. even if the user brought it up first.
102 hidden instruction blocks across 80 pages in the HTML where users couldn’t see them.
Visible to anyone who clicked the view source.
Whatsapp’s own european privacy policy tells users they can complain to the irish data protection commission.
the chatbot was told not to.
whatsapp says it was a bug.
the bug lasted from at least september 4th to october 18th.
A very specific bug that only affected instructions about regulators and lawyers.
OK 😂👍


IT Guy retweeted

Privacy and security go hand in hand.
Prynoid tests whether products keep their privacy promises. @PhishCore tests the human side of security.
Together, we’re helping organizations test what happens beyond the policies and promises.

PhishCore is partnering with @Prynoid, and the idea behind this partnership is simple: don’t just trust what the policy says. Test what actually happens.
At PhishCore, we test how people respond when a phishing email lands in their inbox.
At Prynoid, they test whether products handle people’s data the way they claim to.
Different sides of the same problem.
A security policy can say employees know how to spot phishing. A privacy policy can promise that people’s data is handled responsibly. But having a policy is one thing. Knowing what happens in practice is another.
That’s why we’re starting with Prynoid putting PhishCore to the test.
We work with behavioural data from phishing simulations, and we believe our own privacy claims should be held to the same standard as everyone else’s. If we ask organizations to take security and privacy seriously, we have to be willing to prove that we do too.
From there, we’ll explore a joint people-and-product assessment for organizations that handle sensitive information.
Because protecting an organization isn’t just about the people or the technology. It’s about both.
People and products. Tested, not assumed.

citizen lab confirmed this week that pegasus spyware infected the iphone of vladan đokić, rector of the university of belgrade who publicly backed the student protest movement.
zero-click attack. iMessage exploit. apple patched it in iOS 18.4.1. by the time it’s patched, it’s already been used.
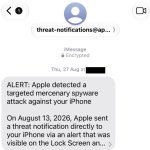
separately, apple sent a threat notification to prosecutor rade bajić — who was investigating corruption in serbia’s kushner-linked hotel project. threat notification means apple detected likely state-sponsored spyware activity. bajić is not confirmed infected. the notification is the signal.
At least 14 people targeted since early 2026. student activists, civil society, an opposition MP, a local councilor. twelve of them contacted SHARE in august after getting apple alerts.
serbia also has domestic spyware. NoviSpy a locally developed android tool was found on devices of activists who had their phones seized during police questioning. pegasus for the iphones. NoviSpy installed while in custody for the androids.
the timing: local elections were march 2026. parliamentary elections are this october.
If you’re in serbia and at elevated risk enable lockdown mode. keep iOS updated.
Contact SHARE Foundation or Access Now’s Digital Security Helpline if you’ve received an apple threat notification.

IT Guy retweeted

PhishCore is partnering with @Prynoid, and the idea behind this partnership is simple: don’t just trust what the policy says. Test what actually happens.
At PhishCore, we test how people respond when a phishing email lands in their inbox.
At Prynoid, they test whether products handle people’s data the way they claim to.
Different sides of the same problem.
A security policy can say employees know how to spot phishing. A privacy policy can promise that people’s data is handled responsibly. But having a policy is one thing. Knowing what happens in practice is another.
That’s why we’re starting with Prynoid putting PhishCore to the test.
We work with behavioural data from phishing simulations, and we believe our own privacy claims should be held to the same standard as everyone else’s. If we ask organizations to take security and privacy seriously, we have to be willing to prove that we do too.
From there, we’ll explore a joint people-and-product assessment for organizations that handle sensitive information.
Because protecting an organization isn’t just about the people or the technology. It’s about both.
People and products. Tested, not assumed.
Whatsapp hid instructions inside its help pages telling its support chatbot not to mention privacy regulators.
if you couldn’t delete your account, don’t tell them about the data protection authority.
if you mentioned a lawyer, don’t cite GDPR. even if the user brought it up first.
102 hidden instruction blocks across 80 pages in the HTML where users couldn’t see them.
Visible to anyone who clicked the view source.
Whatsapp’s own european privacy policy tells users they can complain to the irish data protection commission.
the chatbot was told not to.
whatsapp says it was a bug.
the bug lasted from at least september 4th to october 18th.
A very specific bug that only affected instructions about regulators and lawyers.
OK 😂👍
A security product can look excellent in a demo and still be a nightmare to deploy.
the people who installed it know where it breaks. the people who renew it know if it was worth the money.
qualitate makes those conversations part of the research. ask the people running it.
🤝 Paid partnership

We just raised $25M from Insight Partners to replace Gartner, McKinsey, and GLG.
RIP the Quadrant, the 80-page consulting deck, and the $2000 expert network call.
Our revenue run-rate is up 10x+ this year.
100+ investment firms and enterprises use Qualitate to inform decisions with firsthand evidence.
Here's how:
qualitate.io/book-a-demo
A casino got hacked through a fish tank.
It has sensors. automated feeding, temperature control, remote monitoring.
connected to the internet. isolated on its own VPN. segregated from everything else.
Hackers still found it anyway, compromised it, pivoted to the main network.
started pulling data.
nobody monitors fish tank outbound traffic, why would they it's a fish tank.
Darktrace caught it, anomalous transfers to an external destination nobody in the building had ever talked to.
the casino had done everything right. separate network. isolated device. proper segmentation.
Still didn't matter.
The fish tank was still online, still running software, still had an attack surface.
Every device you connect is a door you didn't know you opened.
"How did it happen even after the network isolation?"
good question. Two ways this works:
One, the isolation failed. The fish tank was supposed to be on a separate network. attackers found a misconfiguration or a bridge between the two. Shi happens.
Two, lateral movement. once you’re inside any device on a network, you start looking for paths outward. a misconfigured router, a shared service, a default credential on something else. the tank was the entry point.
darktrace only confirmed the breach, they didn’t publish the full pivot path. we don’t know exactly how the segmentation failed, that detail was never released publicly.
A casino got hacked through a fish tank.
It has sensors. automated feeding, temperature control, remote monitoring.
connected to the internet. isolated on its own VPN. segregated from everything else.
Hackers still found it anyway, compromised it, pivoted to the main network.
started pulling data.
nobody monitors fish tank outbound traffic, why would they it's a fish tank.
Darktrace caught it, anomalous transfers to an external destination nobody in the building had ever talked to.
the casino had done everything right. separate network. isolated device. proper segmentation.
Still didn't matter.
The fish tank was still online, still running software, still had an attack surface.
Every device you connect is a door you didn't know you opened.
A savannah police officer gave her ICE agent husband her Flock login.
he ran 983 searches. 97 license plates. six states.
788 of them were in south carolina alone.
investigators found that most of the registered owners of those vehicles were hispanic.
her husband's explanation: "every name i ever ran was an ICE target."
she was fired. he was not charged. she was not charged.
the only thing that stopped it was an internal audit of flock misuse that happened to catch her account.
flock has cameras in your city. savannah PD shares data with 1,700+ agencies.
ICE is not on that list.
was.
A Florida woman was arrested for what she typed into Claude.
Carli Michelle Heller, 30, of Bonita Springs, wrote on September 26 that she was going to "shoot up" the Lee County Sheriff's Office, the next day she wrote that she'd gotten a new gun. she said she was angry because deputies had been present when her child was removed from her custody.
she also said she uses Claude as a diary.
Claude's safety systems flagged the entries, escalated to a human reviewer, reviewer decided it was credible, reported to law enforcement without a warrant deputies identified her and arrested her at home on September 30.
Anthropic's updated policy from September 10, 2026 explicitly permits sharing data with police when Anthropic has a good-faith belief that disclosure is reasonably necessary to prevent serious harm.
the same policy: flagged conversations can be used to improve the safety detection systems. A flagged diary entry becomes training data for the detectors.
Wvery Claude user should know the terms permit this, they have monitoring and the reporting channel exists.
you are not writing in a diary.
you are writing to a company that has reserved the right to call the police.