

Come learn to hack at TCM Security Academy! Affordable Learning with Quality results. Need support? Email [email protected]!
United States
Joined February 2019
- Tweets7.9K
- Following422
- Followers219K
- Likes29.2K




Pinned Tweet
Stuck deciding between which #cybersecurity path to go - offensive or defensive?
The reality? Blue team roles are often more abundant at the moment, but following your passion is critical.
Andrew Bellini recommends taking a course in both areas to see which excites you more, and from there, building your personal career roadmap.
Which path are you on? Tell us in the comments, and don't forget to check out our certification roster which features both blue and red team certifications. hubs.la/Q04B-kR90
Find the full guide here: tcm.rocks/soc-resources


Want to sharpen your SOC analyst skills? We've put together a few resources worth bookmarking. 🔵
One of the best ways to improve your #blueteam skills is to get hands-on experience investigating suspicious activity, analyzing evidence, and learning to recognize what an actual security incident looks like.
Fortunately, there are plenty of resources out there to help you practice.
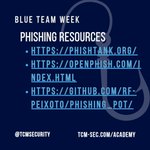
In this carousel, we're highlighting some of our picks for:
🔹 𝗣𝗵𝗶𝘀𝗵𝗶𝗻𝗴 𝗮𝗻𝗮𝗹𝘆𝘀𝗶𝘀: Resources for investigating suspicious URLs and phishing campaigns.
🔹 𝗠𝗮𝗹𝘄𝗮𝗿𝗲 𝗮𝗻𝗮𝗹𝘆𝘀𝗶𝘀: Sites and sample collections to help you better understand malicious activity.
🔹 𝗗𝗶𝗴𝗶𝘁𝗮𝗹 𝗙𝗼𝗿𝗲𝗻𝘀𝗶𝗰𝘀 & 𝗜𝗻𝗰𝗶𝗱𝗲𝗻𝘁 𝗥𝗲𝘀𝗽𝗼𝗻𝘀𝗲 (𝗗𝗙𝗜𝗥): Resources for studying real-world attack techniques and investigations.
Whether you're working toward your first SOC role or looking to build on your existing experience, there's something here worth exploring.
Save this post for your next study session or share it with someone who's building their blue team skills!
P.S. these resources should be 𝗲𝘀𝗽𝗲𝗰𝗶𝗮𝗹𝗹𝘆 helpful if you're taking SOC 201 or eventually plan to take the PSAP (Practical SOC Analyst Professional) cert. hubs.la/Q04C5bxR0
TCM Security retweeted

We’re probably all dealing with php2shell today in some capacity.
You might find yourself being able to read the vulnerability, but what about fixing it? Our new challenge lets you find out without production on the line.
Check out “PHP2Shell” on bit.ly/4dO3LV5.

Meet the TCM Security Blue Team courses! Here's a quick rundown of everything we offer to boost your defensive security skills:
𝗣𝗿𝗮𝗰𝘁𝗶𝗰𝗮𝗹 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗙𝘂𝗻𝗱𝗮𝗺𝗲𝗻𝘁𝗮𝗹𝘀: This FREE course helps you build the foundation to start your journey.
𝗦𝗢𝗖 𝟭𝟬𝟭: Learn the foundations for a T1 or T2 SOC Analyst role, including SIEM, digital forensics, and more.
𝐒𝐎𝐂 𝟐𝟎𝟏: Go beyond with this intermediate course that explores threat hunting and incident response.
𝗗𝗲𝘁𝗲𝗰𝘁𝗶𝗼𝗻 𝗘𝗻𝗴𝗶𝗻𝗲𝗲𝗿𝗶𝗻𝗴: Learn to create detections through offensive tests and solid documentation.
See the full breakdown in the slides, and get started with your #BlueTeam learning today! Memberships start at $29.99 a month. hubs.la/Q04B-0Y30


ICYMI...

🚨 PHP2Shell detection is now available in Burp Suite Professional & Burp Suite DAST.
Most of the web is powered by PHP, which means most of the web is vulnerable to these critical unauthenticated remote code execution flaws (CVE-2026-109618 / 109619). You can already detect it in Burp Suite using:
🟧 ActiveScan++ v2.0.13 (portswigger.net/bappstore/31…)
🟧 Bambda scan checks (github.com/PortSwigger/bambd…)
🟧 BChecks (github.com/PortSwigger/bchec…)
Start scanning for the vulnerability now → portswigger.net/bappstore/31…

If you attended our personal branding workshop today, you got some tips on how to better position yourself in the #cybersecurity community.
One major aspect of that is your LinkedIn profile. And if you want a quick primer on how to fine-tune your profile, we got you!
Whether you’re job hunting or growing your network, these simple tweaks can help you stand out for the right reasons.
🔹𝐃𝐢𝐚𝐥 𝐢𝐧 𝐲𝐨𝐮𝐫 𝐡𝐞𝐚𝐝𝐥𝐢𝐧𝐞 Your headline should reflect who you are and where you’re headed. Even if you’re between roles, focus on your expertise, interests, and aspirations. Extra context (like years of experience) can help, just keep it concise.
🔹 𝐃𝐨𝐧’𝐭 𝐬𝐤𝐢𝐩 𝐭𝐡𝐞 “𝐀𝐛𝐨𝐮𝐭” 𝐬𝐞𝐜𝐭𝐢𝐨𝐧 Think of this as your elevator pitch. Share a clear, honest snapshot of your professional journey and goals. Short and direct works best, but if you want more detail, place it below the “See more” cutoff.
🔹𝐔𝐬𝐞 𝐚 𝐩𝐫𝐨𝐟𝐞𝐬𝐬𝐢𝐨𝐧𝐚𝐥 𝐡𝐞𝐚𝐝𝐬𝐡𝐨𝐭 No studio photo? No problem. A clean, well-lit photo - or a polished Canva-style headshot - goes a long way in making a strong first impression.
🔹𝐊𝐞𝐞𝐩 𝐞𝐱𝐩𝐞𝐫𝐢𝐞𝐧𝐜𝐞 𝐮𝐩 𝐭𝐨 𝐝𝐚𝐭𝐞 Review your experience section for accuracy and impact. Make sure past roles don’t read like current ones and highlight the value you actually delivered, not just your responsibilities.
🔹 𝐀𝐬𝐤 𝐟𝐨𝐫 𝐫𝐞𝐜𝐨𝐦𝐦𝐞𝐧𝐝𝐚𝐭𝐢𝐨𝐧𝐬 & 𝐞𝐧𝐝𝐨𝐫𝐬𝐞𝐦𝐞𝐧𝐭𝐬 These add credibility and social proof. Stick to people you’ve worked with professionally; they’re best positioned to speak to your skills and work ethic.
🔹𝐅𝐢𝐥𝐥 𝐨𝐮𝐭 𝐫𝐞𝐥𝐞𝐯𝐚𝐧𝐭 𝐬𝐞𝐜𝐭𝐢𝐨𝐧𝐬 Volunteer work, certifications, publications, project ... if it adds value to your story, include it. This is your space to show the full picture.
🔹𝐉𝐨𝐢𝐧 𝐠𝐫𝐨𝐮𝐩𝐬 𝐚𝐧𝐝 𝐞𝐧𝐠𝐚𝐠𝐞 If networking is your goal, get involved. Join groups aligned with your interests and participate in conversations. LinkedIn works best when you do.
🔹𝐂𝐨𝐧𝐬𝐢𝐝𝐞𝐫 𝐩𝐨𝐬𝐭𝐢𝐧𝐠 (𝐰𝐡𝐞𝐧 𝐲𝐨𝐮’𝐫𝐞 𝐫𝐞𝐚𝐝𝐲) You don’t have to post daily, but sharing insights, reposting articles with your take, or engaging thoughtfully can help build visibility and attract the right attention.
Ready to level up your #LinkedIn profile? Start applying these tips today.
And if you’re looking to strengthen your profile with courses or certifications, check out the TCM Security Academy: hubs.la/Q04BZ5M90


TCM Security retweeted

🚨 PHP2Shell: CVE-2026-109618 & CVE-2026-109619🚨
Two critical PHP remote code execution bugs, affecting apps built on PHP like WordPress, Drupal, Magento, Laravel, and Joomla.
Discover every PHP server you run and see which ones are exploitable.
Run directly with Neo: go.projectdiscovery.io/php2s…

Don't miss today's resume and personal branding workshop - only in our #Discord server! Unlike our livestreams, this one starts at 1 PM ET.
We'll go over some resume best practices and talk about personal branding (portfolios, GitHubs, socials, so on.)
Bring your questions, and hopefully we can get you some answers!
Happy Cybersecurity Careers Week! hubs.la/Q04BQ5YZ0


TCM Security retweeted

Happy SOC Analyst Appreciation day to my fellow analysts and colleagues!
Happy SOC Analyst Appreciation Day! 💙
Today, we're recognizing some of cybersecurity's unsung heroes: the SOC analysts working behind the scenes to keep organizations safe.
From investigating suspicious activity and responding to incidents to sorting through countless alerts, SOC analysts are on the front lines of #cybersecurity defense every day.
It's demanding work that requires patience, persistence, technical expertise, and plenty of dedication. And while much of that work happens out of the spotlight, it doesn't go unnoticed.
To all the #SOC analysts out there: thank you for everything you do. Your work matters, and we appreciate you!
And for those interested in pursuing or advancing a SOC career, TCM Security offers two SOC-focused certifications, including the intermediate-level Practical SOC Analyst Professional (PSAP): hubs.la/Q04BCzbC0

Ever been curious about the world of GRC (governance, risk, and compliance?) 🤔
Our resident CISO Alex breaks down what a day in the life of a #GRC professional. He discusses how these professionals need to work across the organization to understand potential risk and develop solutions that can meet that risk head on.
Start your blue team journey in the TCM Security Academy; at the moment, we no longer have GRC courses, but we have plenty of adjacent training.
🔗hubs.la/Q04BC6ts0
Happy SOC Analyst Appreciation Day! 💙
Today, we're recognizing some of cybersecurity's unsung heroes: the SOC analysts working behind the scenes to keep organizations safe.
From investigating suspicious activity and responding to incidents to sorting through countless alerts, SOC analysts are on the front lines of #cybersecurity defense every day.
It's demanding work that requires patience, persistence, technical expertise, and plenty of dedication. And while much of that work happens out of the spotlight, it doesn't go unnoticed.
To all the #SOC analysts out there: thank you for everything you do. Your work matters, and we appreciate you!
And for those interested in pursuing or advancing a SOC career, TCM Security offers two SOC-focused certifications, including the intermediate-level Practical SOC Analyst Professional (PSAP): hubs.la/Q04BCzbC0
Have you tried our brand-new Windows Evidence Acquisition & Triage course?
The newest addition to the TCM Security Academy, this blue team course focuses on the investigative mindset, the digital forensic process, foundational principles, #DFIR software and hardware, and more.
If you've taken Intro to Windows Forensics, this is the natural next step. Read more about it here: hubs.ly/Q04BvzJW0


How can you become a SOC analyst following the TCM Security Academy courses and certifications?
Start with 𝘁𝗵𝗲 𝗳𝗿𝗲𝗲 𝗣𝗿𝗮𝗰𝘁𝗶𝗰𝗮𝗹 𝗛𝗲𝗹𝗽 𝗗𝗲𝘀𝗸 𝗰𝗼𝘂𝗿𝘀𝗲, get the PHDA (Practical Help Desk Associate), take our several Blue Team courses, and 𝘁𝗵𝗲𝗻 𝗮𝗶𝗺 𝗳𝗼𝗿 𝘁𝗵𝗲 𝗣𝗦𝗔𝗔 (𝗣𝗿𝗮𝗰𝘁𝗶𝗰𝗮𝗹 𝗦𝗢𝗖 𝗔𝗻𝗮𝗹𝘆𝘀𝘁 𝗔𝘀𝘀𝗼𝗰𝗶𝗮𝘁𝗲).
There's the next step as well - 𝘁𝗵𝗲 𝗣𝗦𝗔𝗣 (𝗣𝗿𝗮𝗰𝘁𝗶𝗰𝗮𝗹 𝗦𝗢𝗖 𝗔𝗻𝗮𝗹𝘆𝘀𝘁 𝗣𝗿𝗼𝗳𝗲𝘀𝘀𝗶𝗼𝗻𝗮𝗹), which builds off the material found in the SOC 201 course.
Want to really challenge yourself? Go even further with t𝗵𝗲 𝗣𝗿𝗮𝗰𝘁𝗶𝗰𝗮𝗹 𝗠𝗮𝗹𝘄𝗮𝗿𝗲 𝗥𝗲𝘀𝗲𝗮𝗿𝗰𝗵 𝗣𝗿𝗼𝗳𝗲𝘀𝘀𝗶𝗼𝗻𝗮𝗹 (𝗣𝗠𝗥𝗣), which will also give you a taste of purple teaming.
Stand out when applying for SOC roles. Explore this roadmap and start your journey.
Will you be following this roadmap yourself... or have you already started?
Start forging your own #BlueTeaming path today: hubs.la/Q04BsFNX0

This week is all about the #BlueTeam here at TCM Security. And what better way to start things off than sharing the FREE portion of our popular SOC 101 course on YouTube?
Watch it here: Security Operations (SOC) 101 Course - 10+ Hours of Content! (hubs.la/Q04BsrMG0)

From mechanical engineering student to IT Solutions Engineer at TCM Security. Meet Likith Chowdary! 👋
Likith joined TCM Security 𝗯𝗮𝗰𝗸 𝗶𝗻 𝟮𝟬𝟮𝟮, making him one of our earliest employees. But his path into cybersecurity wasn't exactly traditional.
While studying mechanical engineering in India, Likith developed an interest in computers. When the pandemic hit, that curiosity led him to purchase his first cybersecurity course. He eventually discovered our free Practical Ethical Hacking (PEH) training, which became a major turning point in his journey.
Today, Likith helps support our customers and team as an IT Solutions Engineer. He's particularly interested in red teaming, especially evading endpoint detection tools, and is currently expanding his knowledge of cloud technologies and AI.
A few fun facts about Likith:
1️⃣ He insists Cyberpunk 2077 is the best game out there
2️⃣ He's a proud Husky owner (Taro, pictured)
3️⃣ He's a Real Madrid supporter and follows CSK in the Indian Premier League
4️⃣ Outside of work, he loves gaming and traveling to new countries
When asked what he values most about working at TCMS, Likith highlighted the people, the opportunity to learn from others, and the importance of taking care of customers.
And his parting advice for the community? "Touch grass." 😂

Malware analysis is about more than just identifying a suspicious file. It's about understanding what that file does, how it behaves, and what evidence it leaves behind.
And having the right tools in your toolkit can make a difference. 🔨
We've combined 3 of our previous malware analysis resource collections into one master guide featuring 12 tools to help you investigate suspicious files, analyze malicious behavior, and develop your malware analysis skills.
𝐀 𝐟𝐞𝐰 𝐨𝐟 𝐭𝐡𝐞 𝐭𝐨𝐨𝐥𝐬 𝐲𝐨𝐮'𝐥𝐥 𝐟𝐢𝐧𝐝 𝐢𝐧𝐬𝐢𝐝𝐞:
🔴 𝐅𝐋𝐎𝐒𝐒: Extract and deobfuscate strings from malware binaries.
🟣 𝐏𝐫𝐨𝐜𝐦𝐨𝐧: Monitor file system, Registry, and process activity on Windows.
🔴 𝐂𝐀𝐏𝐄 𝐒𝐚𝐧𝐝𝐛𝐨𝐱: Execute suspicious files in an isolated environment to examine their behavior.
🟣 𝐘𝐀𝐑𝐀 / 𝐘𝐀𝐑𝐀-𝐗: Create detection rules based on patterns and characteristics identified during analysis.
Whether you're just getting started with #malware analysis or looking to expand your existing toolkit, we hope you find a few useful resources here!
What malware analysis tools do you regularly use? Share your favorites in the comments.
Want to take your malware analysis skills further? Check out our Practical Malware Analysis & Triage (PMAT) course and the corresponding Practical Malware Research Professional (PMRP) certification: hubs.la/Q04Bt5bY0
(We'll link the guide in the next tweet!)


See the rest here: tcm.rocks/malware-tools
