

Real Intrusions by Real Attackers, the Truth Behind the Intrusion
thedfirreport.com/contact
Joined April 2020
- Tweets1.9K
- Following0
- Followers70.7K
- Likes754


Pinned Tweet
New logo. New website. Same DFIR Report team. 🔎
Check out the incredible analysts behind the research:
thedfirreport.com/company/an…

👤 Analyst Spotlight: Jake Ouellette
8+ years in security spanning detection engineering, incident response, and compliance. Has experience leading security teams and enjoys solving challenges at scale. Has a soft spot for the small to midsize business and MSP world. Enjoys rock climbing and mountain biking.
Explore their work on The DFIR Report: buff.ly/maqs80B

"Despite the port number, this traffic was in fact SFTP traffic being used to transfer the data."
Read the full report: buff.ly/uLuiN9Z
#DFIR #ThreatIntel

🤖 100+ AI/ML training sets, built from years of real DFIR cases.
AI Training Ground gives you over 100 fully documented intrusions from The DFIR Report, system and network logs, memory, malware, and IOCs, capturing real threat-actor behavior end to end: initial access, lateral movement, credential theft, exfiltration, and impact.
The ground truth you need to train and validate your AI and ML security models.
Learn more 👉 buff.ly/ovcWaEr
🛠️ Tool Tuesday: AnyDesk
Legitimate remote-support software, and a common attacker backdoor. We repeatedly see AnyDesk silently installed as a service for persistent hands-on-keyboard access.
🔎 Hunt tip: alert on unattended AnyDesk installs, service creation, and connections from unfamiliar AnyDesk IDs.
See it across real intrusions 👉 buff.ly/NA1hVgK
"All of the newly created accounts have usernames that mimic legitimate accounts already present in the environment. For the rest of the report we will refer to these accounts as: 'administratr', 'Lookalike 1', and 'Lookalike 2'."
Read the full report: buff.ly/kJ1ukVK
#DFIR #ThreatIntel

🔒 Private DFIR Reports
Context-rich, ground-truth intrusion analysis from real investigations: unredacted command lines, evidence-based timelines with exact timestamps, and annotated forensic artifacts, process trees, registry keys, and command outputs.
Built for detection engineering, IR, red teaming, analyst training, and AI/ML security models.
Contact us 👉 buff.ly/AXx8KQQ
#DFIR #ThreatIntel
🚨 Early warning, from real adversary activity.
Active Defense monitors attacker interactions with your decoys around the clock and delivers customer-specific threat intelligence, so you detect and disrupt targeted activity before it reaches production.
Learn more 👉 buff.ly/GvI6WMo
Nice write-up from the @GreyNoiseIO team on the proxyjacking activity we've been seeing.
We recently shared our observations from a compromised Linux server running Pawns.app. Their research adds some great context around the broader activity.
Always great to see the community sharing information!
H/T @ImposeCost for sharing 👇
greynoise.io/blog/proxyjacki…


🧲 We recently saw a threat actor compromise an exposed Linux server and install Pawns.app, a legitimate "earn money from your bandwidth" agent, registered to their own account. The goal was to get paid while strangers route traffic through the victim's IP.
On the box, the threat actor:
🔹 dropped a JSP webshell and ran quick recon (id, uname -a, ip addr)
🔹 pulled the Pawns CLI with wget and hid copies as .p in /tmp, /var/tmp, /opt and /home
🔹 tried to persist with an @reboot cron entry
🔹 launched the agent with -email= -device-name= -accept-tos
Threat actors like proxyjacking for a few reasons:
🔹 The binary is the vendor's official app, so antivirus has nothing to catch
🔹 There's no CPU spike, just HTTPS to a well-known service
🔹 The abuse reports land on your IP, not theirs
IOCs:
Threat actor infrastructure (Pawns CLI pulled via wget):
144[.]172[.]86[.]173
209[.]99[.]190[.]80
Pawns account: skynox7@proton[.]me
Files: /tmp/.p, /var/tmp/.p, /opt/.p, /home/.p, /tmp/gotoschool
State file: /var/tmp/.config/pawns-cli/pawns-consent.log
To hunt for it, watch for web server processes spawning wget or curl, proxyware launch flags, and servers talking to services like Pawns, Honeygain, EarnApp or PacketStream.
Add proxyware to your hunt list next to miners and stealers.
🎉 Congratulations to the top 5 winners of our 2026 DFIR Labs Digital Forensics Challenge, all hitting 9050 points!
🥇 1st Place: @KoifSec
🥈 2nd Place: gunturyk11
🥉 3rd Place: @fs_alhumaid
🏅 4th Place: kapelo
🏅 5th Place: loadinGG
Players investigated Private Case #39390: ClickFix leads to Tsundere Bot, Tunnels, RMMs, and Double Theft, tracking a weeks-long intrusion featuring multiple RMMs, tunneling, a dropped VM, and double exfiltration.
Missed out or want another go?
Grab the Elastic/Splunk lab now 👉
🔬 DFIR Labs Subscribers: dfirlabs.thedfirreport.com/
🛒 Purchase Case #39390: store.thedfirreport.com/prod…
"EtherRAT used decentralized infrastructure for C2 resolution, querying Ethereum smart contracts through 1rpc[.]io to resolve its current C2 URL."
Read the full report: buff.ly/2MhA5Az
#DFIR #ThreatIntel

Just because an EXE is signed doesn't mean everything it loads is safe.
We came across an interesting infection chain where threat actors used legitimate, signed executables from SonicWall, IBM, Blue Iris, and ON1 to ultimately deploy SectopRAT (ArechClient2).
They took legitimate DLLs shipped with these applications, modified their import tables to reference a threat actor-controlled DLL, and let Windows do the rest.
When the signed application started, it loaded the modified vendor DLL, which then pulled in the malicious DLL.
The final payload, SectopRAT, ran in memory and retrieved its C2 configuration from a smart contract on the BNB Smart Chain.
We observed four different DLL sideloading chains:
🔹 SWGVC.exe → SWIsaCmn.dll → toolJ.dll
🔹 WinWrapIDE.exe → wwide9.dll → format.dll
🔹 BlueIris.exe → libfftw3-3.dll → ApiTag.dll
🔹 ON1Photoshop.exe → opencv_flann453.dll → modPro.dll
A few things worth hunting for:
🔎 Signed applications running from unusual locations, especially AppData\Local.
🔎 DLLs sitting alongside signed executables that return HashMismatch when checked with Get-AuthenticodeSignature.
🔎 Unexpected unsigned DLLs loaded by otherwise legitimate applications.
🔎 Vendor DLLs with unusual or newly added imports.
Some IOCs from the activity:
C2:
93[.]152[.]220[.]219:443
96[.]62[.]218[.]59:443
BNB Smart Chain contract:
0xb11613acf39ad3b4dde427c27068d278fafa8998
#DFIR #ThreatHunting #SectopRAT #BlueTeam
🧲 We recently saw a threat actor compromise an exposed Linux server and install Pawns.app, a legitimate "earn money from your bandwidth" agent, registered to their own account. The goal was to get paid while strangers route traffic through the victim's IP.
On the box, the threat actor:
🔹 dropped a JSP webshell and ran quick recon (id, uname -a, ip addr)
🔹 pulled the Pawns CLI with wget and hid copies as .p in /tmp, /var/tmp, /opt and /home
🔹 tried to persist with an @reboot cron entry
🔹 launched the agent with -email= -device-name= -accept-tos
Threat actors like proxyjacking for a few reasons:
🔹 The binary is the vendor's official app, so antivirus has nothing to catch
🔹 There's no CPU spike, just HTTPS to a well-known service
🔹 The abuse reports land on your IP, not theirs
IOCs:
Threat actor infrastructure (Pawns CLI pulled via wget):
144[.]172[.]86[.]173
209[.]99[.]190[.]80
Pawns account: skynox7@proton[.]me
Files: /tmp/.p, /var/tmp/.p, /opt/.p, /home/.p, /tmp/gotoschool
State file: /var/tmp/.config/pawns-cli/pawns-consent.log
To hunt for it, watch for web server processes spawning wget or curl, proxyware launch flags, and servers talking to services like Pawns, Honeygain, EarnApp or PacketStream.
Add proxyware to your hunt list next to miners and stealers.
⚡ Track attacker infrastructure, feed your detections.
The DFIR Report Threat Feed turns the command-and-control frameworks and clusters we track into blockable, high-fidelity indicators, updated as the infrastructure moves, not weeks later.
Get early warning 👉 buff.ly/g2RNnRd
While enumeration was ongoing, the actor returned to the backup server for more credential theft via COMSVCS. A new service was installed, then executed, spawning a process tree that dumped credentials to a file in the temp directory.
Request access or a demo 👉 buff.ly/AXx8KQQ
#DFIR #ThreatIntel
"Fortunately the threat actor had bad opsec and reused a password so we were able to decrypt the file using the “rclone config show” command"
Read the full report: buff.ly/t3MPa7p
#DFIR #ThreatIntel

🛡️ Prevent, detect, train your AI, and purple team, all from one subscription.
All Intel gives your team The DFIR Report's full non-public intelligence:
🔹 Threat Feed, high-fidelity indicators tied to real intrusions
🔹 Private DFIR Reports
🔹 Near real-time intrusion tracking
🔹 C2 configurations
🔹 Long-term infrastructure tracking
🔹 and more
How defenders put it to work:
🔹 Prevent: block emerging infrastructure before it reaches you
🔹 Detect: engineer detections from real exploit chains before public disclosure
🔹 Train AI: ground your models in real intrusion data
🔹 Purple team: exercise against current, real-world TTPs
Learn more 👉 buff.ly/IDE6zab

🛠️ Tool Tuesday: AdFind
A free AD query tool, and a recon staple in ransomware playbooks. We see AdFind, often via a batch wrapper, enumerate users, groups, computers, and trusts to plan lateral movement.
🔎 Hunt tip: flag adfind.exe with objectcategory queries and the classic recon batch scripts.
See it across real intrusions 👉 buff.ly/sDS3XpA
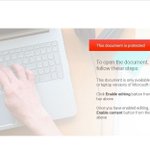
"This single-paged document contained a picture with instructions, attempting to lure the victim into enabling macros."
Read the full report: buff.ly/LCFCbkh
#DFIR #ThreatIntel

👤 Analyst Spotlight: Almedin Santic
Based in Norway, Almedin ('Dino') has worked in cybersecurity for 8 years, mainly in SOC, IR, and Detection Engineering, and enjoys forensic analysis and playing CTFs.
Explore their work on The DFIR Report: buff.ly/oyuI5Rb
