
Prev founded Percy, Respondly, & Favstar. Family guy who enjoys 🍦⛷ Ξ. Bug hunting for fun and profit. 👨🏼🍳
Wanaka, New Zealand
Joined April 2008
- Tweets69.7K
- Following989
- Followers5.4K
- Likes57.9K
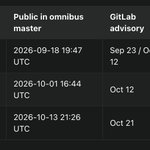






Dunno why @gitlab disclosed this without coordinating with the Ruby patches.

I recommend everyone upgrade Ruby immediately. This is a DoS and RCE vector if you accept user input into Regexp.new() ruby-lang.org/en/news/2026/1…
Tim Haines 🇺🇦 retweeted

I recommend everyone upgrade Ruby immediately. This is a DoS and RCE vector if you accept user input into Regexp.new() ruby-lang.org/en/news/2026/1…
Becoming adept at using a weeks worth of tokens in a day. Thanks @thsottiaux.

Tim Haines 🇺🇦 retweeted

Thanks a lot to @TimHaines for performing a security audit of Rack Gateway: github.com/DocSpring/rack-ga…
I've been working hard on this project and I've been trying to make it as secure as possible, but Tim was able to find a huge number of things that I had missed.

Interesting facets coming out of the PHP foundation's reports about Mythos and Daybreak Red not finding the bugs disclosed this week.

wait, PHP was actually scanned by Anthropic’s Claude Mythos earlier this year. they also had access to OpenAI’s Daybreak Red for validating exploits.
the PHP Foundation revealed this JUST yesterday.
keeping frontier cyber models in the hands of a selected few doesn’t seem to be working well for the internet.
thephp.foundation/blog/2026/…

.@kong has also just bumped it's @Hacker0x01 signal requirement from 1 to 3.
Hope this helps reduce the noise @sonicaghi. Would be interested to hear your teams experience with it over the coming month.

Interesting. @brave was paused for new report submissions on @Hacker0x01. They've unpaused, but have set a signal requirement of 7.0 (max value on H1) in order to submit. Seems like a much better way to manage volume. Your doing @bcrypt?
Other programs with custom signal levels:


Interesting. @brave was paused for new report submissions on @Hacker0x01. They've unpaused, but have set a signal requirement of 7.0 (max value on H1) in order to submit. Seems like a much better way to manage volume. Your doing @bcrypt?
Other programs with custom signal levels:
My wife’s pharmacy has taken their php app offline, so she can’t pre-order her medication. (Need to submit a photo of the script)
Time for @chainguard_dev to remove 'trusted' from their bio.


"On October 21st at 07:41 UTC, more than six hours before the coordinated release, Chainguard unilaterally broke the embargo and published built images containing the fix. Like other distributors, Chainguard had received the patch in advance so its users could update the moment the vulnerabilities were disclosed. Any attacker could now study the fix in binary form while every other PHP user was still waiting for the release. This disregarded weeks of work by many parties toward a coordinated disclosure."
thephp.foundation/blog/2026/…

Hope your vendors patched. 🔥

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Exciting week for cybersecurity. 🔥🔥🔥

Node.js Security Advisory: a high-severity RCE flaw in Node's Brotli decoder affects Node.js 22, 24, and 26.
Vercel WAF rules are live for every project and block known exploit patterns.
vercel.com/kb/bulletin/node-…

The “Leak and disrupted disclosure” section of this report is fascinating. Does Chainguard get excluded from future co-ordinated disclosures as a result?

php foundation has a blog up about how it all went wrong thephp.foundation/blog/2026/…
Imagine sending a report in to a bug bounty program, and getting a dupe because OpenAI was monitoring your work and filed it a minute before you.


Tim Haines 🇺🇦 retweeted
OK so today we had
- PHP2Shell
- LiteLLM supply chain attack
- Node2Shell
- Gitlab CVSS 10.0
what next? 🫠

Another one 🚨 Gitlab is vulnerable to remote code execution.
1. Firewall your Gitlab server
2. Patch.
CVE-2026-110264 is a CVSS 10.0 unauthenticated RCE in GitLab’s regex compiler. It reaches self-managed CE/EE instances back to version 7.0, while @gitlab.com is already patched.
If you self-host GitLab, upgrade ASAP.

Tim Haines 🇺🇦 retweeted

I am here once again to say “put up or shut up”
One million to open source this year, as we continue to give back to the ecosystem via the pledge.
More than half has gone directly to your favorite open source developers.
blog.sentry.io/another-year-…
