

🔸 Trust none. 🔸 Verify everything. ➡️ https://xitter.cf/t.co/xIlhLHOmdh ⬅️
Кавказские горы, сакартвело
Joined September 2026
- Tweets670
- Following1.4K
- Followers249
- Likes947




Pinned Tweet
🚨 KAVSEC[.]AGENCY'S WEBSITE IS LIVE. NO KYC. NO TRACKERS. NO BULLSHIT. 🔐
Most "security" shops run Google Analytics, take your card, ask for your passport and store it all on someone else's server.
We built the opposite.
🛡 QuietKeys by KAVSEC AGENCY:
- Self-hosted shop on a no-KYC VPS, open-source be-BOP framework.
- Payments in Lightning [with phoenixd]⚡
- Zero trackers, zero ads, one session cookie 🍪
- Everything in EN · RU · FR
🧰 FREE TOOLS (no account, no email, nothing):
- Seedcraft: 15 offline calculators and checkers for self-custody. One HTML file, zero network requests.
- Offline Secret Generator: 1 sheet, 2 dice, 1 pen. Up to 202 bits of entropy, no chip to trust. Perfect for a strong BIP39 passphrase. 🎲
📋 FIRST GUIDE:
"Bitcoin: multisig & nomadism"
A false good idea, or the best protection?
5 architectures, 6 nomad profiles, a 72-hour emergency plan.
The multisig that keeps you safe at home can freeze your coins abroad.
🔸 Every file ships with its SHA-256, check it before you open it.
🔸You can't audit a chip. You can audit a die.
🔸Verify everything.
🔸Trust none.
UPS / DHL, those bast*rds are charging a lot and restrict some goods to be send...
I'm using a local post-service, it cost half the price of UPS/DHL, and NO-RESTRICTION at all.
WTF
🔸 My "eHoly Trinity" :
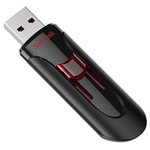
1⃣ 256Gb Cruzer glide from SanDisk
(where I work from, rarely directly to the hard drive, don't forget to back up everything)
2⃣ Yubikey 5 nfc
(3 of them, for redundancy and 2 as a backup in case #1 is lost, (waiting to switch of all them for Open-Sourced's one, hey @nitrokey🤓 need partnership))
3⃣ @SeedSigner with @YTCryptoGuide's firmware + Smartcard Extension aka #ShieldSigner, coupled with @Seedkeeper_io)
Never be too careful. What is your daily tools, set-up or advices ? 🤓


The only proof of work for a product/service is illegalism and sex-industry, if it fits, it will also fit in mainstream.

Devices are safe, someone compromised API Keys on Cloudflare's side.
xitter.cf/FoundationHQ/status/21…

In today's episode... Give a warm GM to @FoundationHQ 😴
s/o embit @StepanSnigirev 👏
@SeedSigner @selfcustodykrux @SpecterDIY still not affected... Are those blackhat tryin' to pwn DIY Project also ? COME AND TAKE IT 🥷
#EverythingIsFuckdUp #DIYorDIE

In today's episode... Give a warm GM to @FoundationHQ 😴
s/o embit @StepanSnigirev 👏
@SeedSigner @selfcustodykrux @SpecterDIY still not affected... Are those blackhat tryin' to pwn DIY Project also ? COME AND TAKE IT 🥷
#EverythingIsFuckdUp #DIYorDIE
okay, devices are safe !
xitter.cf/FoundationHQ/status/21…

ANNOUNCEMENT: SPAM EMAILS HAVE BEEN SENT THAT APPEAR TO HAVE COME FROM OFFICIAL FOUNDATION DOMAINS.
We have traced this back to one or more compromised API keys on Cloudflare, and have already revoked all API keys.
The malicious domain in the spam email has been taken down.
Funds stored on Passport are safe and Passport hardware is not compromised.
We are working nonstop to discover exactly what happened and will put out a report ASAP.
📱 YOUR PHONE IS THE MOST COMPLETE SURVEILLANCE DEVICE YOU OWN. TIME TO TAKE IT BACK.
It knows where you sleep, who you talk to, and when you're awake.
By default, it reports most of it to someone else.
Today we're releasing our GrapheneOS getting started guide. 🔐
31 pages. 24 chapters. 3 levels.
Available in English, Russian and French.
🟢 BEGINNER: the basics, no tech skills
- What GrapheneOS changes, and what it doesn't
- First boot: unlock code, private DNS, updates
- The essential apps: Signal, SimpleX, Proton, KeePassDX, Mullvad, Syncthing…
- What you should never do
- Beginner checklist
🟡 INTERMEDIATE: built-in features and settings
- Per-app network and sensor permissions
- Vanadium, the hardened browser with built-in ad blocking
- Encrypted offline backups with Seedvault
- Duress PIN: one code that wipes everything
- User profiles and Private Space
- Sandboxed Google Play: keep the apps you need, without giving Google the keys
🔴 ADVANCED: verification, hardening, borders
- Verify your install: boot screen, key fingerprint, Auditor attestation
- BFU vs AFU: why you power off, not just lock
- Biometrics: why a code beats your finger
- The SIM: what GrapheneOS can't hide
- Full border crossing protocol and checklist
No magic. No paranoia theater. Just a phone that works for you, not on you.
🔍 Every PDF ships with its SHA-256 hash. Check it before you open it.
🔸 Trust none.
🔸 Verify everything.

🔸As long as Yubico's firmware is closed source, you should check @nitrokey, @SoloKeysSec 🤓
➡️ KAVSEC.AGENCY⬅️


Hey @grok, can you give me 5 reasons someone should follow me?
Tell the truth.


KAVSEC.AGENCY by TosGe ⛓️👨🏼💻 retweeted

⚠️ Searching for Trocador? Careful.
Fake sites copy our design, and some rank above us in search results, even on private search engines.
Check the address before you swap. Our official website is trocador.app
youtu.be/WULJ5vZJLNU?feature…
🚨 ELECTRUM USERS: UPDATE TO 4.8.3 NOW
A high-severity flaw, already exploited in the wild.
How the attack worked:
1. You send a payment
2. A malicious Electrum server blocks it and swaps it, in your history, for a fake one going to the attacker
3. The fake address ends with the same 4 characters as the real one
4. It shows zero fee, so you bump it with RBF
5. That fee bump is the signature that sends your bitcoin to the attacker
RBF isn't the bug, trusting someone else's server is.
3 lessons:
🖥 Run your own server, or at least know whose server you're talking to
🔍 Read the FULL address before signing, on your signer's screen. Last 4 characters prove nothing.
✅ Download 4.8.3 only from electrum.org and verify the signature. Not from a pop-up, not from a link.
Every one of these is a chapter in Bitcoin Hodler: verifying your downloads, a sovereign environment, address poisoning. 📖
Do you run your own Electrum server, or use a public one? 👇

🔥 I ranked 21 Bitcoin signers.
5 years in the shadows: testing hardware wallets, watching Bitcoin Twitter, following every hack, every bug, every vendor drama.
This is where I landed, & some of you won't like it.
My criteria:
🔓 Open code you can verify
📵 Air-gap: QR or microSD over USB, Bluetooth or NFC
🧱 Security model: secure element, stateless or smartcard
📜 Track record, and how the vendor reacts when things break
🔁 Standard backups (BIP39, PSBT, descriptors): no lock-in
🟥 S TIER
Open code, minimal trust in a vendor, and for most of them you can build or flash it yourself. The less you have to trust, the higher it goes.
🟧 A TIER
Serious, Bitcoin-focused tools. You trust the vendor more than in S, and you get polish in return. Yes, Coldcard stays in A after July's entropy bug. The transparent fix and migration guide count too.
🟨 B TIER
Good tools, each with a trade-off: a server in the security model, a newer approach still proving itself, a phone in the loop, or multi-coin roots.
🟩 C TIER
Multi-coin first, Bitcoin second.
⬜ D TIER
Closed code, or recovery models where a company holds part of the keys to your castle.
Now the twist: no signer is the best in the absolute. The right one depends on YOUR threat model. A ranking expires. A method doesn't.
That's the whole idea behind chapter 23 of Bitcoin Hodler: Choosing Your Signer. 📖
Where would you move one device? 👇

ALT https://kavsec.agency
🔹 JSON Bourne-Again Shell 😂
Sunday but rainy day in here.. That's my joke of the day/week/year.
Back to work ➡️KAVSEC.AGENCY ⬅️ is almost done. ☑️
🤖 Made with AI

🔸 Don't. If you are an individual, single signature + BIP39 Passphrase is enough, as long as you are doing it correctly.
Multisig are for boards & company, seedless is crap and Bitkey will forces you to back up your wallet files into a centralized "cloud".
"Bitcoin Hodler: the ultimate guide for onchain sovereignty"
➡️ kavsec.agency ⬅️
