

Escape the Technocracy Podcast | Watchman's Torch Newsletter Extreme Privacy | Rebel intellectualism | Tech warlordism No sponsors = free speech
Joined December 2020
- Tweets309
- Following539
- Followers6.7K
- Likes1.6K





Gabriel Custodiet retweeted

If you use a Ledger wallet bought from CryptoBilis, you need to take action and move funds.
You can follow my new wallet guide in that case youtube.com/watch?v=1FgNJvwu…
Hardware wallets are big targets. Make sure you think twice before you buy one, and where you buy it from.


Situation Update: Ledger can confirm that one of the impacted users’ devices contained an unauthorized hardware implant. Ledger is reaching out to impacted users as part of the ongoing investigation. If you have information regarding the investigation, please reach out to Ledger’s bounty program: [email protected]. As a measure of precaution CryptoBilis confirmed it has ceased sales of all hardware wallet inventory until the investigation is concluded. Ledger is in active communication with CryptoBilis on next steps.
Ledger is working with the appropriate authorities to bring the bad actors to justice, and thanks @SEAL_911 for their collaborative support on the investigation. We have no indication that Ledger’s security infrastructure, systems or services have been compromised. As a reminder, Ledger recommends users who purchased a Ledger device from this reseller to not initiate set up if they have not yet done so. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with a new seed).
Security is a constantly evolving landscape; Ledger is continuously adding security mitigations and is working on further, enhanced anti-tampering solutions.
Scammers often try to take advantage of incidents like this. Rely only on official Ledger channels for updates, and remember: Ledger will never ask for your 24-word recovery phrase.
For assistance or questions, contact Ledger customer support through our official channels: support.ledger.com
Gabriel Custodiet retweeted
"Flock's founder blurred his own house while deploying 170,000+ cameras tracking your vehicle, passengers, and everywhere you go."
The 4th Amendment wasn't written for AI surveillance.
New episode with @Dr_Jon_Padfield covering Flock
#FlockCameras
youtu.be/9GFNPrtkvWU
Gabriel Custodiet retweeted


🔗 Full story: therage.co/letter-7-notes-fr…

Gabriel Custodiet retweeted
Good morning 🌞
What's a good eSIM service that allows you to make calls and works worldwide and accepts btc???
Gabriel Custodiet retweeted

Not the OSI. Not the FSF. Not even Commons Clause itself calls Commons Clause "open source."
This was never about reading code. It's about wearing a label you didn't earn. Full stop.
Call your license what it is. There is honor in truth. There is none in pretending.

Gabriel Custodiet retweeted
People who don’t like AI slop and yet at the same time will trust AI to detect slop are fooling themselves. If you admit AI is doing sloppy job, why would you trust it to rate the sloppiness of a text?
Gabriel Custodiet retweeted
There is another very interesting Operation Orchestra (half fictitious) youtube.com/watch?v=3jQoAYRK…
And I followup done by myself & @WatchmanPrivacy in Riga for @btcplusplus
youtube.com/watch?v=WJB7Z-WG…

Gabriel Custodiet retweeted
The self-proclaimed bastion of free speech just sent lawyers after a website whose only crime is letting people read public posts without logging in.
xcancel (a lightweight, privacy-friendly frontend for X) received a cease and desist letter from X Corp. And it didn’t stop...

Gabriel Custodiet retweeted

I was interviewed by @WatchmanPrivacy. In his words: "Fenigson has much to say.. about how technocratic her home country of Israel has become, and advocates a range of solutions for carving out extra freedom.."
Link to full interview below.
Gabriel Custodiet retweeted
Some people update their firmware.
We update with lead.
@MissBitcoin_ vs a compromised Coldcard wallet
The Final Showdown commences below...
Gabriel Custodiet retweeted
After the Coldcard Catastrophe many bitcoiners are going back to basics.
Let's have a refresher on how to create a new wallet.
With @watchmanprivacy
Gabriel Custodiet retweeted
. @WatchmanPrivacy got silently muted by its own newsletter software while trying to send a security warning. Here's the sequence:
🞄 We sent a Coldcard security advisory to our Bitcoin customers. Twice, to two groups.
🞄 Then Watchman's Torch #31 to paying subscribers.The dashboard reported all three as fully sent. 100% sent. ✅The real number was zero.
All three campaigns show 0.0% opens. On a list that opens at 44 to 67 percent. That doesn't happen. The mail never went out. No notification. No banner. No error when we hit send. We found out because we asked why the stats looked wrong, and support confirmed the account had been restricted.
Then the next campaign, for our upcoming workshop "Access Internet Anywhere," got flagged CRITICAL by the same platform that had rated us EXCELLENT on every scored campaign for months.
Our best guess: the advisory contained words like "hacked" and "move your funds," because it was a warning about a hardware wallet. An anti-phishing filter probably ate an anti-phishing warning. And yes — we sell tools to people who don't want to depend on platforms that can switch them off without warning. And honestly this isn’t the first problem we have either. Confusing GUI, moving subscribers onto a new pipeline has been far harder than it should be. Exporting and onboarding a list you own should take minutes. It hasn't.
What this means for you:
🞄 Nothing is lost. Torch #31 is live and always was. Log in, read it, download the PDF as normal.
🞄 The inbox is a convenience, not the archive.
🞄 If you own a Coldcard: the advisory is in your account, or reply here and we'll send it directly.
🞄 If you're a Torch subscriber on our website, we suggest moving to Substack. Write us and we'll port your subscription.
What we're doing:
🞄 Moving the newsletter to Substack, and changing our own sending infrastructure underneath everything else, so we control delivery and can verify per message that it arrived.
🞄 Substack is a platform too, and that's a trade-off we're making with open eyes. The difference: we keep a complete independent archive of every issue, PDF and audio, and we can leave with our list at any time.
Gabriel Custodiet retweeted
After the Coldcard hack the vultures arrived on schedule, circling in perfect formation, announcing that self custody is de facto dead. You've read the posts. If only these poor souls had kept their coins "on an exchange," none of this would have happened. Adults said this out loud, in public, with their real names attached. So let's do the thing nobody circling the corpse wanted to do. Let's look at the data.
🔴 Mt. Gox — 2014
Hot-wallet theft + years of mismanagement → insolvency
~850,000 BTC (~200k later recovered)
🔴 Bitfinex — 2016
Hot wallet breach
~119,756 BTC
🔴 Coincheck — 2018
Hot wallet breach (NEM)
~523M XEM (~USD 530M then)
🔴 Zaif — 2018
Hot wallet breach
~5,966 BTC + other assets (~USD 60M)
🔴 QuadrigaCX — 2018–19
Not a classic hack: founder death + "inaccessible" cold wallets; monitor found big shortfall / suspected fraud
~26,000 BTC + other coins (~CAD 190–250M+)
🔴 Cryptopia — 2019
Hacked, then liquidation (BTC + alts)
~USD 16M+ initially reported
🔴 Binance — 2019
Hot wallet breach
7,000 BTC (~USD 40M — SAFU covered users)
🔴 KuCoin — 2020
Hot wallets breached
~USD 275M mixed tokens
🔴 BitMart — 2021
Hot wallets breached
~USD 150–200M mixed
🔴 FTX / Alameda — 2022
Fraud & insolvency; customer funds misused
~USD 8–10B shortfall
🔴 DMM Bitcoin — 2024
Unauthorized outflow
4,502.9 BTC (~USD 300M+)
🔴 WazirX — 2024
Multisig / custody breach
~USD 230–235M mixed
🔴 Bybit — 2025
Cold-wallet / signer exploit
~401,000 ETH (~USD 1.4–1.5B), not BTC-led
Custodial and protocol heists together — centralized exchanges plus DeFi and bridges — run into the tens of billions of dollars over their lifetime at event prices, with single bad years clearing USD 2–3B in hacks alone. That's not counting fraud, insolvency, or the founder who dies with the keys in his head.
One Coldcard wave: roughly USD 0.04–0.07B. Do the division. Very rough math puts Coldcard at somewhere between 0.1% and 1% of a single bad year, and comfortably under 1% of lifetime headline losses from exchanges and DeFi combined. It is a rounding error. It is the tip you leave on the bill for everything else that got stolen this decade. And it is being used as an argument to hand your keys back to the same institutions that produced the top of that table.
But I'm not going to end on a smug ratio, because something about this genuinely bothers me. The people who lost money here were not degens. They weren't farming yield on a bridge held together with hope and a Discord moderator. They were the careful ones — the people who read the guides, bought the hardware, wrote the words down on steel, and did everything the responsible adults told them to do. Playing it safe is exactly what got them hit. That's the part that stings, and anyone selling you a custodial account off the back of their pain should be treated accordingly.
The conclusion doesn't move, though. Verify your entropy, verify your seed on a second implementation, stop trusting single black boxes — and understand that from a strict safety analysis, your funds have never been safer than in self custody.
Gabriel Custodiet retweeted
PSA to everyone who generated a new seed this week: The Coldcard advisory has a brutal lesson buried in it. Whether YOUR funds are at risk depends on facts almost nobody records:
— which wallet + firmware created the seed
— the date it was created
— whether dice rolls were added (and how many)
— whether a passphrase protects it
— the wallet fingerprint
24 words are not a backup. They're a key. A backup is everything you need to trust and use that key. We built a backup documentation PDF for our clients at @WatchmanPrivacy as part as our Underground Backup Kit. Given this week's events, it's now free for everyone — no signup, no email, and we will never ask for your seed words. Ever.

Gabriel Custodiet retweeted
It appears the creator of LibNGU and the C-level executive at Coinkite/Coldcard who reviewed and merged it are the same person.
Let me be 100% clear: pseudonymity is good. After what happened to Ledger's team in France, nobody should be forced to doxx themselves.
And anyone implying the anonymity itself is nefarious should reconsider why they're in Bitcoin. Satoshi was pseudonymous too.
So what's the real problem?
One person, Wrote it. Reviewed it. Merged it. Two hats. Zero independent eyes.
The entire point of the pull request process is a second
brain. Once you write code, you read what you MEANT not what you wrote. You cannot see your own work fresh.
Self-review is no review. For a video game or a random web app? Ship it, who cares.
For a library securing people's life savings?
Ask who independently reviewed it. If the answer is
"the author, under a different hat" that's not a review, that’s just a theater.
Gabriel Custodiet retweeted
I've said this in several Spaces but time to write it down.
DO NOT assume the fixed Coldcard firmware is flawless.
It was written and shipped under extreme time pressure and pressure is exactly when new bugs get introduced. There are already reports, unverified but worth taking seriously, of devices freezing or bricking after the update.
So before you update or migrate anything:
1. Verify your seed backup, every word, correct order
2. If you use a passphrase, confirm you have it exactly
3. Record your wallet fingerprint
4. After migrating, test with a small amount first
A bricked device with a good backup is an inconvenience.
A bricked device without one is a funeral.
Urgency is not a reason to skip the boring steps.
The boring steps are what save you.
Gabriel Custodiet retweeted
LISTEN UP COLDCARD OWNERS
Here's my video about the Coldcard catastrophe after a conversation with @WatchmanPrivacy
Gabriel Custodiet retweeted
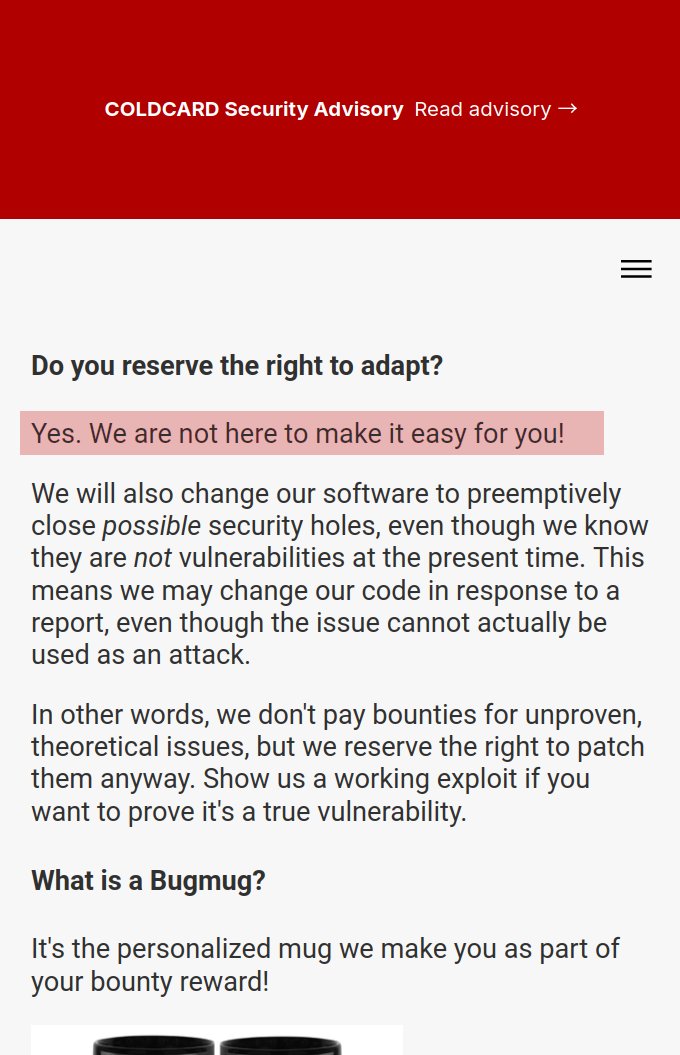
Picture this: you are a researcher and work for a well funded cyber sec lab, find a critical vulnerability and go to ColdCard’s website:
* We don't pay bounties in these cases
And bellow
* Yes. We are not here to make it easy for you!
Why would anyone submit anything? it’s so threatening and no price list published, but you might get a mug while supply last
Gabriel Custodiet retweeted
Our Escape the Technocracy premium Bitcoin course has a 30-minute module on every single way people lose their Bitcoin.
It's not fun. It's not what influencers sell you. It's the most important half hour in the course.
Every time there's a new hack or drain, we check — and almost invariably, it was already in there.
Today's Coldcard entropy bug? The lesson is literally titled "Entropy is difficult for humans."
"Just take a sponsor." We hear it every week, and we proudly have NO SPONSORS. No affiliate links, no hardware vendors paying us. That means we tell you how we see it. We work for you alone.

Gabriel Custodiet retweeted
Ditch modern, fiat skincare and go back to what our ancestors trusted.
✨ Get back to real skincare.
Pay with Bitcoin and receive 10% off your order. ₿ 🧡
sadaorganics.com


For healthy, glowing skin.
There is no second best😌
Buy your beef tallow at sadaorganics.com
Shipping all over the USA 🇺🇸