
Penetration tester
Joined August 2018
- Tweets21
- Following232
- Followers96
- Likes234




Pinned Tweet
Intel #CET killed traditional #callstack #spoofing. Here is how to bypass modern #EDRs telemetry anyway.
New: CET-Compliant Callstack Spoofing via Thread Pool & Enum callbacks.
Manual shadow stack resync via JMP & #INCSSPQ. Article & Rust PoC included👇
mrtiz.github.io/cet-callstac…

Tiziano Marra retweeted

Great work by @_MrTiz and a very long read!
CET-Compliant Callstack Spoofing via Thread Pool Enum Callback Trampolining
mrtiz.github.io/cet-callstac…

Bypassed fully hardened #MicrosoftDefender on fully updated #Windows11 using only free tools: trojanized a legit MS exe with #Shellter, staged an HTTPS reverse shell with #Hoaxshell, then evaded #AMSI & #UAC, in-memory, no zero-days. Read more: mrtiz.github.io/defender-eva…
CVE-2023-35671: #Android App Pin security issue exposes payment cards in #Google Wallet to unauthorized payments
Full PoC video using @flipper_net: youtu.be/reNinRDiBkM
Details: github.com/MrTiz/CVE-2023-35…
nvd.nist.gov/vuln/detail/CVE…
source.android.com/docs/secu…
source.android.com/docs/secu…
Some blogs and online users claim that through this vulnerability it is not possible to make unauthorized payments. This is not true; in fact, if you use a real P.o.S., instead of a #FlipperZero-like device, Google Wallet makes a physical payment. Try it to believe.
Tiziano Marra retweeted

#fakenews are free, real news are behind a paywall. :-/
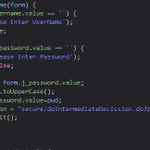
@LeFrecce salvate ancora le #pwd in chiaro nei DB? La mia pwd contiene caratteri minuscoli che diventano maiuscoli nella richiesta #POST e il #login avviene correttamente, cosa impossibile se le pwd fossero "#hashate". Link bit.ly/33N6Or7 @disinformatico @evaristegal0is


In passato #TrenItalia era solita inviare la password in chiaro via mail (anch'esse tuttora non criptate) nel momento in cui un utente cercava di resettarla:
reddit.com/r/italy/comments/…
medium.com/@silvanocerza/tre…
facebook.com/Spottedtrenord/…
books.google.it/books?id=G3p…
