

@GrapheneOS Foundation Tweets my own and not endorsed by my employer. AI slop and DMs mostly ignored.
Joined January 2024
- Tweets279
- Following95
- Followers132
- Likes72





Pinned Tweet
I am now reachable from email if for whatever reason you needed that. Final @ the GrapheneOS domain name.
Amber retweeted
theglobeandmail.com/canada/a… is a very fair and balanced article. They did proper research and talked to experts.
That's entirely unlike nearly all of the coverage by the media in Spain, France, Germany and the Netherlands. In the few cases we were asked for our perspective, nearly nothing we said was included. They acted as sycophants for the state and did not challenge or verify their claims.
Why is it that nearly all the western European news coverage is sycophantic?

Amber retweeted
There's a major state sponsored misinformation and smear campaign towards GrapheneOS in the Netherlands and Germany. The misinformation campaign includes unsubstantiated security claims not holding up to scrutiny to scare people away from it. They're also heavily misrepresenting who uses it overall.
These smear campaigns conflate GrapheneOS with forks and modifications of it sold by shady companies. Those usually include a device management app to remotely manage the devices of their customers as if they're employees. These are largely not GrapheneOS devices or have preinstalled malware apps.
A common tactic being used in these smear campaigns is to make unsubstantiated and outright false claims about the capabilities of forensic data extraction tools. They misrepresent how they get into devices. They want to scare people into using far less secure devices which are easier to exploit.
France, Germany, Spain and the Netherlands are becoming increasingly authoritarian surveillance states with an ongoing crackdown against privacy. It's happening throughout the whole EU and it's likely both secure devices and end-to-end encryption without backdoors are going to end up outlawed.
There are a bunch of companies based in the EU selling phones with drastically worse privacy and security than an iPhone including Jolla, Volla, Murena and iodé. These products are effectively backdoored by not providing standard privacy and security patches/protections while misleading users.
France and other EU countries are actively cracking down on legitimate privacy and security projects while supporting unsafe products within their control. These products make it far easier to remotely exploit devices and also to bypass encryption to extract data. They're phony privacy products.
Each of the companies we've listed have participated in the misinformation and smear campaigns against GrapheneOS. Jolla spent years working closely with Putin's regime. Volla, Murena and iodé are building an EU Play Integrity API. None provides the crucial standard privacy patches/protections.
Murena is directly assisting with state anti-privacy campaigns smearing highly private and secure devices as mainly benefiting criminals. They've repeatedly falsely claimed GrapheneOS is mainly used by criminals. Here are 2 of many examples:
teapawt.org/GrapheneOS/status/2040…
clubic.com/actualite-604786-…
GrapheneOS, end-to-end encrypted messaging apps, Monero and other projects are being targeted with state and corporate propaganda and anti-privacy laws. Meanwhile, the same governments heavily fund and support phony privacy projects clearly downgrading privacy and security compared to an iPhone.
GrapheneOS is only an initial target for these state actors and their sycophants in corporate news organizations. Apple heavily works on protecting users against exploits too. It would be much harder to convince the public that an iPhone is for criminals so they're starting with open source.

Gaël Duval is the founder and president of the /e/ foundation along with the CEO of Murena. Duval and his organizations have consistently taken a stance against protecting users from exploits. In this video, he once again claims protecting against exploits is for only useful pedophiles and spies.
Translation to English:
> There's the attack surface, on that front we're not security specialists here, so I couldn't answer you precisely, but from the discussions I've had, it seems that everything we do reduces attack surface. However, we don't have a "hardened security" approach, we aren't developing a phone for pedo(censored) so they can evade justice. So there aren't difficult things to check if the memory is corrupted, really hardened security stuff that could clearly be useful for executives, in the secret service, or whatever. That's not our goal, our goal is to start from an observation: today our personal data is constantly being plundered and that wouldn't be legal in real life with the mail or the telephone, we want to change that. So we are making you a product that changes that by default for anyone.
Transcription in French:
> Il y a la surface d'attaque, là pour le coup on est pas des spécialistes de la sécurité, donc je ne pourrais pas te répondre avec précision, mais des discussions que j'ai eu, il semblerait que tout ce qu'on fait, ça réduit la surface d'attaque. Donc oui, probablement ça aide. Par contre, on a pas une approche "sécurité durcie", on développe pas un téléphone pour les pédo(bip) pour qu'ils puissent échapper à la justice. Donc il y a pas des trucs pas possibles pour voir si la mémoire est pas corrompue, des trucs de sécu vraiment durcis qui pourraient être utiles clairement pour des dirigeants, dans les services secrets ou que sais-je. C'est pas notre but, notre but c'est de partir d'un constat, aujourd'hui nos données personnelles sont pillées en permanence et ça serait pas légal dans la vraie vie avec le courrier ou le téléphone, on veut changer ça. Donc on vous fait un produit qui change ça par défaut pour n'importe quelle personne.


Amber retweeted
I'm doing the thing until I can convince people that focusing on whether or not AI is being used in intrusions is a waste of time. What will be figured out is that virtually every cyber threat is using AI, because AI these days is as generally available as the internet. Imagine back when the requirement was "threats using the internet." AI isn't an emerging threat anymore. It's the norm.


I seriously hate when corporates think it is okay to refer to anything about their teams and workers with insulting language like "stupid" and "losers". He didn't seem to address that afterward too. A product is nothing without the people who work on it, you must respect them.


New: you think you know Proton, but you really don't.
I spoke to 8 current employees, got Slack chats, meeting audio, and an AI manifesto written by its CTO.
“That’s bullshit and loser thinking,” Yen wrote. “Stop thinking always of how to be slower, and focus more on how to be faster.”
CEO Andy Yen critiques AI in public. But inside, he is pushing everyone to use AI, even those with security concerns 404media.co/manifestos-fear-…

You are not being a firebrand, outspoken, misunderstood or 'just being blunt' by having such an insulting tone to your own workers. You only make prospective employees not want to be supervised by you.
If there is a statement to come of this, that should be the first to address.
Amber retweeted
Our port of the 10th generation Pixels to the Linux 6.18 GKI LTS branch has been through a day of public testing by a couple dozen users. There are no known issues remaining anymore. We're going to continue heavily reviewing the commits and looking for more unhandled API changes.
New boot animation. Check it out!
Amber retweeted
Yahoo is still blocking emails from our newly assigned IPv4 space (206.220.120.0/22). It's likely they're behind on updating their database of allocated IP space. It was already published via arin.net/resources/guide/ipv… and other providers have been accepting it for 2 weeks already.

We threat modelled that this feature could be a notable target for exploits to prevent reboots & keeping data safe when introduced in @GrapheneOS. Compared to iOS, you can configure a shorter reboot time & USB-C port hardware controls prevent USB as a mode of exploit delivery.

NEW: An iPhone hacking company claims it can freeze the iPhone in a state that makes it easier for cops to access data.
The iPhone has an automatic reboot feature that reverts the device to a state where data is harder to extract. This would defeat it.
404media.co/cops-can-bypass-…

Protecting GrapheneOS against malicious use of forensic tools / 0days for unauthorised access is two parts: preventing known tools from working, and designing the OS that the window of exploitability if a capability ever emerged is as short as possible. Nothing is unhackable.
Amber retweeted

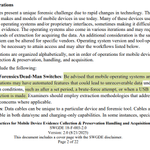
NEW: Apple is preparing to implement a kernel level EDR system in iOS
When activated, the watchdog, known as com.apple.iokit.EndpointSecuritySE, which is still in beta, will monitor deep system telemetry in order to spot signs of exploitation
More details:


Amber retweeted
Secure paste has been merged into GrapheneOS to provide a replacement for focused apps being able to read the clipboard:
github.com/GrapheneOS/platfo…


installed a fucking app called Bing Wallpaper. is this 2007

Microsoft is accused of showing a Harry Potter ad disguised as a wallpaper on Windows 11 PCs that use the Bing Wallpaper app.
Bing Wallpaper is not installed by default, but it used to be a simple, clean app that did not quietly add ads to the desktop.
However, over the past few months, Bing Wallpaper has been engaged in all sorts of sketchy stuff.
Not long ago, we spotted that Bing Wallpaper added a feature that would open Bing .com if you clicked anywhere on the desktop.
The feature was later pulled after outrage, and here we are again with another Bing Wallpaper controversy.
Bing app displayed J.K. Rowling’s Harry Potter + Fantastic Beasts 11-film collection ad on September 7.

ALT Harry potter ad on Windows 11 PC