

Don't trust a cook, that doesn't have any vices.
San Francisco
Joined March 2018
- Tweets612
- Following551
- Followers489
- Likes6.8K





Pinned Tweet
we turned the openai x hugging face incident into a desktop you can log into. everyone has opinions on how ai labs handle safety. almost nobody has seen what it looks like from the inside.
Huggingbreach.com/?v=




Alia Abbas retweeted

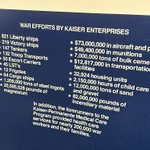
Never going to get over that the AT-AT walkers in Star Wars were originally conceived by U.S. Steel.


Alia Abbas retweeted

This is what I want to see. Swarms used for defense.
(because swarms will be used for offense too)


just saying but Tailscale and Cloudflares’s WARP are not formally verified software (not entirely agent proof themselves).
Alia Abbas retweeted

Quest Diagnostics has been hacked. Patient data was exposed. They serve roughly half of U.S. hospitals and physicians. Investigation ongoing.


incident replication and then having abliterated models have a field day in it is another level of entertainment and doom. enriching landscape to learn on discrete tasks. valuable data.
is minecraft the last safe place on the internet?
> remember Log4Shell started in minecraft chat
> the thing that broke half the internet was discovered by griefing
> there are no safe places
> only servers that haven't been griefed yet
> Mojang's biggest CVE is "creeper got in"
> log off. go mine. touch cobblestone
3% of all cyber benchmarks look at defensive capabilities of models…very concerning. more blue team tasks must be measured
as model deployment starts hitting week to week, it’s not hard to believe and be deeply worried that exploits are going to be happening every day with drastic outcomes.


Alia Abbas retweeted

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
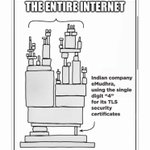
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea

