

I research security of Intel platforms. I don't work for Intel
Москва, Россия
Joined September 2014
- Tweets1.6K
- Following134
- Followers12.2K
- Likes2.3K



Pinned Tweet
Finally, the casket is opened: we (+@h0t_max and @_Dmit) have extracted Intel x86 microcode! One more Intel "top secret" information gets revealed...
github.com/chip-red-pill/glm…


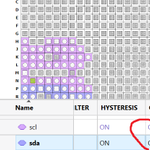
Be aware of potentially danger default settings for I2C SCL/SDA IO pins in Lattice Radiant (Open Drain mode is requred for I2C), as it isn't checked by Map and other tools generating a valid bitstream. This can lead to a damage of a driver even if the slave never sets 1'b1 on SDA


I’m so happy for our hardware Positive Labs (@ivannikovp and others), who are helping me with my Intel research. Together, we’re going to break Intel desktop CPUs!


Mark Ermolov retweeted

Missed one more from the drop lol
CVE-2026-43783 - macOS LPE via DesktopServicesHelper. One XPC request -> arbitrary chown -> root.
PT SWARM writeup:
ptswarm.com/blog/cve-2026-43…
My blog:
andrd3v.github.io/cve-2026-4…
PoC:
github.com/andrd3v/CVE-2026-…

Mark Ermolov retweeted

After 4 years of effort, I'm happy to announce that one of the final secrets of the PS2 has been broken wide open!
It's been a long process of decapping, optical dumping, and now at last a software solution.
Thank you Libby for finding the exploit from our dirty optical dumps!


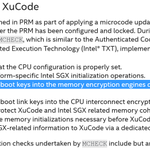
Anyone who has carefully read the Intel article on XuCode (intel.com/content/www/us/en/…) might well wonder: where (from which memory) MCHECK executes? (1/x)

It's not L2 or C6SRAM of CPU module, it's a completely different memory outside of CPU core used also to cache requests to memory controller (D-unit) from all agents including iGPU (5/x)


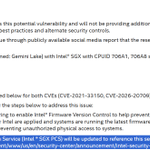
It turns out that Intel Gemini Lake Refresh platforms were supported by the new Intel SGX PCS (Provisioning Certification Service) remote attestation mechanism based on DCAP/ECDSA

This means we have compromised the actual Intel SGX 2.0, and anyone who hoped that only the older SGX was vulnerable was sorely mistaken...
intel.com/content/www/us/en/…

Mark Ermolov retweeted

New exploit: “xor dword [0xf80c2094], 1<<22”
Unlocks CPU microcode, the platform security processor, system management mode, and every internal processor register, all at once, on 100 million AMD CPUs. As far as I can tell can’t be fixed.
github.com/xoreaxeaxeax/skit…
Mark Ermolov retweeted
⭐️My PoC exploit for CVE-2026-31695 in the Linux kernel is ready
🏁I managed to make it absolutely stable on Fedora 44 Server despite an elusive race condition during the exploitation
🛠This vuln existed for ≈5 years before I fixed it upstream
⚡️Gonna publish a detailed article!

