

The man who trades freedom for security does not deserve nor will he ever receive either - OSCP | eCPPT | CRTP | CARTP | CRTO
Joined November 2011
- Tweets1.3K
- Following526
- Followers307
- Likes1.4K



Pinned Tweet
- Have you ever tried to create a phishing campaign using #Gophish?
- Have you ever tried to MiTM using #Evilginx2?
Go beyond that by creating a more sophisticated campaign by migrating Gophish and Evilginx2 under Apache proxy (AaRP)
Alice in PhishLand: lnkd.in/gAZ9kecS
CVE-2022-45608 - ThingsBoard Access Control Privilege Escalation
outpost24.com/blog/access-co…

1) I always trust and will continue to trust the community for sharing my ideas and new methods/implementations/improvements. But there are moments when people escalate your effort and the time you invest and not only don't give you credit but blame you for what you have offered
4) Dylan Evans (fin3ss3g0d) after making some changes, decided to remove me from the credits section. I contacted him in good faith, but he decided to follow the aggressive way accusing me that after the changes that he made, the project is based now on his own solution.


Liatsis Fotios retweeted

Check out our red team's blog on 3 ways to escalate privileges and steal credentials based on real world hacking bit.ly/37pEe5l
Alice in Windowsland: 3 ways to escalate privileges and steal credentials
outpost24.com/blog/Alice-in-… @outpost24 #azure #credentialmanager #sqldumper #redteaming

I just got a voucher for @SEKTOR7net Malware Essentials course from the @RedTeamVillage_! Thank you so much for sponsoring the @RedTeamVillage_'s #CTF at DC29 #DEFCON this year! @lazzslayer @NopResearcher @j0nk1m
Completed the Az AD Lab from #PentesterAcademy! bootcamps.pentesteracademy.c… #AzureAD via @SecurityTube cc @nikhil_mitt

Nicely done and amazing Lab. Recommended for all those who want to expand their skills in AD attacks

Congratulations to @_wizard32 for clearing our Certified Red Team Professional exam! #ADLab #CRTP #PentesterAcademy cc @nikhil_mitt bit.ly/2AXXbM2

@degiroeu My account is still not verified on your side since 11th of June (have been on waiting list since May 8). Try contacting twice through email and I got no reply back. Yesterday after third attempt received a reply similar to "we are under verifying your account"
2/2 A week ago, received an email by you, that my account/money is now available and I can proceed to my portfolio, but once I logged in my account was still under verification @degiroeu
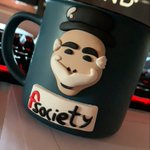
It’s time to finally take back control. Real control. @whoismrrobot Never Forget #MrRobot #handmadecup

Liatsis Fotios retweeted

NTLM reflection is back to haunt windows.
Read about Ghost Potato here (this time with a fixed link): shenaniganslabs.io/2019/11/1…

Liatsis Fotios retweeted
We are proud to launch our brand new interactive XSS cheatsheet featuring novel vectors from @garethheyes
portswigger.net/research/one…

Liatsis Fotios retweeted

Playing with the .NET Manifesto stuff @subTee spoke about at DerbyCon. Kinda nice to use as a springboard for launching TikiTorch payloads.

Liatsis Fotios retweeted

Here's a Cobaltstrike beacon being popped on a VPN client that connected to pulse secure. Will share more information later on in the week or next week with @Alyssa_Herrera_
@bad_packets Is that scary or what?
#CodeExec #CobaltStrike #RedTeam #PulseSecure
Liatsis Fotios retweeted

Lateral Movement Using Outlook’s CreateObject Method and DotNetToJScript
posts.specterops.io/lateral-…