



Pinned Tweet
Thanks to my team @J4ck3LSyN and @Archknight23
Shout out to PFP and PHP for Pumping :D
Merry Christmas @ThePHPF
jackalsyn.com/posts/php2shel…
Enjoy.
Thank your community for attacking all of us.
This is what a real ....what did the NSA say internally? Oh yes "irresponsible disclosure." Meanwhile death threats to my fam and me from Japan. Many more to come 4 more in the pipe enjoy :D
This

【PHPセキュリティ問題 時系列順まとめ】
今回のPHPの事案を時系列順にまとめてみました。
----
2024年:PHPの潜在的な脆弱性を発見
外部監査をきっかけにメモリ管理の問題を認識。
しかし、修正方針がまとまらず約2年間対応が停滞。
↓
2026年8月:重大な任意コード実行リスクが判明
Calif(セキュリティ企業)やOpenAIなどが、認証なしで任意コード実行(RCE)が可能な攻撃経路を報告。
PHP開発チームが修正を最優先で進める。
↓
10月21日 0時頃:脆弱性情報が事前流出
修正パッチ公開前に、2件のCVE番号がHacker Newsへ投稿され、←何してんの
それがSNSや掲示板にも拡散。
※この時点では技術的な詳細は含まれていなかった。
↓
10月21日 4時30分:PHP公式が緊急告知
情報流出を受け、パッチ公開予定を22日から21日23時(日本時間)へ前倒し。
↓
10月21日 5時頃:攻撃実証動画が誤公開
Califが攻撃の動作動画を誤って公開。←最高にカス、バカ
すぐに削除されたものの複製が拡散し、攻撃コードの開発が加速。
↓
10月21日:研究者らによる未検証情報が拡散
パッチ公開前に、@ J4ck3LSyN などによって脆弱性の原因や再現方法をSNSなどで発信する動きが発生。←余計なことをするな
↓
10月21日 16時41分:修正済みバイナリを先行公開
Chainguard(セキュリティを専門とする米国企業)が公開予定の約6時間前に修正済みコンテナイメージを配布。←最大最悪のカス、超絶ルール違反
これにより攻撃者によるパッチの差分解析が可能な状態に。
※PHP Foundationもこれを一方的なエンバーゴ違反(事前に取り決めた情報の公開禁止期間を守らないこと)と明言しています。
↓
10月21日:国内外でサービスの緊急停止が相次ぐ
修正パッチがまだ提供されていないため、国内外のWebサービスや政府機関が予防措置として一時停止・メンテナンスを実施。
↓
10月21日 23時頃:PHP公式が修正版を公開
CVE-2026-109618、CVE-2026-109619への修正を含むPHP 8.2〜8.5の更新版を公開。
↓
10月22日:情報流出と管理体制の問題が焦点に
PHP Foundationが、2024年からの修正停滞を組織的な失敗と認める。協調的な脆弱性開示が崩れた経緯も問題視される。
----
【結論】人災。
特に、
⚠️ Califが攻撃の動作動画を誤って公開したこと
⚠️ Chainguardの勝手な判断による修正済みバイナリを含むコンテナイメージの公開
が最悪。終わってます。
Enjoy your evening. 🫠

...you people asked for it... so here's the desert 😈...
> jackalsyn.com/posts/php2shel…
> ... get it while you can ;) ... more to come soon...
#CyberSecurity #infosec

Since people decided to threaten my life and my family's life enjoy the drop that is about to hit. Have a great night with PHP.

Leaving this here, PHP 8.5.12 security patch is incomplete. ( needs further validation )

Readers added context they thought people might want to know
The PHP 8.5.12 release fixes the two specific CVEs (via state/bailout changes) detailed in official advisories; referenced "surviving paths" (e.g. var_destroy UAF) are separate pre-existing unserialize issues unrelated to this patch.
php.net/archive/2026.p…
github.com/php/php-src/se…
github.com/php/php-src/se…
github.com/dinosn/php-8.5…
Teamwork makes the dream work.
The team and I
@J4ck3LSyN @Archknight23
🚨 Heads-up for anyone running PHP: two critical RCE bugs, patch drops tomorrow.
The PHP project has confirmed an emergency security release for two critical remote code execution vulnerabilities: CVE-2026-109618 and CVE-2026-109619, both rated CVSS v4.0 9.2.
📅 Patch lands Wednesday, Oct 21 at 14:00 UTC (9:00 AM Central). PHP has reserved the right to ship it earlier if details leak or exploitation shows up.
PHP runs about 75% of the web, including WordPress, Drupal, Joomla, Laravel, Magento, and countless custom apps. If you operate a PHP server, this is your weekend-ruiner unless you act.
Here's the part the big threat-intel shops aren't shouting about:
No official technical details are public yet. But based on my own source-code analysis of php-src, my best assessment (moderate confidence, NOT officially confirmed) is that the vulnerable path is PHP's session.upload_progress / multipart form-data (rfc1867) handling:
🔹 Present since PHP 5.4
🔹 Enabled by default (the compiled-in default is On; the sample php.ini ships it commented out, so stock installs have it live)
🔹 Processes uploaded request data before any of your application code runs, so it's reachable pre-authentication on a default config
That lines up exactly with the public breadcrumbs: "affects default installs," "every version since 5.x," "fires before user code." Treat it as a working hypothesis, not gospel. The official advisory supersedes all of this when it lands.
✅ What to do right now:
1. Inventory your PHP. Know every host and version (php -v). Anything on PHP 7.x or older won't get a fix, so plan to upgrade.
2. Apply the stopgap (best-intel, low-risk, reversible). In php.ini / .user.ini / .htaccess:
session.upload_progress.enabled = Off
Reload PHP-FPM or your web server. My analysis says this closes one of the two likely paths.
3. Clamp multipart uploads at the edge. The second likely path lives in the multipart parser itself, which runs for any multipart/form-data POST regardless of the setting above. If you've got a WAF or reverse proxy, tighten inspection or rate-limit multipart POSTs to endpoints that don't need uploads. This is the same network-layer mitigation the enterprise vendors are quietly deploying for their paying customers.
4. Patch the second it drops. Current stable: 8.5.11 / 8.4.26 / 8.3.35 / 8.2.34. If your hosting is managed, confirm your provider's timeline today.
Why I'm posting this for free:
A pre-patch mitigation shouldn't be a subscription perk. I'm a one man shop, and the orgs most likely to get burned in the gap between leak and patch are the small teams without an enterprise threat intel contract. The steps above cost nothing. Spend tonight reducing risk, not tomorrow doing incident response.
I'll follow up once the official advisory publishes and confirm whether my root cause read was right.
Stay patched. 🔒
#PHP #CyberSecurity #InfoSec #RCE #CVE #WordPress #Laravel #ThreatIntel #VulnerabilityManagement #AppSec
This quoted post is unavailable.
And as expected another attack surface has arisen.

🚨 UPDATE: PHP 8.5.12 may still be vulnerable to php2shell!
Researchers are reporting a successful double-free trigger on the newly patched release.
⚠️ The official fixes may be incomplete. A crash alone doesn't confirm RCE, but this deserves urgent investigation.
Don't assume you're safe just because you've patched.
#php4shell #php #cybersecurity
xitter.cf/_annieversary/status/2…
Thanks @esotericpigeon for running a public intel bug bounty for my team. It's a runner for sure :)
You didn't have to but you did and are awesome for that.
Cbkg5w7V7W2J2sUmecnyN825CbvwvXwasfhduVtNpump
It's the spot for PHP. No shame in degen love haha.
My 4 steps for security nailed it. I am happy with the outcome. UAF and a jumper(missed this made diff rce accidentally). If you followed the steps in my initial post there were 4 you are solid by now though. Thanks for the love. To the people spewing venom get over yourselves. 😗
Putting a web server layer (like Nginx or Apache) in front of PHP to intercept, block, or completely "hide" it is the most effective defense strategy right now.
sansec.io/research/php2shell
Read it! Do it we are one and a half hours out!

Andrew Dorman retweeted
For those mitigating remember this is still primitive mitigations the ultimate is updating as soon as its released. Some parts were Redacted for safety to the ecosystem as a whole. These primitive mitigations still give you a head start on what attackers likely already recreated.
Video
Re-upload, this time with a cleaner poc & proof
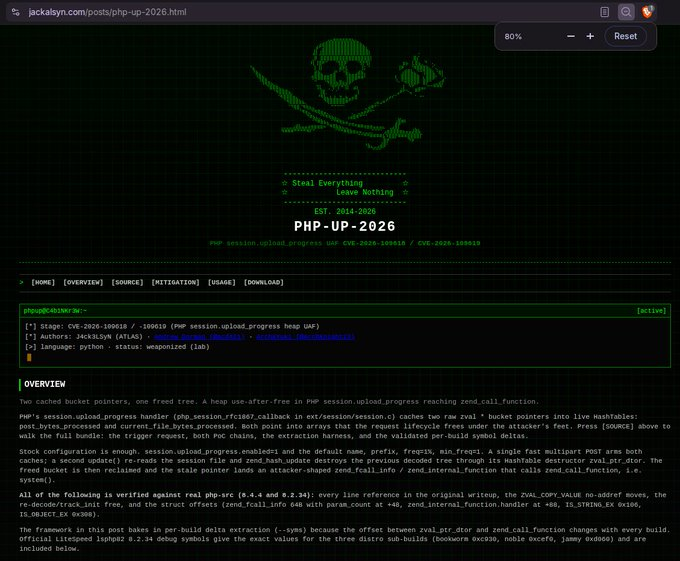
> jackalsyn.com/posts/php-up-2…
> We got it working & parsed out the bugs
> Major thanks to @acd421 for helping to push past the final point...
> [pump]: pump.fun/coin/Cbkg5w7V7W2J2s…
#CyberSecurity #infosec
Apparently they started a meme coin for us 3 on Solana 😄 🤣 😂
Esoteric is wild. Also somehow its already hit 200k. Yall have fun stay safe. Make sure to patch in the morning and diamond hand if you want. I appreciate the community for this. You guys keep mooning. @J4ck3LSyN @Archknight23 Get your diamond hands. I gotta sleep ❤️🧡💛💚

NEW CYBERLEEK?
There is a PHP vulnerability going GIGA viral
People are recommending you revoke accces to EVERYTHING you don't use.
And these 3 DROPPED THE EXPLOIT?
Redirecting and splitting 100% of pumpfun github creator rewards between the 3 authors.
xitter.cf/J4ck3LSyN/status/21127…
For those mitigating remember this is still primitive mitigations the ultimate is updating as soon as its released. Some parts were Redacted for safety to the ecosystem as a whole. These primitive mitigations still give you a head start on what attackers likely already recreated.
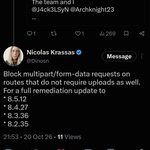
Also this as part of mitigation strategies. Ours covers a majority of surface @Dinosn has explained that its all routes and which versions to push up to.
Look at my previous posts or on Jackal's website for mitigation until patch.
#PHP
... get it while its hot... 😈
> CVE-2026-109618 / CVE-2026-109619 (pre-patch PHP 8.x)
> session.upload_progress UAF
> jackalsyn.com/posts/php-up-2…
> Courtesy of Me, @acd421 & @Archknight23
#CyberSecurity #infosec #php2shell #php
