


addBTC retweeted

Lab grown diamonds crashed the price of diamonds. What will lab grown gold do to the price of gold?

Last month, we demonstrated high-rate alchemy: turning mercury into real, stable gold, beating CERN’s record by a factor of 10.
Last week, we enriched isotopes in the world’s most powerful plasma centrifuge, beating the Soviet record that stood for 40 years.
Now, we’re building a fusion reactor in San Francisco to achieve record power density.
addBTC retweeted

i mean, if malicious actors can replace all the hardware inside the device... surely they can also replace a sticker that looks "genuine"
addBTC retweeted

Oof, this post did not age well for @Ledger !


Hi there, instead of relying on a sticker, Ledger uses Cryptographic Attestation.
Every time you connect a device to Ledger Wallet, the software sends a cryptographic challenge directly to the Secure Element chip. If the hardware, chip, or internal firmware has been modified or altered during manufacturing/shipping, the cryptographic check fails, and the app will flag the device as non-genuine.
The Secure Element chip is designed to detect physical tampering and will refuse to execute unsigned code or pass the genuine check if extra hardware attempts to intercept signals.
A cryptographic proof performed directly by the hardware chip is infinitely more secure than a physical sticker.
addBTC retweeted

Broadcom, makers of your favourite raspberry pi...


addBTC retweeted
Verifying the Ledger Nano S Plus Hardware
Verifying the Ledger Nano S Plus Hardware was easy, but verifying the security chip turned out to be not so easy. For those who asked, the weight is 20.230 grams with the metal. 7.404 grams for just the plastic unit.
Links: messervices.cyber.gouv.fr/vi…
shop.ledger.com/products/led…
Liked this video? You can 1-off donate: paypal.com/paypalme/eevblog donateopen.com/@eevblog

addBTC retweeted

Single-Board Computer
Raspberry Pi 5 8GB
$225.00 each
4284N202
Fun fact, Raspberry Pis are an extremely popular solution for running digital advertisement signs 😀

Behold, the discovery of the key logger.

the ledger incident could go way beyond hardware wallets
imagine someone starts putting the same kind of spy implants inside logitech keyboards, or any other big brand of computer gear that's in millions of homes
they could do the same with laptops, phones, tablets and so on
and steal not just crypto but money straight out of your banking apps
this is a really telling example that just exposed a huge threat to every one of us. nobody is safe anymore


addBTC retweeted

While Ledger is trying to downplay a massive amount of their wallets being backdoored, Trezor is lying about the existence of their own wallets being found with backdoors.
And then you have other competitors shilling their product with “we are immune to this” while having an unspoken list of other problems.
The crypto space is so sketchy 😂

Trezor joins the backdoor party!
A few hours ago Trezor posted there is “not a single piece of evidence that Trezor devices have been compromised”. Which conveniently leaves out the fact that @joegrand found implanted Trezor wallets IN THE WILD and even notified Trezor 2 months ago.
Story by @KimZetter:
zetter-zeroday.com/trezor-wa…
🧵13

Everyone is frantically trying to invent the @COLDCARDwallet

Following the tampering of @Ledger devices and the theft of funds, wouldn't it be better for major hardware wallet manufacturers (Ledger, Trezor, Safepal, Bitbox, Ellipal, ColdCard, etc.) to start considering the production of transparent models?
At the very least, this would save users from having to play amateur mechanic by opening up the device!
It probably wouldn't solve the problem, but at least major changes would be noticed.


addBTC retweeted

Honestly looks sick.
But I think ledger's recent fiasco is worse then coldcard, coldcard was a extreme fuck up in code I am not defending it coinkite but letting some PHYSICALLY install shit on your devices is another level of incompetence


The worst part was @Ledger marketing of “secure display”
The implant was enabled by very fact that the display was insecure.

Je vois ici et là de la compassion pour Ledger. Vous êtes sérieux ?
@Ledger a été très négligeant, en refusant de voir les failles béantes de leur devices, que de simples actions auraient corrigé :
- rendre l'ouverture de leur Nano/Stax destructrice en collant les plastiques : on connait ça sur de nombreux appareils jugés "irréparables"
- designer le contenu des boitiers pour ne laisser aucune place vide disponible pour un implant espion eSIM/5G
- noyer l'intérieur des Nano S Plus (sans batterie) dans une résine époxy remplissant tout l'intérieur du boitier comme les terminaux de paiement : zéro place pour l'implant
- chiffrer le bus entre le display et le secure enclave comme un simple DRM qui vous empêche de faire vos screenshots Netflix, et qui empêche donc à l'espion de lire votre écran
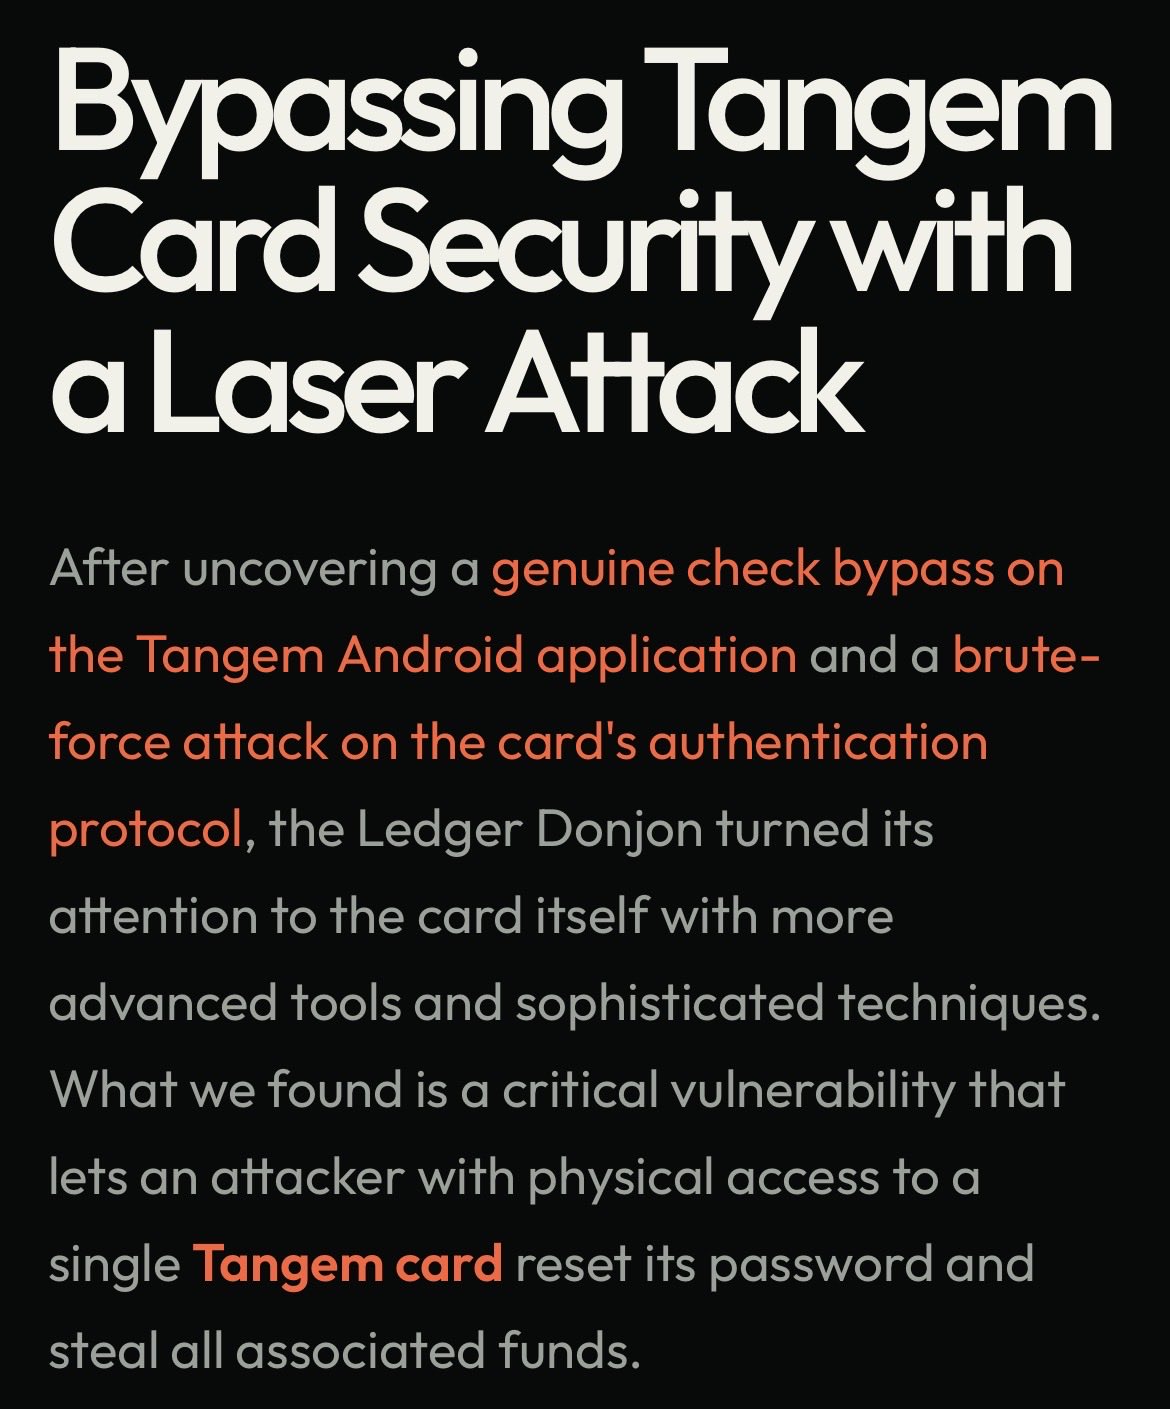
Dans le même temps @DonjonLedger a dépensé 300,000€ et 6 mois de travail acharné pour tenter de disqualifier leur concurrent Tangem, en proposant de pénétrer une faille sous conditions dantesques :
- de trouver une carte Tangem
- qu'elle soit remplie
- d'avoir du matos à 300k€
- d'avoir une expertise pointue dans le domaine
Dans la théorie, Ledger n'a aucune faille.
Dans la pratique, Ledger c'est $200M drainés (hack actuel + ceux du passé).
Dans la théorie, Tangem a ses failles (avec un laser nanosecond à 300k€, ou en envoyant la seed phrase au support client dans de rares cas de seeds importées ayant contacté le support client sous 7 jours).
Dans la pratique, Tangem c'est $0 drainés.
Tangem c'est une carte plate NFC sans batterie, dans laquelle un implant eSIM/5G et une antenne serait quasi-impossible à dissimuler.
En s'acharnant sur ses concurrents, et en délaissant ses clients, Ledger devient complice de ce drain, et est tout simplement inexcusable.

addBTC retweeted

It's remarkable that the Ledger supply chain infiltration was able to grow to the scale it did given that we were aware of these implants ~6 months ago (thanks @joegrand!)

Reverse Engineering a Ledger Nano X Hardware Implant (@_TROPICON) slides are up! grandideastudio.com/portfoli…

ALT A real-world hardware implant discovered inside of a Ledger Nano X cryptocurrency wallet

Great technical overview by @eevblog

EEVblog 1780 - Ledger Hardware Supply Chain Attack Examined
00:00 - Ledger Nano X hardware wallet supply chain attack
06:16 - This is not a new thing
09:00 - DaveCAD explaining how the Ledger Nano X works
11:40 - Common Criteria EAL5+ security verification
12:34 - How the hack works
14:21 - Viewing the Ledger PCB and hack boards in detail in KiCAD
18:57 - Anyone could be in on it!
19:38 - What can manufactures do to help stop hardware hacks?
20:21 - Don't have exposed traces
21:00 - This applies to credit card payment terminal and ATM's too
22:17 - Different package selection can help
23:52 - Potting compound
27:45 - Basic crypto hardware wallet tips
Links: github.com/KarpelesLab/ledge… st.com/en/secure-mcus/st33j2…
Forum: eevblog.com/forum/blog/ledge…
addBTC retweeted
EEVblog 1780 - Ledger Hardware Supply Chain Attack Examined
00:00 - Ledger Nano X hardware wallet supply chain attack
06:16 - This is not a new thing
09:00 - DaveCAD explaining how the Ledger Nano X works
11:40 - Common Criteria EAL5+ security verification
12:34 - How the hack works
14:21 - Viewing the Ledger PCB and hack boards in detail in KiCAD
18:57 - Anyone could be in on it!
19:38 - What can manufactures do to help stop hardware hacks?
20:21 - Don't have exposed traces
21:00 - This applies to credit card payment terminal and ATM's too
22:17 - Different package selection can help
23:52 - Potting compound
27:45 - Basic crypto hardware wallet tips
Links: github.com/KarpelesLab/ledge… st.com/en/secure-mcus/st33j2…
Forum: eevblog.com/forum/blog/ledge…

72 hour update on reseller CryptoBilis incident 🔽
As the investigation continues, we are working with relevant authorities. The volume of impacted devices is limited. We know this is concerning, especially for those directly affected, and we are reaching out to impacted users.
To date, all confirmed cases related to the disclosed draining incident of Oct 9th, 2026, involve devices sold through the Southeast Asia reseller CryptoBilis. Our systems and direct sales channels remain unaffected.
We take the CryptoBilis situation seriously and are actively investigating.
We encourage impacted users to reach out to Ledger Support through official channels and file complaints with their local law enforcement authorities. As a reminder, CryptoBilis has confirmed having ceased all sales of hardware wallets.
We are reminding our authorized resellers and distributors to source products only through authorized channels and never to restock returned products.
Also, we strongly advise users not to purchase from unauthorized resellers, where the risk of buying suspicious, counterfeit or modified devices is important as nothing operates under ledger security guidelines.
Security isn’t static and this incident underscores why we continuously review and strengthen our distribution and anti-tamper processes.
We are continuously improving that work now and events like this strengthen our resolution: reviewing authorized reseller controls, advancing hardware protections, and cooperating with authorities. Thanks to @SEAL_911 for their collaborative support and all their efforts.
This is an ongoing threat that doesn’t just impact Ledger, but the whole ecosystem, and we are calling others in the space to work with us on making improvements for users.
We believe in jointly working with researchers, other vendors and partners on improving industry chain-of-custody practices and anti-tamper techniques. Raising the bar on physical supply-chain integrity benefits the entire ecosystem. If you have relevant information, contact [email protected].
For CryptoBilis buyers: do not initialize unused devices. If already set up, move to a new seed on a device from Ledger. If you have concerns that your device was impacted by the CryptoBilis incident, please contact Ledger Support through the official site: support.Ledger.com.
Ledger Support is available 24/7 to answer your questions and concerns.
Scammers often try to take advantage of incidents like this. Rely only on official Ledger channels. Ledger will never call you, DM you, or ask for your 24-word recovery phrase.