

Web3 Enthusiast | learning Cybersecurity
Joined November 2022
- Tweets2.1K
- Following2K
- Followers288
- Likes26.8K




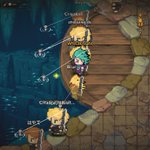

why this name no mames

EXCLUSIVE: We’ve uncovered 3 #GTAVI branded beer labels, including a brand-new Vice City beer 🍺👀
Pißwasser, Patriot and “No Mames Vice City” all appear in the discovery.
Here’s what we found. 👇
gtavice.net/news/exclusive-g…

13
4rham retweeted

Indian law enforcement froze $3M from an innocent Chinese investor after mistaking a crypto bridge for a pig butchering scam. Now an Indian court has ordered Gate to hand his funds to a person they never belonged to.
My analysis of how Indian LE traced through an unlabeled service and wrongly froze @xxxkeym's Gate account:
The case stems from a pig butchering victim who allegedly lost $1.7M of BTC, USDT, DOGE & SOL in May 2025.
Andhra Pradesh CID registered it as Cr. No. 10/2025 and filed a charge sheet in March 2026.
In July 2025, xxxkeym had Gate deposit address 17mpajZ6Nq3dG3T6wUhaXxYF4Qy9HJnYx5 frozen after depositing 15 BTC from 3NcBhqK in the following transaction:
885f3afab562251b222363cf12095e864ddb94636674b01f0cdb05997e5a54a0
This is one transaction Indian LE cites in its notice. 3NcBhqK was funded by xxxkeym's own OKX & Binance withdrawals in Jan 2023 and the coins sat dormant for years until the Gate deposit.
Indian LE never froze his OKX or Binance accounts, the actual source of the 15 BTC, which tells you how flawed their justification is.
Gate froze his entire account, which held roughly $3M at the time and about $1.5M today.
The Indian court order hands all of it to the complainant.
Gate deposit address 17mpajZ also received two deposits for 15 BTC total in 2025 from bc1pkkwqyxn3rm608ryuqg9hyqna0syq4jx5pxkr7pzg8n3usx6tyqfst5u966, which is also controlled by xxxkeym.
Shortly before the deposits to Gate, bc1pkkw was funded in three transactions by bc1quzwkggdf6ly06mrrnnled0qdr57w770k45n5n7 & bc1qtu66zfqxj6pam6e0zunwnggh87f5pjr7vdr5cd.
bc1quzw & bc1qtu66z were reported as alibarbit[.]bit, the same scam named in Indian LE's press release.
That was a mistake. Both belong to the Merlin Chain bridge, which is unlabeled in most compliance tools.
xxxkeym is simply a normal Merlin user trading tokens on the L2. This wrong label is the only place the scam touches his transaction history.
Below is the blockchain data showing each Merlin withdrawal by xxxkeym matched to a BTC payout from those addresses, plus screenshots of the bridge activity.
xxxkeym bridged 50 BTC into Merlin on March 28, 2024, over a year before the alleged May 2025 theft.
His three withdrawals came out of that balance. I found zero onchain connections between xxxkeym and the theft.
Separately on July 15, 2025 xxxkeym had a 7 BTC private key compromise theft which was reported to local police and also SlowMist was engaged. His stolen funds flowed to Wasabi.
This is embarrassing incompetence by Indian LE, who seem incapable of reviewing basic blockchain data.
Indian LE, the prosecutor and the judge all signed off on this, Gate froze the account, and LE did a full press release about it recently, while the real victim here (the Gate user) hasn't had access to his funds for nearly 16 months.
My hot take is VASPs need to challenge weak jurisdictions like India, Canada, etc due to repeated negligence in criminal cases.
Merlin source transactions from xxxkeym
10.1368 BTC - March 25, 2025
0x975081c2a62355019561c3ec0d01c72bf0dadf7121d46764bbb13ac0013a9a06
4.9071 BTC - May 6, 2025
0xa30f7b770e2e8e2e2d0fc0d390aa800e7f880e8e129d1b705dbc4167fc878769
9.9796 BTC - June 17, 2025
0x147429d324520c9ebee8015b0214dbd7bdce97ee37ad25e11819f4b04aecc049
Bitcoin destination transactions to xxxkeym
10.1367 BTC - March 28, 2025
55ab5373c2daa69b1728e6551b59f9dc661d1d78786face798d5251ccbe4685a
4.907 BTC - May 9, 2025
b2222fe38856e65420f15051a4cc419a92868803dec69a218f007948972ea367
9.9795 BTC - June 19, 2025
094f01388638523fb29aac0a0d4f70adf6949fede0847a45cef2c3f930692c73
Merlin Chain bridge
bc1quzwkggdf6ly06mrrnnled0qdr57w770k45n5n7
bc1qtu66zfqxj6pam6e0zunwnggh87f5pjr7vdr5cd
Gate deposit address - xxxkeym
17mpajZ6Nq3dG3T6wUhaXxYF4Qy9HJnYx5
Other addresses - xxxkeym
3NcBhqKnyo8dfzqfG1p5rbaKJFV8yLnx3u
bc1pkkwqyxn3rm608ryuqg9hyqna0syq4jx5pxkr7pzg8n3usx6tyqfst5u966
0x59fd8E3aEca4FAbb53ef6078D2319Dc174fb66a6
July 15, 2025 BTC theft addresses
bc1qjmf2e4fc2r97rq762055ag3g9uhypavta0payq
bc1q80gq7ctfsm6p9h9jh2k45da87jy6s7a87pj3h0
March 28, 2024 50 M-BTC destination transaction to xxxkeym
0xf1ee67ba1d3f97fb2d4776fa8ffc90f0b7ba7d116de3bf510a2c6aeae7d80def


4rham retweeted
Modern life can feel like being in a sci-fi story—all that is missing is the aliens. They probably won’t appear in 2027. Here are ten other things to watch out for bit.ly/3UCxXw9
Illustration: Cleon Peterson

4rham retweeted

WEMIX Bug Bounty Program is now live on CertiK Hunt🛡️
Security researchers can now explore the scope and submit vulnerabilities related to WEMIX3.0, with rewards of up to $10,000 based on severity and impact 🔐
Start hunting below 👇
hunt.certik.com/explore/wemi…
📢 See the full announcement at #WEMIX community
👉wemix.com/news/wemix-fortifi…

4rham retweeted

Learn harness engineering with a project-based course covering environment, state management, verification, and control mechanisms for AI coding agents.
github.com/walkinglabs/learn…

4rham retweeted

New "ethical hacking" forum: ForumNOX
Clearnet: forumnox[.]com
Dark Web: http://tyoeevaqn6alon623bfm7r4e7z3so54ky6uvbqkza3fyun7g4cm24hyd[.]onion

4rham retweeted

🇮🇩 🚨 INDONESIA: CNBC INDONESIA APPLICANT AND STAFF ID DOCUMENTS ALLEGEDLY FOR SALE
A seller on a dark web forum is offering what it claims is a 5.5 GB cache of CNBC Indonesia recruitment and HR files for $1,000, covering 908 people (job seekers, psychological test candidates and contract staff).
The files allegedly include:
• National ID cards (KTP) and family cards (KK)
• Tax ID (NPWP) documents and payslips
• CVs, diplomas and academic transcripts
• Personal photographs
⚠️ Analyst Note:
Unverified threat-actor claim, NOT confirmation of a breach. CNBC Indonesia has not commented and no sample was verified. The record count is small, but identity and payroll documents are highly sensitive and well suited to loan fraud, identity theft and fake-recruiter scams.
#DDW #DarkWeb #Indonesia #DataLeak #IdentityTheft #Media

4rham retweeted

Salah satu finalis Clash of Trenchers, @degen2ex mengubah 1 sol jadi 10 sol kurang dari 20 menit
CRAZYYY
4rham retweeted

Indonesian President Prabowo Subianto has accepted the resignation of Vice President Gibran Rakabuming Raka, according to people with knowledge of the matter bloomberg.com/news/articles/…


4rham retweeted

THIS IS THE MOST DANGEROUS DEAL IN THE ENTIRE AI BOOM.
Anthropic needs Broadcom's AI chips to run Claude.
It does not buy them directly.
Instead, Wall Street banks and Blackstone put $63 billion into a separate company, and that company buys the chips from Broadcom.
That company then rents the chips to Anthropic.
Over the life of these leases, Anthropic owes about $161 billion in rent on Broadcom equipment.
So where does Anthropic get the money to pay that rent?
Partly from Broadcom.
Broadcom has agreed to lend Anthropic up to $42 billion, and that money can only be used to pay rent on Broadcom's equipment.
Broadcom sells the chips, then lends the customer money to pay for them.
If Anthropic cannot pay the loan back in cash, Broadcom can take Anthropic shares instead.
So why is this dangerous?
First, the sales are not as real as they look. When a company lends its customer the money to pay its bills, part of its revenue is just its own cash coming back.
Second, everything depends on one customer. Broadcom's own filing warns about its dependence on a small number of customers for AI chip demand.
Anthropic alone owes $161 billion on its equipment.
Third, Anthropic does not have the revenue yet. It made $16.96 billion last quarter but has committed $895.4 billion to compute.
Many of these contracts must be paid even if Anthropic never uses the capacity.
Fourth, the chips are the collateral. AI chips lose value fast as newer models come out. If Anthropic cannot pay, lenders are left holding equipment worth far less than the debt.
If AI demand slows, the whole chain breaks at once.
Anthropic misses payments, Broadcom loses its biggest customer and its loan, and the banks and Blackstone take losses on the debt.
This exact setup played out in 1999 and 2000.
Lucent and Nortel lent billions to their own customers to keep equipment sales growing. When those customers went bust, the loans were never repaid, and both stocks collapsed.
The current situation is getting dangerously close to the dot-com bubble.


4rham retweeted
Does it concern anyone else about how all of these other offshore CEXs with little to no US presence rush to immediately cut off MEXC users from transferring assets?
Who is actually being protected by it…
What % of MEXCs total volume was illicit?
I can go to any large CEX and flag 9-10 figs in illicit activity.
I think anyone can agree MEXC historically has had a quite relaxed AML / KYC policy.
But the $16B illicit amount being alleged by FinCEN seems overstated to me so I’d like to see the data and comps.
Starts to feel a bit of gov’t overreach for cases like HTX or MEXC when much worse offenders like Kucoin are not being sanctioned...
4rham retweeted

🚨 UPDATE: Binance hacker moves $430,000 in stolen funds through six self-created $NEAR meme coins in just three days, per Elliptic.


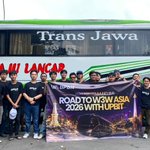
Let's go trip to Jakarta
@W3WOfficial @UpbitID
#Web3Weekasia2026 #upbiindonesia #Communitybus #JogjaJakarta

2
51
4rham retweeted

🚨BREAKING: North Korea-linked hackers are using MEMECOINS to launder funds from the $6.4 BILLION Binance hack, Elliptic reports.
Between Nov. 5 and 7, the hackers created at least six memecoins on NEAR, spending about $90 per token to launch them.
They then moved 117,000 NEAR worth about $430,000 through liquidity pools on decentralized exchanges.
Routing funds through those pools can make them harder to trace. Elliptic spotted a similar tactic after the 2025 Bybit hack.


4rham retweeted
🚨 Google Gemini safety bypass allowed users to download AI-generated images that its own filters had blocked
Security researcher Jason Kao of Fog Security discovered a flaw in Google Gemini that allowed users to retrieve images the AI had explicitly refused to generate, including sexualized and copyrighted content.
The issue involved Gemini's download functionality, which sometimes delivered previously rejected images even when the conversation displayed an approved image. No jailbreak or prompt manipulation was required.
The vulnerability was reported to Google in June 2026, but the company declined to track it as an abuse bug. By October 22, researchers could no longer reproduce the issue, with Google attributing the change to routine maintenance.

4rham retweeted

Here's five Github Repos to help you build your second brain:
- G Brain by Garry Tan
github.com/garrytan/gbrain
- LLM Wiki by Karpathy
gist.github.com/karpathy/442…
- AI-Memory by Akitaonrails
github.com/akitaonrails/ai-m…
- Agen Second Brain by Smixs
github.com/smixs/agent-secon…
- COG by Huytieu
github.com/huytieu/COG-secon…
SHARE WITH A PERSON WHO WILL FIND THIS USEFUL AND BOOKMARK TO SAVE IT FOR LATER

4rham retweeted
🚨A wave of CYBERATTACKS hit Asia in the past FEW WEEKS.
🇲🇾 Malaysia (Oct. 13)
RM1.985M (~US$489K) was allegedly drained from a Terengganu royal family member’s accounts at two banks, based on a civil suit.
🇸🇬 Singapore (Oct. 29)
A forged letter triggered a US$12.8M transfer to Cambodia. All funds were recovered.
🇹🇼 Taiwan (Nov. 3)
Hackers breached a SinoPac vendor and pulled NT$41.76M (~US$1.27M) from 419 customer accounts in one day. Customers were refunded.
🇰🇷 South Korea (Nov. 5)
A hacking wave hit 37 financial firms since Sept. 30. About 473,000 records leaked and ₩1B (~US$733K) was stolen.
🇮🇩 Indonesia (Nov. 7)
FortiGuard detected around 350,600 cyber threat events this weekend, with 214,000 aimed at the financial sector.


Indonesia’s banking sector is under ATTACK.
Indonesian banks and financial firms faced roughly 214,000 cyber threats in just 24 hours.
FortiGuard Labs recorded about 350,600 threat detections across Indonesia in the 24 hours to November 7, averaging four per second nationwide.
Banks, insurers and other financial firms accounted for 61% of the total, more than all other sectors combined.
The figures show how often attackers targeted the sector. No bank breach was confirmed by the data.
In neighbouring Malaysia, attackers defaced Bank Rakyat’s externally managed website on Friday night.
Officials said banking systems remained secure and reported no data theft.


4rham retweeted
🚨 MetaMask confirms infrastructure breach, hackers diverted Ethereum staking rewards
MetaMask has confirmed that attackers gained unauthorized access to part of its staking infrastructure in September, redirecting approximately 0.385 ETH in rewards by manipulating recipient addresses.
The company says its wallet infrastructure, customer funds, private keys, and recovery phrases were not compromised. However, precautionary shutdowns of affected Ethereum validators caused temporary withdrawal delays and missed staking rewards for some customers.
MetaMask has secured the affected systems and is working to reimburse impacted customers. Regular wallet users do not need to take any action.

4rham retweeted

Not your keys, not your coins?
Apparently, it's now:
Your keys, our RPC. Your coins, our permission.
A scammer sends 0.0001 dust to your wallet without your consent.
You didn't approve anything. You didn't interact with the scammer. You simply received an unsolicited transaction on a public blockchain.
Then Phantom's compliance filter kicks in:
"Your address has interacted with a flagged malicious entity. Transactions disabled."
Wait. WHAT?
So a random scammer can poison my wallet address with dust, trigger your automated risk detection, and suddenly I can't use your wallet interface to move my own assets?
Welcome to self-custody, where you own the keys but apparently need corporate permission to use them.
The blockchain didn't freeze my account.
The centralized frontend did.
The irony is almost too good.
We built crypto to escape banks freezing our money, only to end up with fintech apps wearing a decentralization costume.
If a wallet can unilaterally disable your ability to transact because some random third party sent you dust, maybe it's time to rethink what "self-custody" actually means.
Not your keys, not your coins?
More like:
Your keys. Their rules. Their permission.
Peak Web3 UX. 🤡
