

A technology company that develops tools to self-analyze blockchain transactions provides services to locate and recover stolen cryptocurrency.
Joined July 2022
- Tweets300
- Following586
- Followers605
- Likes72




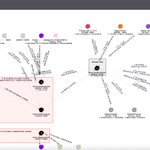

This is what the cluster of addresses belonging to the Binance fund thief looks like now on the Ethereum, Tron and Bitcoin networks.
The AML Crypto team continues to monitor the movement of the stolen assets and analyse the transactions linked to the attack.
bholder.amlcrypto.io/shared/…


Separately, we would like to note that if your company keeps its own lists of cryptocurrency addresses associated with illegal activity, we recommend flagging the above-listed addresses as “Stolen Funds.”
If your platform is receiving funds from these addresses, we recommend that you immediately suspend transactions and freeze the received assets according to applicable legal authorities and internal AML procedures.
“Based on our analysis, these addresses are linked to the movement of the stolen Binance funds.
bc1q0mtc2f5agpkvlq6hhahmfr3hlr55kyfjhl2mnm
bc1qalwnl7dtaa73fsq5tyn0ghfy3fgfpqkt69tca8
bc1qf5cyvv9w50tx9xx9s3xwsne0z87wvjj9l8a35u
bc1qg3nrzpuvq2pxqx74tcrywr09dc208ze96n3t53
bc1qjwdw6vrzq4vf6hckutvx4ucj86awwv99mxnz7w
bc1qm2j6v3247khlwzxl7p9vqnfkghcllyhv9wjaat
bc1qm8v88m5fy6kuq9myva2eemwycxqd3e0zcrs2l8
bc1qs3aej5tmcdz0vctz8y9rjcxtxg8v5385577s56
bc1qs6xnmhar38z44g2za93pv8ygdcwurrh8l87w3v
bc1qdfhmlrdvg4tm87zjl0vyf0xflp5ql50q3g88gw
bc1qnq6jj9jmlf3945m3l8s0kxnqehrsga300k8t3s
bc1qxrxujwxfnvz040jw76d26zhjdg5jura7hs968s
bc1q63qrfrpsg5hh0zzn3kp2xx9vljl7dq7tatsjxp
bc1qepc70u3u476vgvg3hfcwjgu4mecxe2uchs4lag
bc1qz8hdwv8gmml0u96dsvnzsagz6krjyzxmgxupdp
bc1q42flhayrzy3zh8lkyevw8qcjduurt9a35wlsyx
bc1q2wvz0kcsn4hqmajwtey30ud27fl25w8pveznn6
bc1qhuq4genel5cuj00p7ggn30dwnzzjsw8mz3z2je
bc1q96qkjsye5qruf9yksqdqg09lzdmur7wau2ga6u
bc1qdyy9q2lrnn5qh3ju996pgt95eesvc38lppdewn
bc1qn43ejagzgxgle394ynmv5sv3f9ydc48qme7t02
bc1qk8kpt0suefus8zz3fp78w8993frc5x97w423wl
bc1qrsrh56k4rpal88w0xpjuul0m78ud62akcwue5e
bc1qt8mrl9uchasf7pqhwlz6ezm9g44x7xj0vs6zqz
bc1qvws6kh5vjf7apg7f82wd5av8w2gmfj2zxkm8jc
bc1qsmvvvvya6ak2gmsjcxc06ns7yrsx7q4x492vf2
bc1q66l8z9htj4cd7pf8nnlc6mrxyssudm6hyg7a2a
bc1ps696gdcgw8qhm5fepajpta0q4t2j4554dfcmjlgeyfasdejlcs5qerdn38
bc1pq2wttx8d4nd0rs63zrlgqv2l9cdn5u3ekmvvkyrslcqfr006zafspg44uy
bc1pkc75m3yqpadhx5macx5yghlgtuujnalh67qw797etnepd8cm6czqm7kygw
bc1ps9dcuc4ams0u394kmv2rgd97gj00xgjplr8fx09ml4udtlpldmzsrsxdd8
bc1qxg0l4p6xc50zuv9cl5f0l0wmaxjpg8wcy7s9ra
bc1qrg025e2pgx0rwya2kpgtj30972p64jt0hn6zyt
bc1q0ts8gaf9ht0rr4u02hr56f8thndqsc4kmkmfv3
0x811f15855476156ebf86ba3b84fafb8ceaa4e84c
0xb3ddec0ccc5c3ba733fcdf5a15f98c95ec5a5fdb
0xcf4ca2bdf21bc3a467a00b6afe72b833982723e0
0x9749292d74fd460982d0912ea9515ea24736c762
0x600d6f00eadabdb514561ceeb43730a7103e8298
0x8532fa14acaf483729c449b8458aeddb900543d4
0x42cdf00c85005630cc8605731b9364f712077810
0x3e2bf1ac6bf0934bbba6456c341c2ecbced632d5
0x0ddf0480016e6bcb2c1f5d190d221fba1320697e
0x0e772ee615c7f93373c7519f2c36e780696477d3
0xf01c98b3bef6cc96bd484e092cc2a56016ac2ed6
0x00fc00edbe7c003b006f870068c548940000223e
0x8d53903625b8e839b9df4bd28b0efb1cd6b8639a
0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c
0x5c23023ca6633f91ded909b4a753a3ca00fea4fc
0x7f9dc988b46336ad536828fad50fa8fa1e5415e3
0xaa246bf639586a6ba46762d378ce50ca4fc654a0
0xc887af690e0301cd4edbbce8f8d31b4ec65b286a
0x008f06f04b72da2621a4f37f5531cc7352187dcd
0xe7024ab80143b1ef843efe6a58368696cb87958d
0x54401f80da97893a15d43566184635b6674bc942
TCzBTkqn66yApqbYoPezaEQosM5DAd7Y62
TPBkSjkCMn2ckrMuAP8n2J1jdjbw76bKN4
TSpe5HC3PRD2svJcr1YoGszhHk2mtkyZ8A
TG5iBMQPrDzJJAUM8GMVBf1hRaJ1wvzsGi
Tether also froze an address linked to Binance that had been compromised:
0x28C6c06298D514Db089934071355E5743bf21d60
Funds were withdrawn from this address by the attackers. Tether subsequently froze $1,351,530 of that address.
The blue rectangles in the chart represent addresses blocked by Tether and Circle.
t.me/CryptoAlertReport/17651


Credit is due to the Binance team for their rapid response to the incident. The freezing of $2.5 billion in assets involving Tether and Circle is proof of the incident response processes that are in place and the coordination that can take place.
The AML Crypto team, meanwhile, is already tracing the stolen funds, following their movement on the blockchain, and is ready to assist with the ongoing investigation.

Started with an EIP-7702 delegation, but Binance 16 signed with its own key, so their signing is compromised. Tether & circle froze ~$2.3B, exploiter still borrowed 20k WETH on aave.
In total:
~$3.5B drained on ethereum,
~$5,64B counting Bitcoin and Tron.
~$880M freezable but not frozen.
So we have approximately $5.643B in outflows from Binance-labeled wallets as Tether and Circle freeze at least $2.316B in stablecoins
• Ethereum: $3.528B
• Bitcoin: $1.449B
• Tron: $628M
• Arbitrum, Optimism and Base: $38M combined.
As AI tech evolves, we need to re-evaluate our approaches to vulnerability hunting, no matter how much you think you know.
AML Crypto × @Officer_secret: New Crypto Crime Investigation Insights
We took a look at some data that was allegedly obtained from a data breach at the Wagyu crypto exchange, along with @Officer_secret.
The results have already allowed us to progress on various investigations that were previously stopped for lack of necessary information from Wagyu.
This is why it matters.
Wagyu: 10,139 Users records, 38,628 orders, and new connections in crypto incident investigations
As part of a partnership between @aml_crypto and @officer_secret , we decided to conduct a detailed analysis of datasets presumably obtained as a result of a data leak from the crypto exchange/swap service Wagyu.
- Wagyu officially acknowledged (by @PerpetualCow ) a data leak from its service covering the last 3 months.
- The hacker group WhiteArmor allegedly demanded $5 million not to publish the data, but after the refusal, they carried out their threat and published the deal data.
What do the investigated data contain?
Users — 10,139 records
Orders — 38,628 records
Total: 48,767 records in two tables.
The order data is particularly interesting for blockchain analytics, as it can be used to match incoming and outgoing transactions, discover relations between addresses and reconstruct the flow of assets through the exchange service.
Why is this important for investigations?
When investigating hacks, thefts and other crypto incidents, analytical firms and independent investigators often need information from centralized services. Making formal requests through law enforcement often means blocking stolen funds and obtaining details to help identify parties to transactions. Not all the platforms react quickly, some don’t react at all.
Wagyu has been in similar situations in our practice, unfortunately. “We had some investigations where our teams were working on Wagyu never responded to requests from law enforcement officials. So, victims and analytical companies need to look for other legal sources to trace the movement of stolen assets.
What was established?
A quick analysis of the datasets allowed us to merge previously separate clusters and find connections between several branches of fund movement. This includes links that were not possible to reliably establish from on-chain analysis alone without additional data from Wagyu.
Another interesting point is that it is in the data we found operations that Wagyu itself labeled hacks and thefts. So the platform has systems that can detect suspicious transactions. At the same time the respective orders are in status “Executed”.
The natural question is when did Wagyu decide these operations were linked to illegal activity? Perhaps the analysis was performed after the deals were completed. If yes, how effective are the current AML monitoring tools and what does the platform do when it identifies such operations?
We hope Wagyu will fix the shortcomings in its procedures and reconsider its approach to cooperating with law enforcement and analytical companies.
Separately, we draw the attention of @DCENTWALLETS , @Poloniex , @DEXXai_EN / @DEXXai_CN, @bitget , and Channels Finance.
If law-enforcement officials investigating your occurrences still have not obtained the necessary responses from Wagyu, the results of analyzing this data may assist create further linkages and advance the investigations.
We will continue studying the datasets, matching transactions with known incidents, and verifying the discovered clusters.


7/8 Message to Affected Projects
We would like to draw your attention specifically to:
@DCENTWALLETS, @Poloniex, @Dexx, as well as the teams at Bitget and Channels Finance.
If, during the investigation of your incidents, the flow of stolen funds led to Wagyu but you never received the necessary responses from the service, the results of our analysis may help establish additional connections and advance the investigation
We are open to collaborating with affected projects, their investigative teams, and law enforcement agencies.
8/8 Work Continues
Together with @Officer_secret, we will continue to analyze Wagyu’s data, cross-reference exchange transactions with known crypto incidents, and verify the connections we’ve identified.
Our goal is not simply to track the movement of stolen assets, but to help investigations move forward even in cases where on-chain analytics had previously reached their limits.
Sometimes, information that has been missing for months can help restart an investigation that had reached a dead end
Insider threat: how 825K USDT left a payments company
A payments company came to us after a theft. Malicious logic had been planted on the server of its payment system. It monitored outgoing USDT payments and, for any payment above 600,000 USDT, replaced the recipient address with the attacker’s.
On June 2, 2026 at 11:12:09 UTC, it fired. 825,000 USDT went not to the intended recipient but to TG89AYoDT3EiNyBEsgWoBfiSxfVXjQCHiJ on TRON. Transaction: ad69d92960c99865508eb8d13946fb7431f84b1d86395801fea6dbb21993079d.
🤖 Made with AI

$10,000 reward for information that helps identify the attacker. Paid upon results. Contact: [email protected].
To services. If funds from these addresses reach you, halt the transaction and contact us. Any service that freezes the funds will receive a reward of 10% of the frozen amount. The offer applies to every service, including those operating without KYC.