






Pinned Tweet
If you're new to exploit development, reverse engineering or vulnerability research, bookmark this before buying another course.
Blackstorm Security has published 1,600+ pages of research for FREE.
Windows kernel exploitation.
Driver reversing.
Patch diffing.
Chrome / V8 / WebAssembly.
Hyper-V.
macOS / iOS internals.
Modern mitigation bypasses.
Real CVEs taken from root cause to working exploitation.
Their CVE-2024-30085 series alone spans hundreds of pages and multiple exploitation strategies.
This is the kind of material that teaches you how vulnerability researchers actually think, not just how to run tools.
19 research papers. 1,657 pages. Free.
Start here:
blackstormsecurity.com/resea…
Author: @ale_sp_brazil
Focus on the techniques not the tools (X64DBG, GHIDRA/IDA, WINDBG, GDB GEF)
#ExploitDevelopment #ReverseEngineering #VulnerabilityResearch


cr3ghost retweeted

Let’s set the record straight: @lcfr_hax was the first to discover php2shell and develop a working exploit. See his August 5 tweet: xitter.cf/lcfr_hax/status/208503…
His work convinced the PHP Foundation to invest in fixing this entire bug class. He then worked around the clock to review, test, and retest the patches.

cr3ghost retweeted

To teach a lesson,
After Wiz rushed to buy php2shell domain and use its marketing machine to steal the spotlight, I spotted "phpbleed" in a recent Calif tweet and bought phpbleed.com before wiz could pull the same stunt again.
A big budget can buy a domain. It shouldn't buy someone else's research credit.
If you have contacts at CISA or in the press, do the right thing: make sure the researchers who actually did the work get the recognition they deserve.
Hack the planet. Credit the researchers.

cr3ghost retweeted
If you're into Active Directory, Entra ID or identity security, bookmark this.
Researcher @_dirkjan has built one of the best FREE identity security research archives online.
The rabbit hole covers:
- Active Directory internals
- Kerberos
- NTLM relaying
- Forest trusts + SID filtering
- AD CS
- mitm6 + krbrelayx
- Zerologon
- BloodHound
- Entra ID internals
- Primary Refresh Tokens
- Windows Hello for Business
- Conditional Access bypasses
- OAuth + token abuse
- Cloud Kerberos Trust
- AD -> Entra lateral movement
- Entra -> AD lateral movement
- Temporary Access Pass abuse
- Federated credentials
- Managed Identities
- Intune certificate abuse
- ROADtools + ROADrecon + roadtx
- Actor Tokens
Some absolute classics:
- Relaying Kerberos over DNS
- NTLM relay to AD CS
- Active Directory forest trust bypasses
- Domain Admin from Entra via Cloud Kerberos Trust
- Phishing Primary Refresh Tokens
- Windows Hello key abuse
- Conditional Access bypasses
- Global Admin in every Entra tenant via Actor Tokens
There are also years of FREE conference slides, demos and presentations.
Blog:
dirkjanm.io/
Talks + slides:
dirkjanm.io/talks/
Huge credit to @_dirkjan / Dirk-jan Mollema for publishing so much deep identity research openly.
#ActiveDirectory #EntraID #RedTeam
A re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1.
github.com/forrest-orr/Doubl…

cr3ghost retweeted

🚀 Introducing DeepInfer, our in-house inference framework, now fully open source!
Powering DeepSeek-V4.1-Flash at scale with high throughput and low latency. We’re sharing our production stack to help the community lower compute costs, reduce energy use, and make AI more affordable.
🔗 github.com/deepseek-ai/DeepI…
1/4

cr3ghost retweeted
Proper old-school hacker energy.
If you're into Windows internals, exploit development, malware memory or reverse engineering, Forrest Orr's (@_ForrestOrr) work is absolutely worth bookmarking.
The FREE archive covers:
- Windows memory corruption
- Stack overflows + ROP
- DEP, ASLR + CFG
- Shellcode development
- Windows internals
- Malware memory artifacts
- Phantom DLL Hollowing
- Process injection + hollowing
- Memory scanner evasion
- Moneta memory analysis
- PE internals
- Browser exploitation
- Chrome UAF exploitation
- Firefox / IE exploit chains
- Sandbox escapes
- Defensive memory analysis
And unlike a lot of modern security content, there are actual tools, PoCs, shellcode and exploit-development experiments to go with the research.
Blog:
forrest-orr.net/
ExploitDev repo:
github.com/forrest-orr/Explo…
Some of this is older material, but that's part of what makes it good. Proper fundamentals and low-level research that still teaches you how the machinery actually works.
Huge credit to Forrest Orr (@_ForrestOrr) for keeping it publicly available.
#ExploitDevelopment #WindowsInternals #ReverseEngineering
cr3ghost retweeted

Secure boot is total security theater. Too easy to cheat from windows um without doing any kind of preboot attack. But even assuming preboot was required just buy an AMD mobo or an intel one with bootguard fused off and flash your own fw and freely lie about secure boot status
cr3ghost retweeted
If you're learning malware analysis or reverse engineering, bookmark this.
RPISEC released the full materials from its Malware Analysis university course for FREE.
12 lectures + 10 hands-on labs + 4 projects covering:
• Static + dynamic malware analysis
• x86 + IDA
• Windows internals + WinAPI
• Malware behavior + persistence
• Anti-disassembly
• Anti-VM + anti-debugging + anti-AV
• Packing + unpacking
• Windows kernel + drivers
• Rootkit techniques
• Hooking + DKOM
• Anti-forensics + covert channels
• Runtime process manipulation
• APT sample analysis
It was designed for students starting with zero reverse engineering experience and built heavily around Practical Malware Analysis.
github.com/RPISEC/Malware
Huge credit to RPISEC and original authors Branden Clark, Austin Ralls and Aaron Sedlacek for making the course materials publicly available.
#MalwareAnalysis #ReverseEngineering #WindowsInternals


cr3ghost retweeted
This @BeyondTrust incident is worth reading, especially if you work in detection engineering or threat hunting.
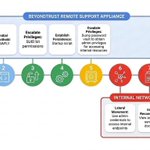
@Mandiant says ARMORY CASTLE exploited CVE-2026-102764 in BeyondTrust Remote Support as a zero-day.
Post-exploitation got ugly:
- SAWFLY PHP webshell
- Service account -> root
- Attempted credential vault extraction
- Persistent passwordless root access
- Systematic log deletion
- BARECLAW WebSocket/SOCKS5 tunneler
- Admin session abuse
- Pivoting into downstream systems
But the part defenders should read twice:
BeyondTrust says its sensors fired high-severity alerts in real time when the actor escalated privileges.
A third-party automated triage system closed them as false positives.
Their separate threat-intelligence-driven hunting pipeline later surfaced the activity.
That is such an important detection engineering lesson.
Having telemetry and alerts is only part of the job. You still need strong detection engineering, active threat hunting, validation, R&D and people who understand what the adversary is actually doing.
The sensors saw it. The surrounding detection process failed to escalate it.
Excellent research and transparency from the @Mandiant and @BeyondTrust teams.
Mandiant technical analysis:
cloud.google.com/blog/topics…
BeyondTrust incident timeline + BT26-05:
beyondtrust.com/blog/entry/b…
Patch BT26-05 and read both write-ups.
#ThreatIntel #DetectionEngineering #Infosec
cr3ghost retweeted
🚀 DeepSeek-V4.1-Flash-1017 is here!
Stronger benchmark performance, faster task completion, and shorter outputs than the previous version—a Pareto improvement in performance and cost. Now live on our website, app, and API.
🛠️ Optimized for @DeepSeekHarness, Tencent CodeBuddy, WorkBuddy, and more. Upgrade to DeepSeek Harness v0.2.1-rc.1 or later for the best experience with the new model.
1/4


cr3ghost retweeted
Galaxy S26 Ultra: untrusted_app → root.
Introducing "Infinity Core": 6 vulns in the Linux kernel's core subsystems.
Their impact spans Linux server LPE, container escape, and Android LPE.
Details: github.com/V4bel/InfinityCor…
cr3ghost retweeted

🧠 How Secure Boot & TPM 2.0 Power Anti-Cheat
This guіdе еxplains exactly why Secure Boot and TPM are mandatory, breaking down remote attestation and the hardware-level trust anti-cheats use to stop cheaters.
👉 guidedhacking.com/threads/th…

cr3ghost retweeted
If you're into malware analysis or reverse engineering, bookmark this.
@hasherezade has built an incredible collection of FREE research, tools, articles and talks covering:
- Malware reverse engineering
- PE internals + analysis
- PE-bear
- PE-sieve + HollowsHunter
- Process injection + hollowing
- Malware unpacking
- Ransomware analysis
- Custom malware formats
- Rhadamanthys
- Petya / NotPetya
- Shellcode + in-memory implants
- V8 JavaScript bytecode deobfuscation
Her research archive goes back more than a decade, with everything from classic Windows malware analysis to Black Hat USA 2026 research.
Projects:
hasherezade.github.io/
Articles:
hasherezade.github.io/articl…
Talks + slides:
speakerdeck.com/hshrzd
Huge credit to @hasherezade for publishing so much of this work and tooling openly.
Absolute rabbit hole for malware analysts, reverse engineers and threat researchers.
#MalwareAnalysis #ReverseEngineering #Infosec


cr3ghost retweeted
This is why the anti-cheat arms race is getting so interesting.
Riot is pushing Vanguard further into hardware-backed trust, attestation, VBS/HVCI, IOMMU and deeper platform security.
At the same time, AI-assisted reverse engineering is making it much faster to tear apart the software sitting on top of those protections.
@k0mkc is showing heavily devirtualized VGK internals and says he can now devirtualize the entire thing.
On the EAC side, @in19h has published tooling that recovers large parts of a heavily virtualized Easy Anti-Cheat Linux sample into readable code and IDA artifacts:
github.com/19h/eac-linux-dev…
There is an important parallel here with EDR.
An EDR is only as effective as the detection engineering, threat hunting and R&D behind it. Anti-cheat works the same way.
You need researchers constantly following new techniques, detection engineers turning that research into useful telemetry and detections, and people actively hunting for behaviour that existing rules may miss.
That means continuously keeping up with:
- new cheat architectures
- kernel abuse
- BYOVD
- hypervisors
- DMA
- firmware tricks
- input manipulation
- virtualization + obfuscation
- new bypass techniques
The game was already there. AI is speeding it up and lowering the barrier to reversing, classification, devirtualization and research.
That forces both sides to iterate faster.
A lot of respect to the Vanguard team as well. They have clearly been keeping up with some of the most cutting-edge work in Windows security, hardware-backed trust, kernel security and anti-cheat research, and their recent Vanguard On-Demand changes show how quickly the defensive side is evolving too.
This is becoming a much faster research cycle on both sides.
Where does the arms race go next?
Huge credit to @k0mkc and @in19h for the research.
#AntiCheat #ReverseEngineering #WindowsInternals


BREAKING NEWS: Riot just announced Vanguard On-Demand. Vanguard no longer needs to start at boot.
If you enable Secure Boot, TPM 2.0, VBS, HVCI, and IOMMU, Vanguard will only run while you play. Microsoft built a Runtime Driver Attestation Report that lets Vanguard verify driver integrity without needing to be present at boot.
For everyone who complained about Vanguard running at startup, this is the answer. Enable your hardware security features and it goes away.
The blog also breaks down every cheat vector in detail: kernel exploits, BYOVD, DMA hardware cheats, bootkits, hypervisors, and pixelbots. With real data showing cheaters deliberately downgrade to older Windows to avoid security features.
riotgames.com/en/news/vangua…
Some of the best security engineers in the industry working on one of the hardest problems in gaming. Massive respect for publishing this level of detail publicly.
@deteccphilippe @nickeverdox @aidankhoury
#AntiCheat #Vanguard #GameSecurity


This is why the anti-cheat arms race is getting so interesting.
Riot is pushing Vanguard further into hardware-backed trust, attestation, VBS/HVCI, IOMMU and deeper platform security.
At the same time, AI-assisted reverse engineering is making it much faster to tear apart the software sitting on top of those protections.
@k0mkc is showing heavily devirtualized VGK internals and says he can now devirtualize the entire thing.
On the EAC side, @in19h has published tooling that recovers large parts of a heavily virtualized Easy Anti-Cheat Linux sample into readable code and IDA artifacts:
github.com/19h/eac-linux-dev…
There is an important parallel here with EDR.
An EDR is only as effective as the detection engineering, threat hunting and R&D behind it. Anti-cheat works the same way.
You need researchers constantly following new techniques, detection engineers turning that research into useful telemetry and detections, and people actively hunting for behaviour that existing rules may miss.
That means continuously keeping up with:
- new cheat architectures
- kernel abuse
- BYOVD
- hypervisors
- DMA
- firmware tricks
- input manipulation
- virtualization + obfuscation
- new bypass techniques
The game was already there. AI is speeding it up and lowering the barrier to reversing, classification, devirtualization and research.
That forces both sides to iterate faster.
A lot of respect to the Vanguard team as well. They have clearly been keeping up with some of the most cutting-edge work in Windows security, hardware-backed trust, kernel security and anti-cheat research, and their recent Vanguard On-Demand changes show how quickly the defensive side is evolving too.
This is becoming a much faster research cycle on both sides.
Where does the arms race go next?
Huge credit to @k0mkc and @in19h for the research.
#AntiCheat #ReverseEngineering #WindowsInternals
BREAKING NEWS: Riot just announced Vanguard On-Demand. Vanguard no longer needs to start at boot.
If you enable Secure Boot, TPM 2.0, VBS, HVCI, and IOMMU, Vanguard will only run while you play. Microsoft built a Runtime Driver Attestation Report that lets Vanguard verify driver integrity without needing to be present at boot.
For everyone who complained about Vanguard running at startup, this is the answer. Enable your hardware security features and it goes away.
The blog also breaks down every cheat vector in detail: kernel exploits, BYOVD, DMA hardware cheats, bootkits, hypervisors, and pixelbots. With real data showing cheaters deliberately downgrade to older Windows to avoid security features.
riotgames.com/en/news/vangua…
Some of the best security engineers in the industry working on one of the hardest problems in gaming. Massive respect for publishing this level of detail publicly.
@deteccphilippe @nickeverdox @aidankhoury
#AntiCheat #Vanguard #GameSecurity
cr3ghost retweeted

I can independently verify these results are semi-correct. However there are a lot of issues with this output. I will cover it in this thread 👇
This binary is protected with CodeVirtualizer for context.
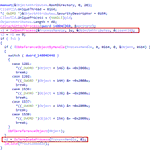
(Proper devirt on the left, vs AI on the right) func: 0x237F0


Devirtualized Easy Anti-Cheat (EAC) for Linux via Gemini 4 Argon and GPT 6.1 Sol using Hex-Rays IDA Assist's MCP: github.com/19h/eac-linux-dev…
