






Pinned Tweet
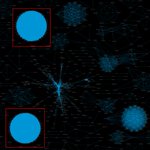
Here's my write-up on how to use perceptual hash algorithms to track malware campaigns that use visually similar maldocs (e.g. #Emotet, #QakBot, #Ursnif). Also released graph_similar_document_images.py that will graph out visually similar maldocs.
bromium.com/spot-the-differe…


Alex retweeted

We’ve just published YARA rules and Python scripts to our GitHub that detects and extracts #IcedID and #BazaLoader malware from Excel add-in (#XLL) files.
Alex retweeted
New #PurpleFox EK campaign spotted in the wild.
An IE Exploit was hosted on this domain:
hxxps://feneffecsdoteteat.aixgedbubirtsabkhotsswse[.]shop
C2 (registered on 25/07/2021):
hxxps://8ze[.]me/u.php?id=1

Alex retweeted
We’re super excited to share our research into #opendir malware hunting and announce a new framework at #VBLOCALHOST @virusbtn this October! Hope to see many of you there.
Alex retweeted
#PurpleFox EK now exploits CVE-2021-26411, demonstrating a short PoC-to-ITW time. On 12 April we isolated a sample from a HP Sure Click Enterprise customer in the Middle East. More details in our write-up by @stoerchl on the HP Threat Research blog.
threatresearch.ext.hp.com/pu…

ALT Timeline showing the history of CVE-2021-26411. The PoC-to-ITW time is highlighted in orange.

ALT Process execution flow of the CVE-2021-26411 exploit isolated by HP Sure Click Enterprise.
Alex retweeted
We saw high volumes of #Dridex malspam last week, showing up as three groups when clustering samples by filename similarity.

Alex retweeted

Bromium's Patrick Schläpfer explains how to extract payload URLs from Dridex samples and provides a python script to do that threatresearch.ext.hp.com/dr…

Alex retweeted
We're pleased to share the HP-Bromium Threat Insights Report for July 2020. Highlights include a look at the top document malware file types and office exploits we've seen in 2020 so far, and insights into recent #Aggah, #QakBot and #WannaMine campaigns.
threatresearch.ext.hp.com/hp…

Here's my write-up on changes to the #Aggah malspam campaign which looks at their mail infrastructure, lures, targets, PowerPoint Add-In dropper and Bitcoin stealer.

In May, the attackers behind the #Aggah malicious spam campaign impersonated B2B companies in Europe, the Middle East and Asia to compromise businesses. They also adopted a PowerPoint dropper and cryptocurrency stealer. threatresearch.ext.hp.com/ag…

Alex retweeted

At present we still intend to run the event at the end of July. We are monitoring the situation and will make a final call over the coming month.


Alex retweeted
SPONSORS. We need your support. See our Sponsor Information Pack and levels available on our website. bsidesbristol.org.uk/sponsor… Let's make this happen!
Alex retweeted

Extremely informative overview of reverse engineering of “Ransomware as a Service” #Buran by @cryptogramfan @bromium for Joint @BcsForensics @owasp @OwaspCambs @ARUCyberRes “Aspects Of Digital Forensics” Workshop @AngliaRuskin @aru_fse #cambridge on Wednesday 19th Feb


The CfP for #bsidesbristol is officially open. This year we're accepting shorter talks (20 mins) as well as regular presentations (45 mins, including Q&A). If it's your first time presenting, we also have friendly mentors on hand to give advice and feedback.

Save the date... 29th and 30th July 2020 BSides Bristol is back! And our Call for Presentations is now open - get submitting! bsidesbristol.org.uk/call-fo…
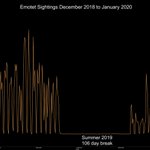
#Emotet malspam activity resumed on 13 January 2020. This festive period its actors took a 21 day break, compared with 23 days in 2018/19. cc @Cryptolaemus1 @abuse_ch

If you're interested in malware analysis & RE, I highly recommend the #Zero2Hero course by @VK_Intel and @0verfl0w_. Props to @SentinelOne for releasing ~7 hrs of content for free. It's community contributions like these that close the gap between defensive & offensive capability

Alex retweeted
Tracking Malware Campaigns Using String Metrics:
bromium.com/tracking-malware…
#malware
Here's my write-up on how to use string metrics to track malware campaigns based on email logs. I've also released a script to generate similarity link charts (graph_similar_strings.py). The screenshot is a email attachment name similarity link chart.
bromium.com/tracking-malware…
