
Cyber Security Researcher | Policy Analyst | Technical Team Member at OpenAI | @dave_aitel@mastodon.social
Joined August 2007
- Tweets94.1K
- Following1.8K
- Followers29.1K
- Likes16K





Dave Aitel retweeted

Do you know who illustrated the comic on calif.io/php2shell?
Her name is Stephanie Cortes. And her husband is the hacker who discovered php2shell: @lcfr_hax.
This artist-hacker couple has the best story, stay tuned!
elections.cordyceps.systems/… I think it's possible @ForecasterEnten is wrong about presidential popularity driving midterm votes


Dave Aitel retweeted

Amazing leadership here from the PM of Japan:

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X
Dave Aitel retweeted
This is the first time I've ever seen a site do this, the obvious simple response to a disclosure of a vulnerability without a fix: sacrifice availability to preserve safety. This option should be why we do full disclosure.

Dave Aitel retweeted

Over the past two months, we have been leading a coalition to mitigate one of the most severe bugs in open source software found in recent memory, php2shell, found as part of our Patch the Planet initiative.
Dave Aitel retweeted

OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

Readers added context they thought people might want to know
Wiz Research wasn't the first one to discover the exploit. An independent researcher first discovered it: x.com/calif_io/statu…
Dave Aitel retweeted
php2shell is the most consequential vulnerability I have ever helped discover. I am proud of how our team worked closely in coordination with the PHP Foundation to provide support and to harden the patch in preparation for this release.
Please read more about our approach:


OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…
Readers added context they thought people might want to know
Wiz Research wasn't the first one to discover the exploit. An independent researcher first discovered it: x.com/calif_io/statu…
Dave Aitel retweeted

(2) Any dislike of AI-assisted bug reports is out of place. It shouldn't matter whether an AI or a guided fuzzer found a bug; both are computational searches. Unfortunately, there are still people that reject bug reports accompanied by PoCs based on the origin in AI.
Dave Aitel retweeted
On the upside: The fact that old bugs are being discovered is a strong indicator for optimism: Old bugs are deep bugs that survived many years of code review. Finding a bunch of old bugs is the clearest indicator that technological progress in bug detecdtion is real.


Dave Aitel retweeted
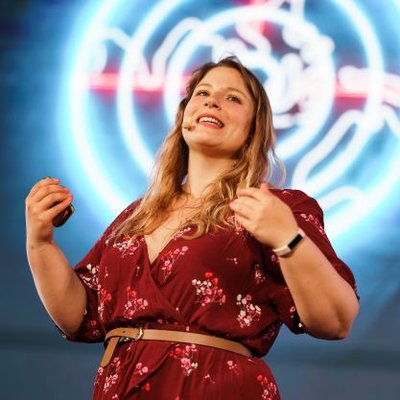
A lil personal news: Yesterday I started working at OpenAI on the cyber research team. I'm really excited to join this team of brilliant researchers and work on problems that feel really important and meaningful to me. Let the next chapter begin! 🥳🩷
RT @chrisrohlf: Reducing the attack surface of deployed services and apps is a fundamental component of software that is secure by design.…


